Turn AI Governance Policies Into Signed Audit Evidence
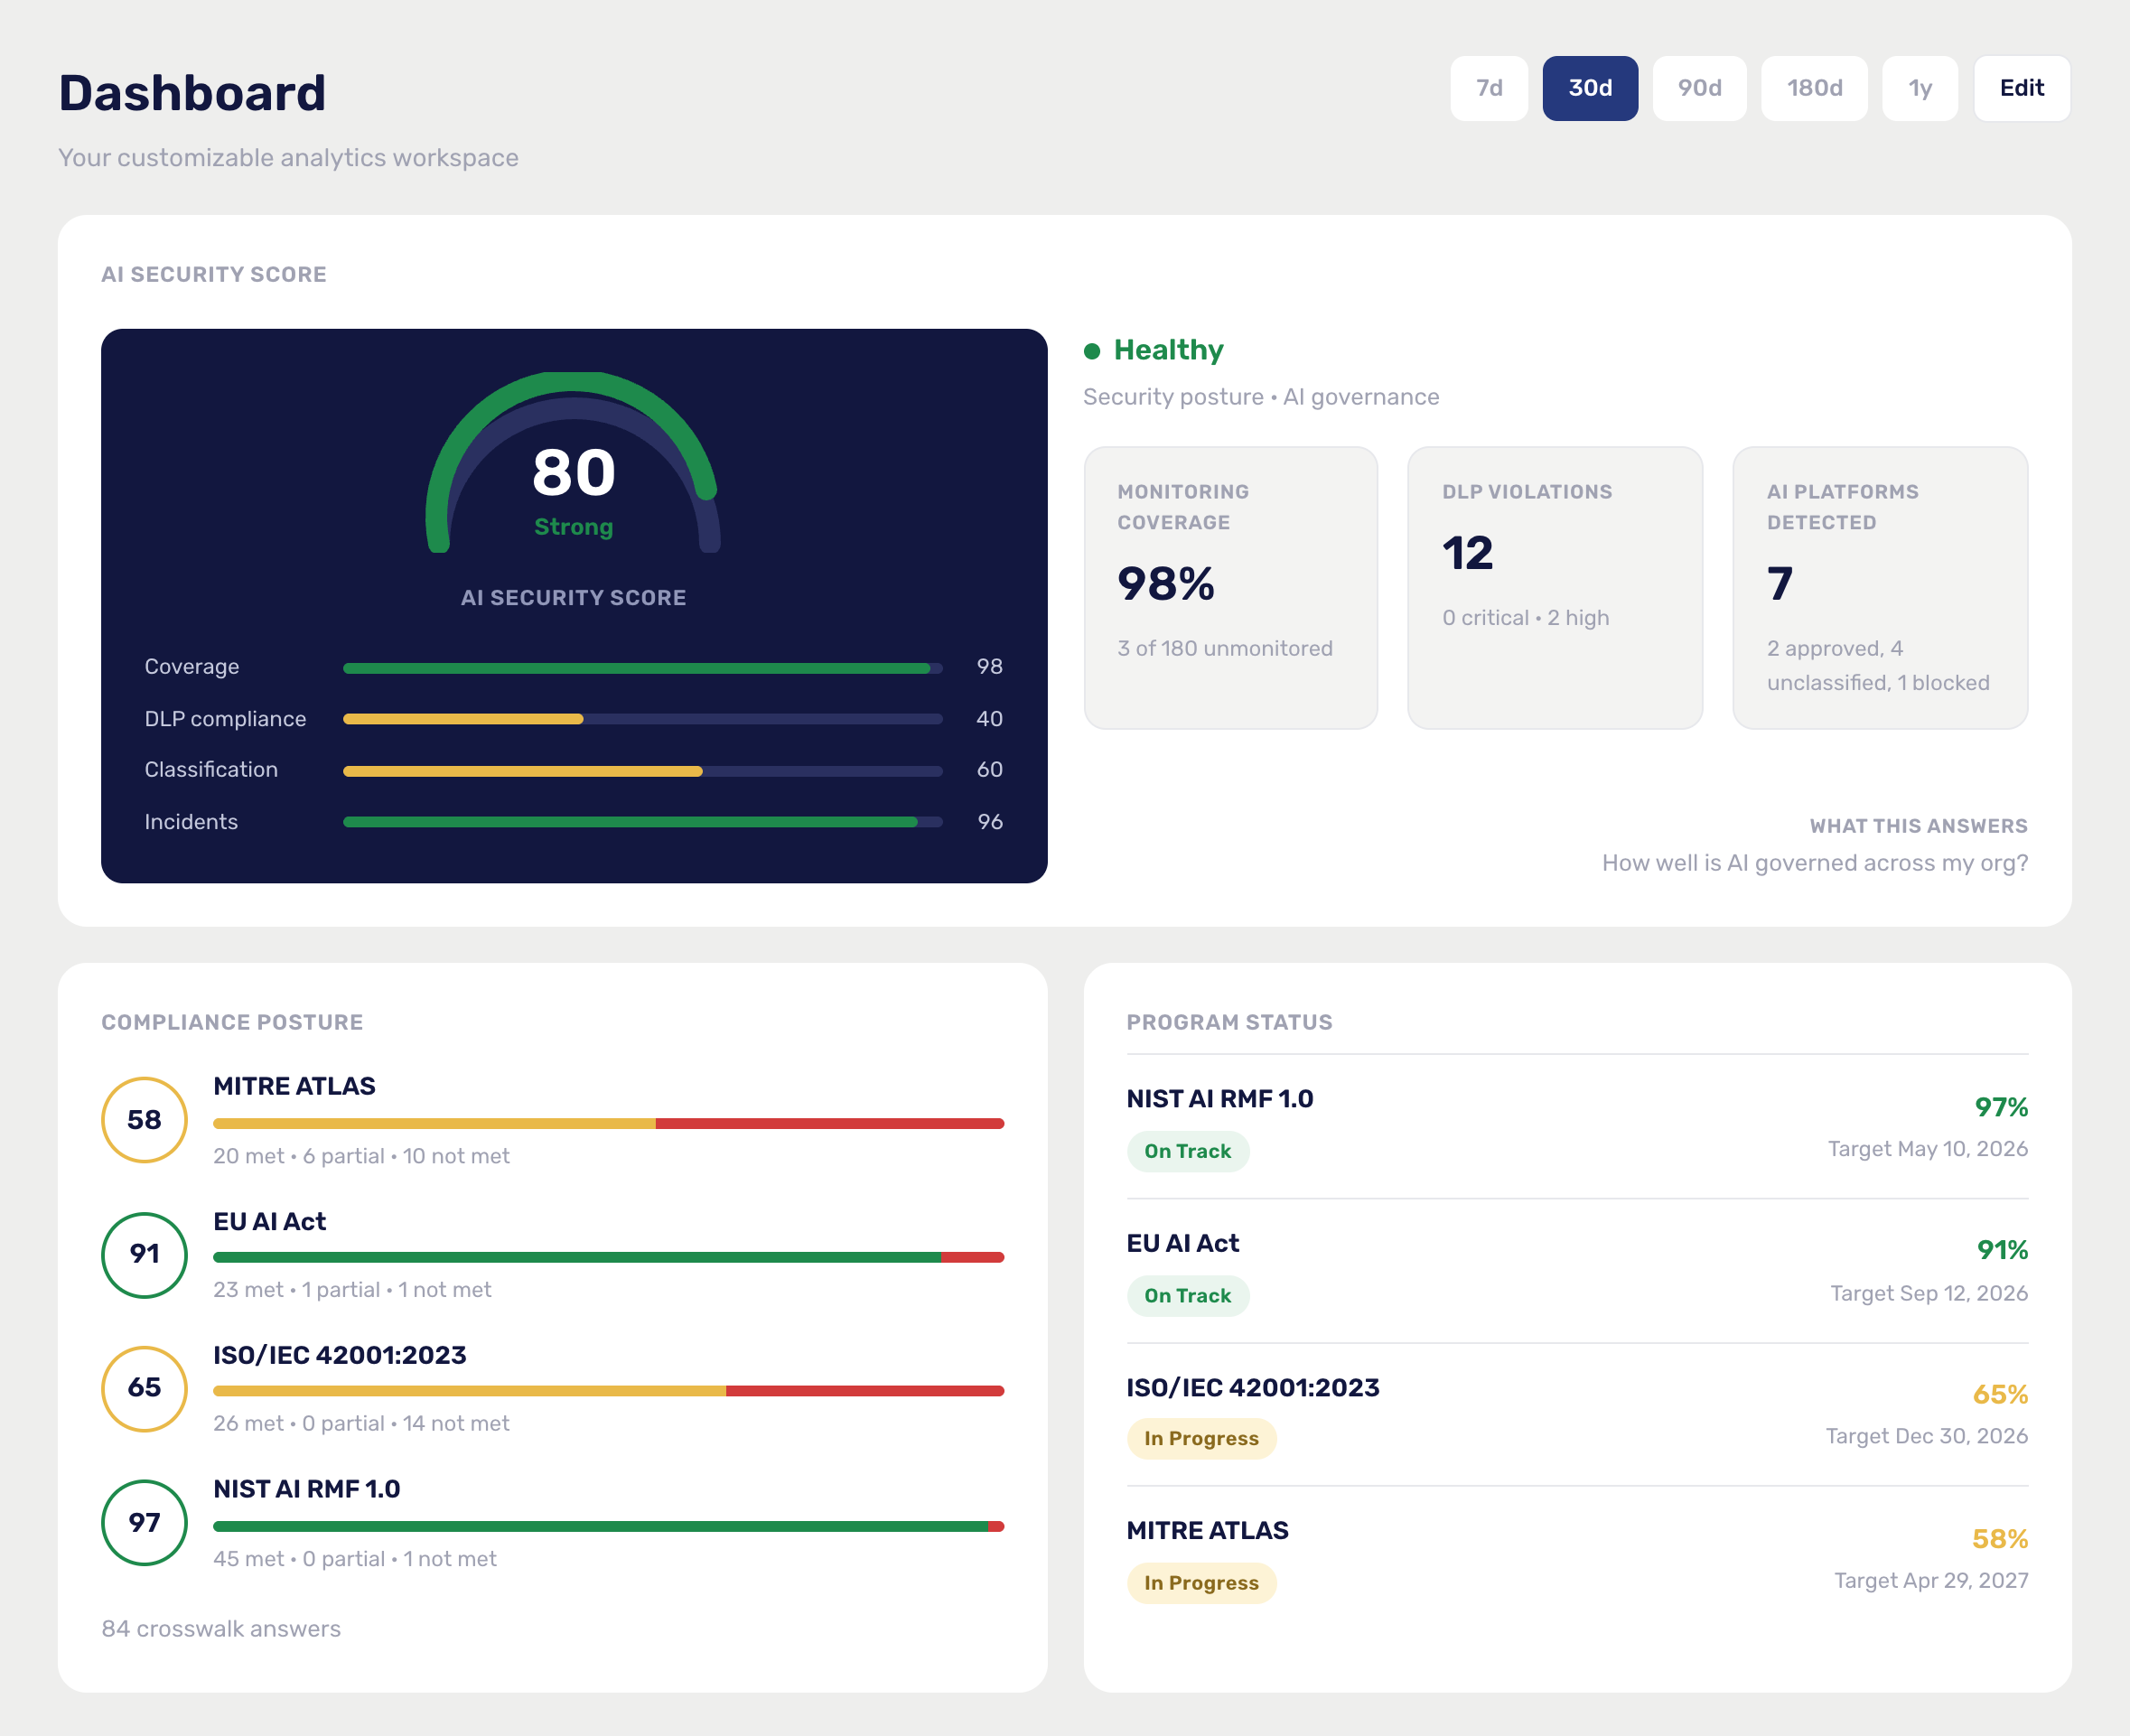
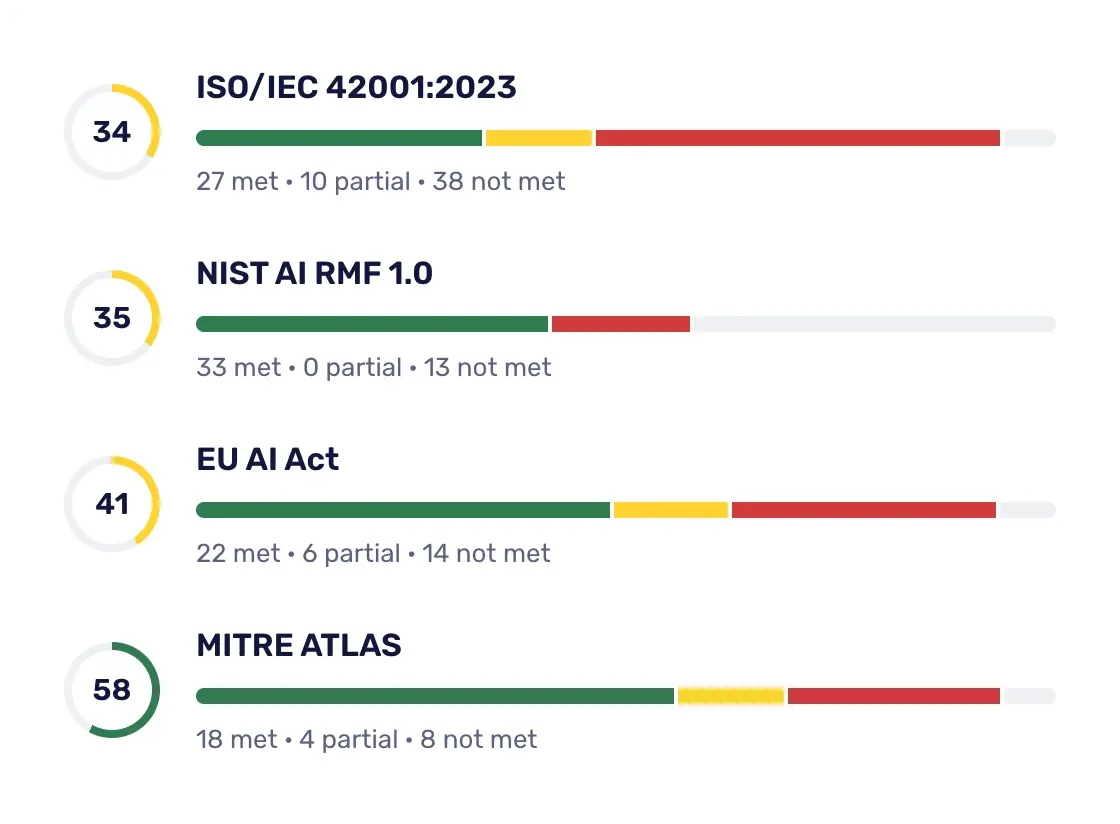
CyberHQ.ai maps findings and evidence to ISO 42001, NIST AI RMF, the EU AI Act and MITRE ATLAS, 214 controls and 101 ATLAS techniques in one place. Three-lines-of-defense workflow and signed daily evidence snapshots turn an assertion into an attestation. Scoped audit engagements bring your external auditor in.
Signed, audit-ready evidence snapshots
Live-monitored controls re-graded daily
214 controls plus 101 ATLAS techniques
214
controls mapped across three scored frameworks, plus 101 MITRE ATLAS techniques
4
frameworks: ISO 42001, NIST AI RMF, EU AI Act, & MITRE ATLAS
3
lines of defense behind every attestation
< 30 mins
to full deployment, no proxy or SSL inspection required
The Problem
An Assertion Is Not an Attestation
An auditor, a board member, or a customer security questionnaire asks how you govern AI use. The honest answer is usually a policy document, a slide, and a handful of screenshots gathered the week before the meeting. None of it is evidence. All of it is an assertion.
Traditional GRC platforms were not built to see AI usage. Nothing is watching the browser tab, the endpoint, or the AI agent that policy is supposed to govern, so the record's accuracy depends on whoever last remembered to update it. A framework gap can sit open for months before anyone notices.
For a compliance officer, the trigger is rarely abstract: an ISO 42001 or NIST AI RMF audit on the calendar, a customer questionnaire due Friday, or a board that has started asking for evidence rather than a summary. When that moment arrives, an assertion does not hold up. A signed, timestamped record does.
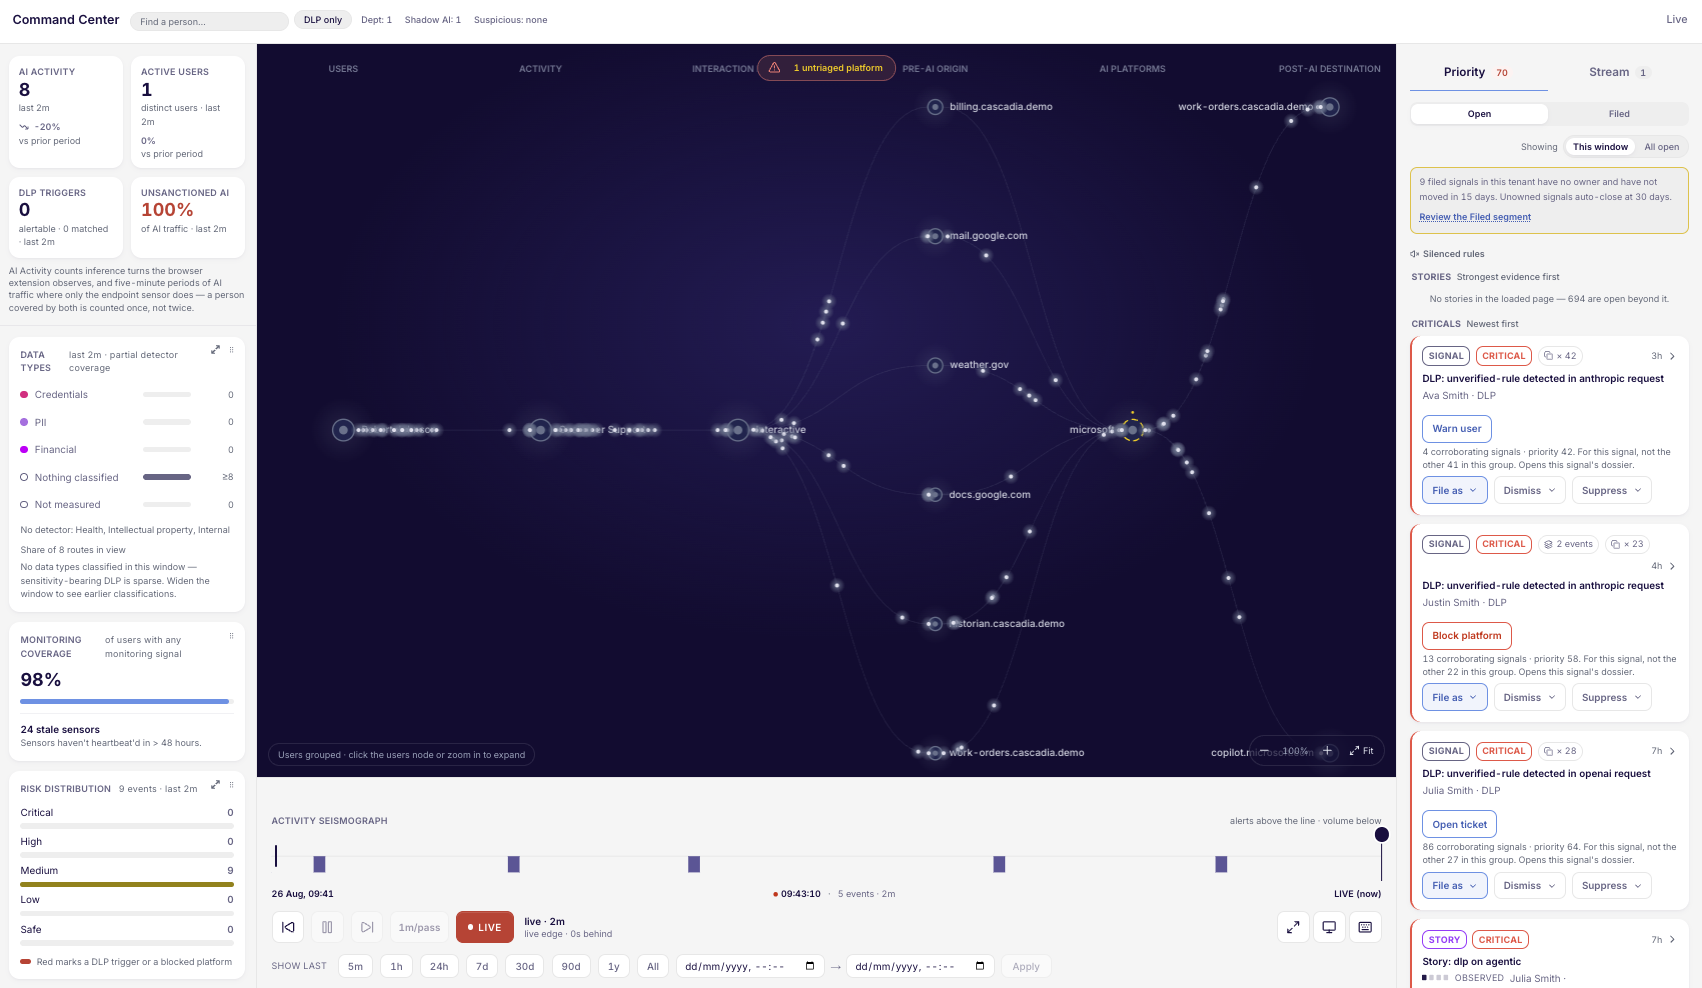
AI Security Command
What CyberHQ.ai Does Differently
Attest once, reuse it. An attestation flags suggested matches on related ISO 42001 and NIST AI RMF controls for a reviewer to accept.
See a control's real state, not a checkbox. Continuous Controls Monitoring re-grades live-monitored controls daily across five honest states, from effective to not-evidenced.
Hand the auditor an engagement, not a spreadsheet. Attestations route through first-line owners, second-line risk review, and third-line audit engagement, recorded in an append-only chain, with signed snapshots for live-monitored controls.
AI Security Command
AI Compliance & Audit
Three capabilities that turn a policy document into a control map an auditor can actually verify.
Four-framework control mapping
Maps findings and evidence to ISO 42001, NIST AI RMF, EU AI Act, and MITRE ATLAS.
Continuous controls monitoring
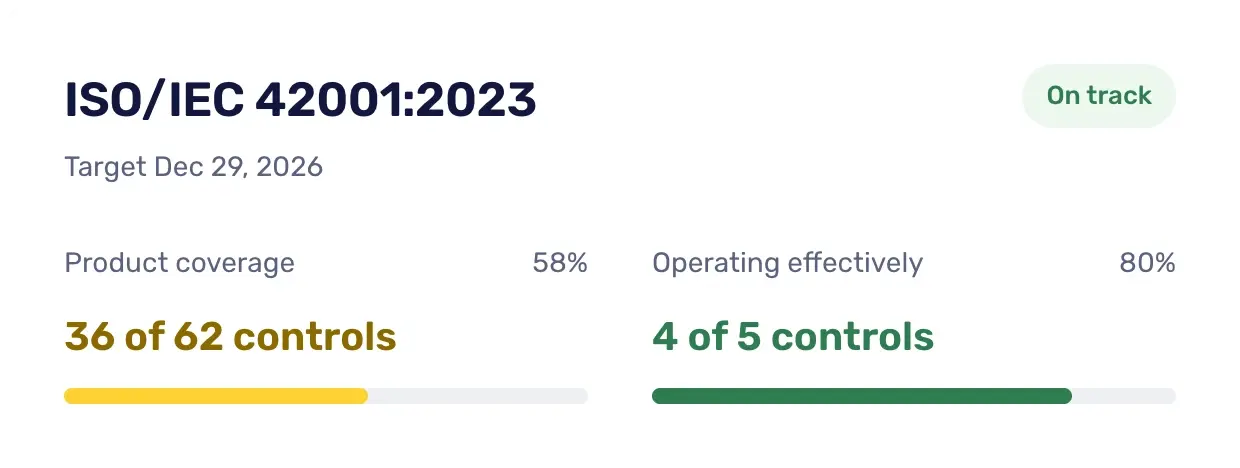
Re-grades live-monitored controls daily across five honest states, from effective to not-evidenced, instead of a single pass or fail.
Three-lines-of-defense workflow
Routes every attestation through first-line owners, second-line risk review, and third-line audit engagement, recorded in an append-only chain, with signed snapshots for live-monitored controls.
AI Usage Insights
AI Usage Insights Within 48hrs Of Deployment
Start a free 30-day trial and see results on your insights dashboard within 48 hours of deploying your sensor.
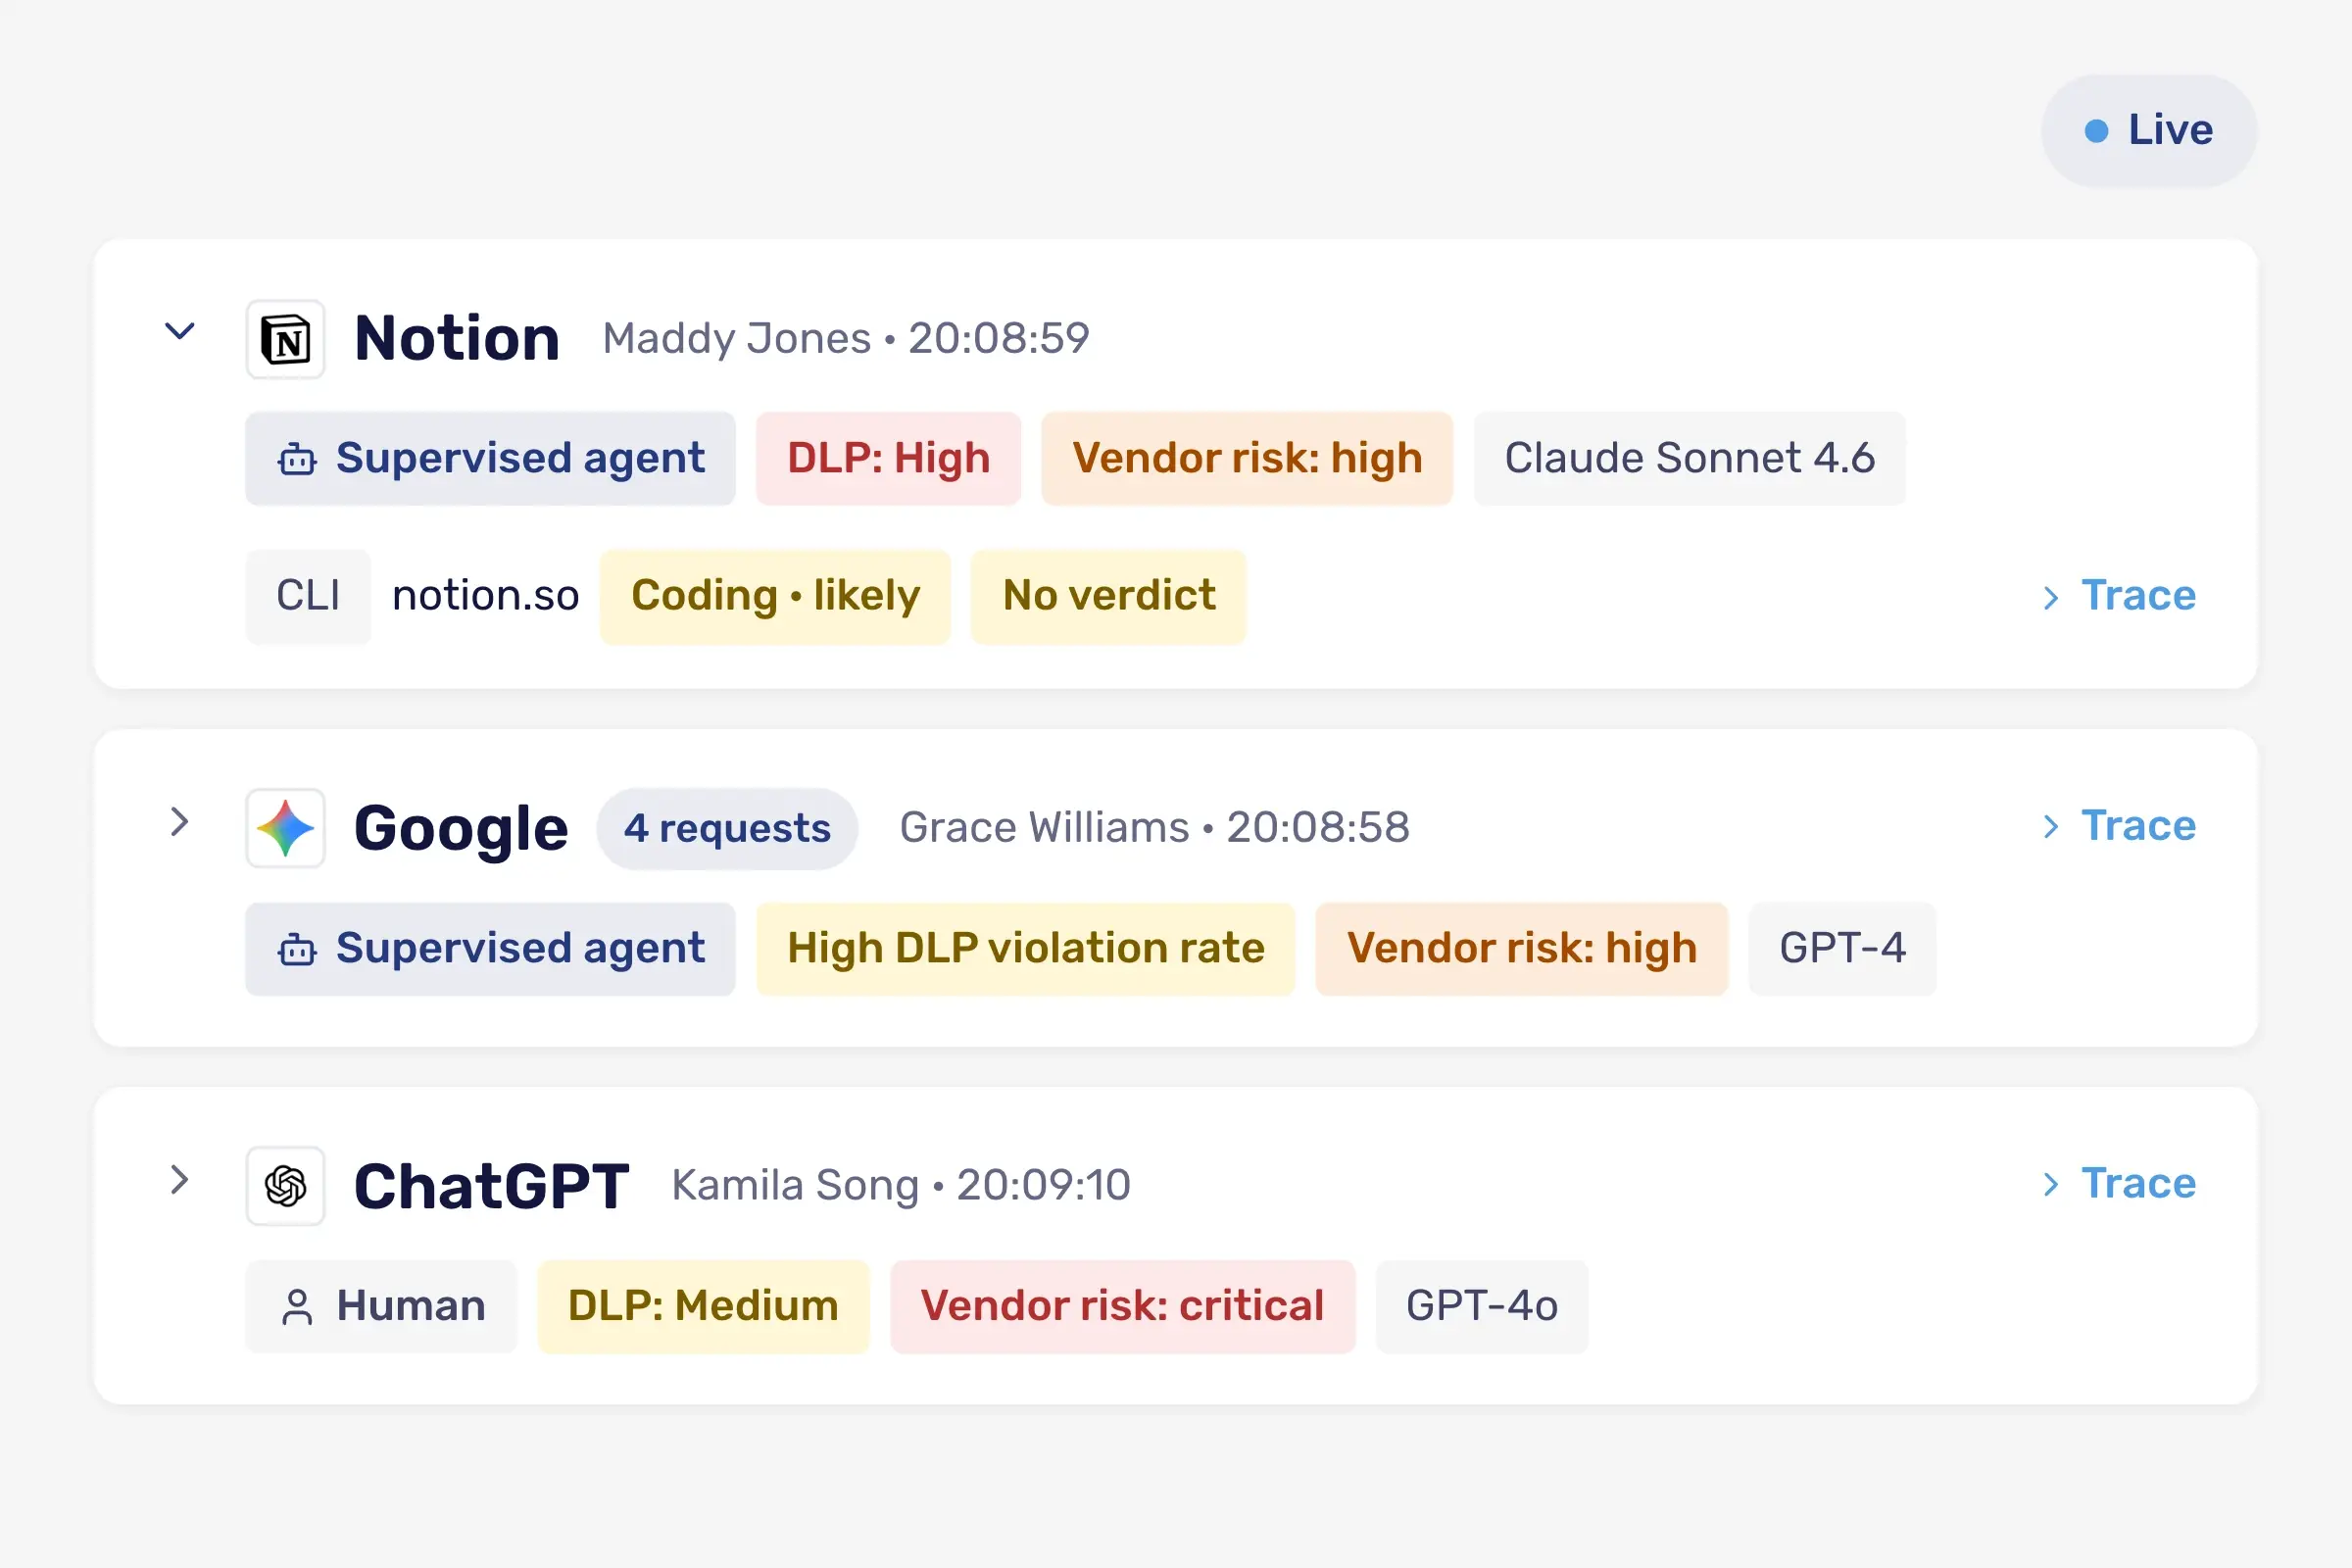
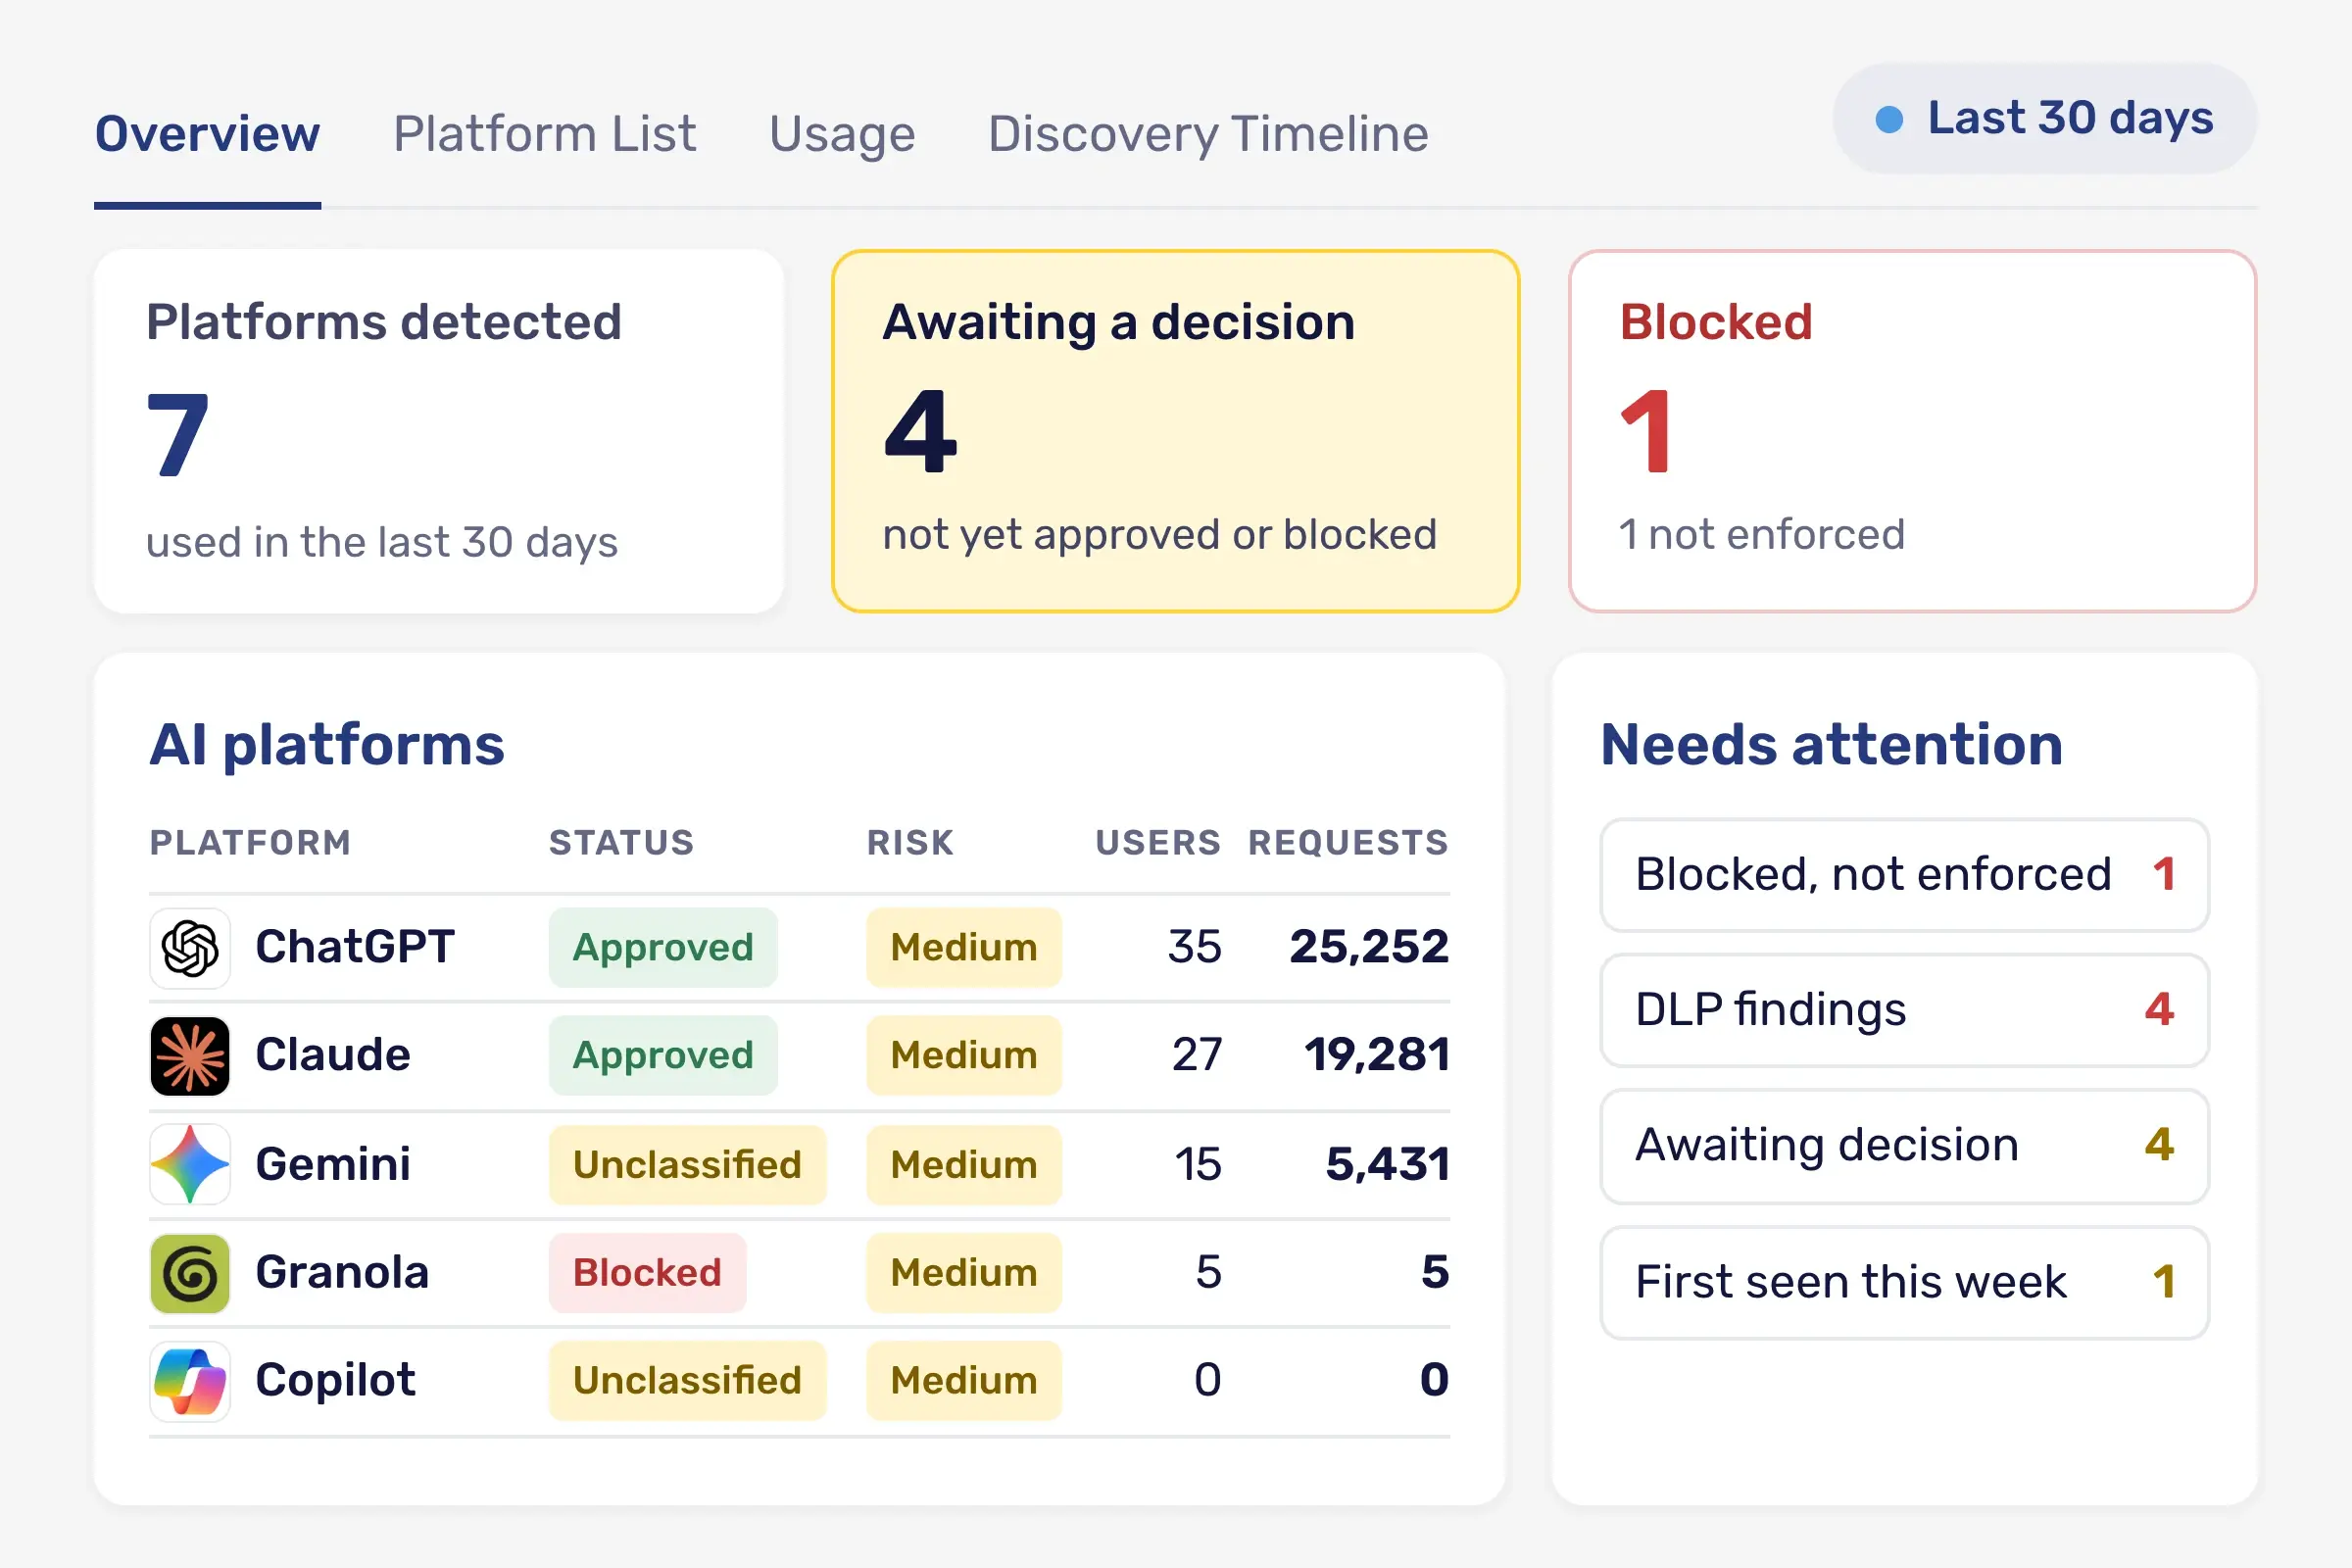
What AI tools are moving through your organization
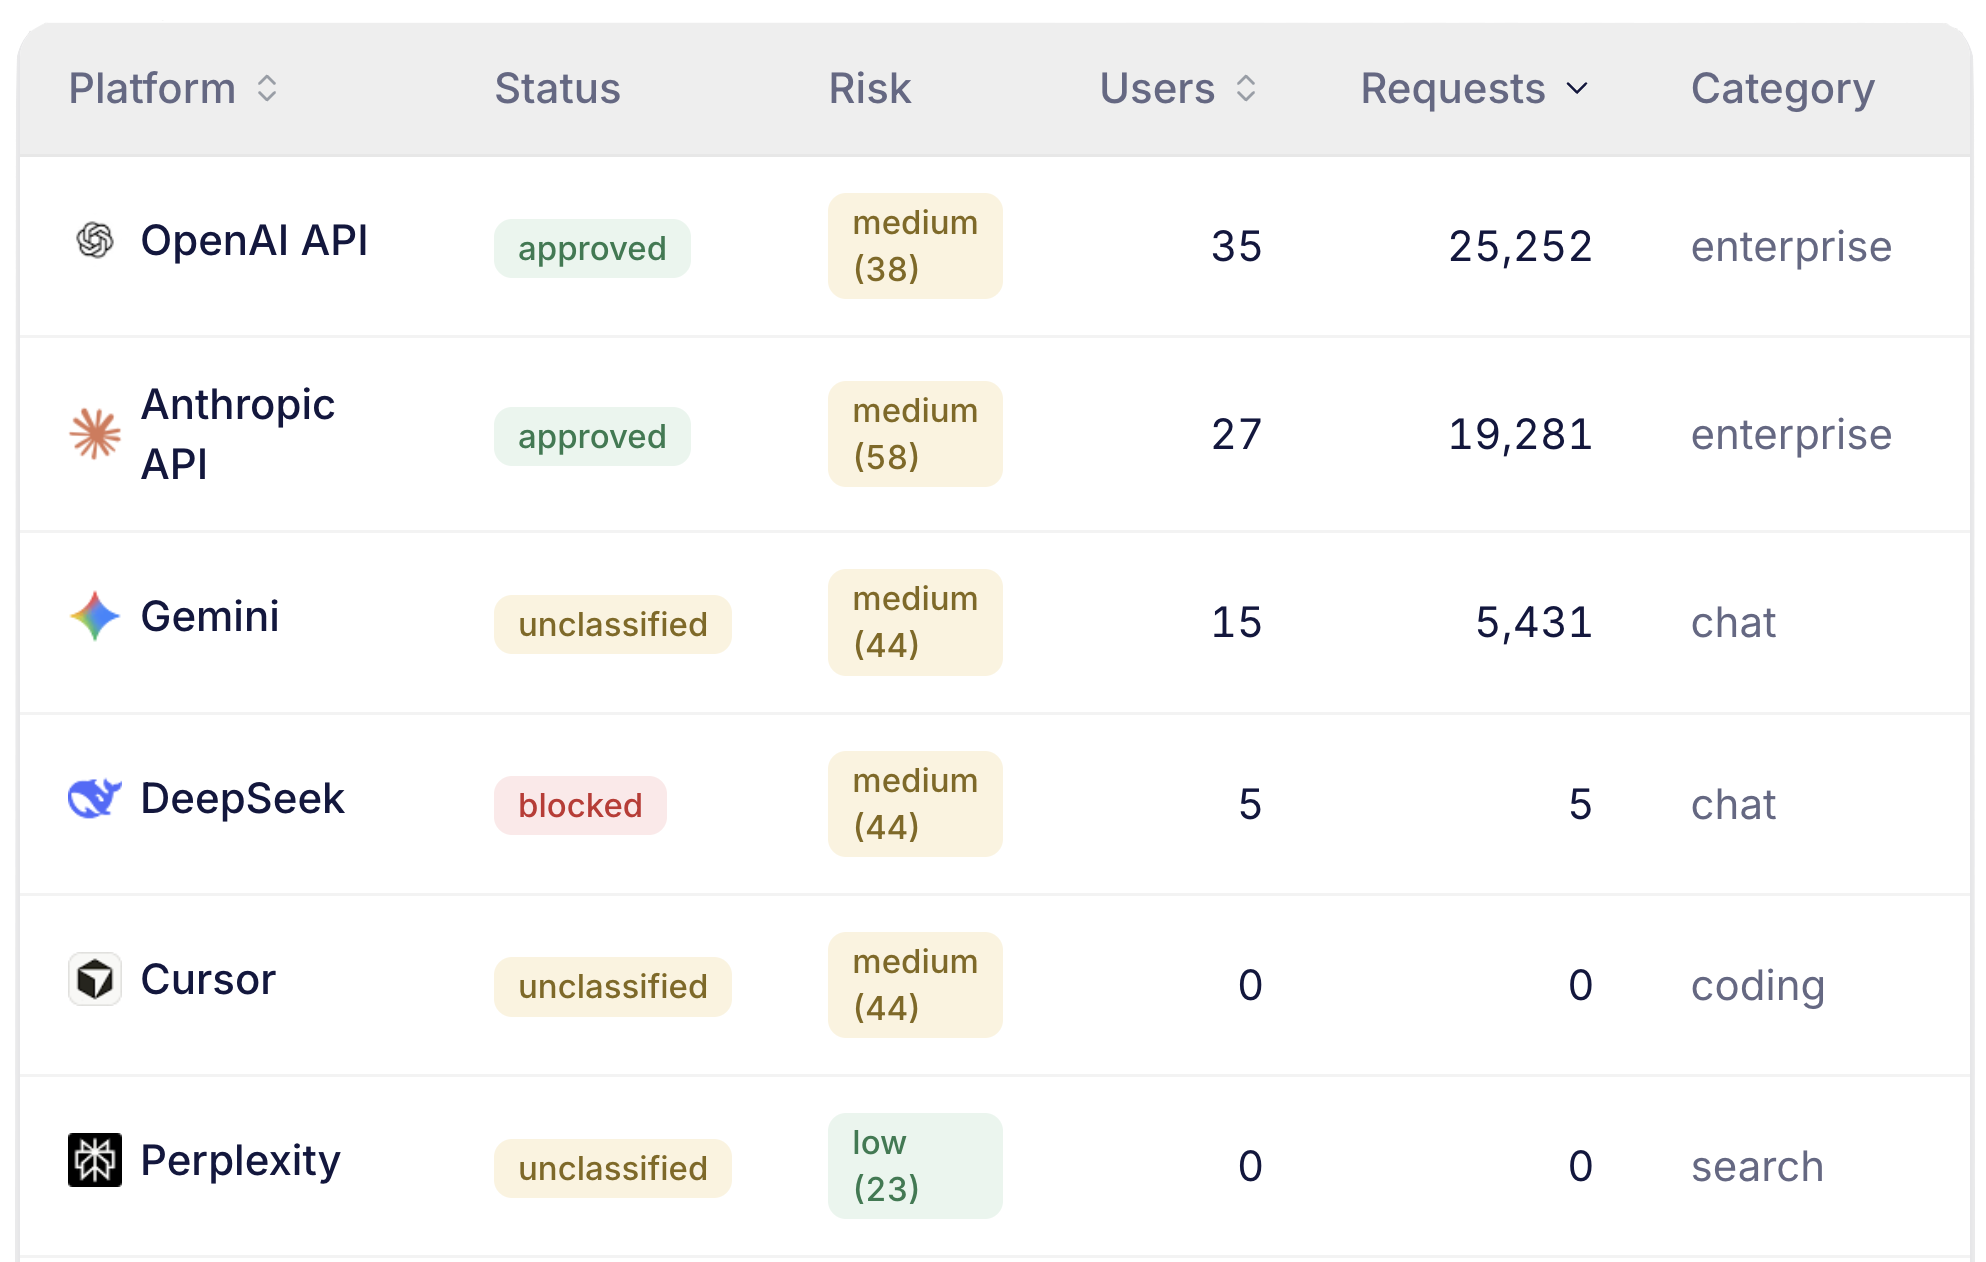
Who is using AI and how they are using it
How agentic AI is acting and what it's accessing
Which AI tools are putting your data at risk and why
Start your 30-day free trial
CyberHQ.ai Does Not Replace Your Tools
A Control You Cannot Prove Is Not a Control.
CyberHQ.ai is not a replacement for CyberHQ or a traditional GRC platform. It is the live monitoring layer that feeds it real evidence, the piece traditional GRC tools were never built to generate on their own.
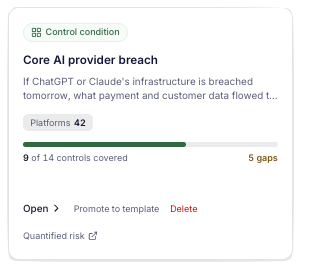
CyberHQ.ai raises a framework-gap signal whenever a control is assessed as not met, partial, or unassessed, so a gap cannot sit open unnoticed.
Where a control has audit-grade machine evidence but no attestation, CyberHQ.ai drafts a nightly attestation suggestion (requires a connected AI provider), so a first-line owner starts from a draft, not a blank page.
Exports a Statement of Applicability as a PDF and gives an external auditor a properly isolated portal of their own.
ISO 42001, NIST AI RMF, the EU AI Act and MITRE ATLAS, 214 controls across the three scored frameworks, 167 of them individually assessable, plus 101 MITRE ATLAS adversarial machine learning techniques tracked separately.
Can I grant access to CyberHQ.ai to an external auditor?
Yes. On the Prove tier, each audit runs as a scoped engagement in an audit engagement with properly isolated access, sampling requests, ITGC panels, and auditor challenges, alongside a Statement of Applicability PDF export, so an audit does not depend on someone assembling evidence by hand.
What does Continuous Controls Monitoring actually grade?
Live-monitored controls are re-graded daily across five honest operating states: effective, operating-with-gaps, implemented-not-effective, not-implemented, or not-evidenced, instead of a single pass or fail. A control can also be marked out-of-scope, not applicable, waived, or covered by a compensating control without forcing it red.
Which tier includes the three-lines-of-defense workflow and audit engagements?
The three-lines-of-defense workflow starts at Act; audit engagements are Prove. See gives you continuous shadow AI discovery, actor classification, and coverage gap detection. Act adds your AI Security Score, alert triage, custom DLP rules, incident response workflow, and compliance attestation with the three-lines-of-defense workflow and Statement of Applicability export. Prove adds readiness programs, audit engagements for external auditors, attack simulation, and AI-agent governance. If a compliance deadline, an upcoming audit, or agents already running in your environment is what brought you here, Prove is the tier built for that.
What is a three-lines-of-defense workflow?
It routes an attestation through first-line control owners, second-line risk review, and third-line audit engagement, recorded in an append-only chain, with signed evidence snapshots for live-monitored controls, so an auditor can verify what was recorded and when.
What is an AI Security Command Platform?
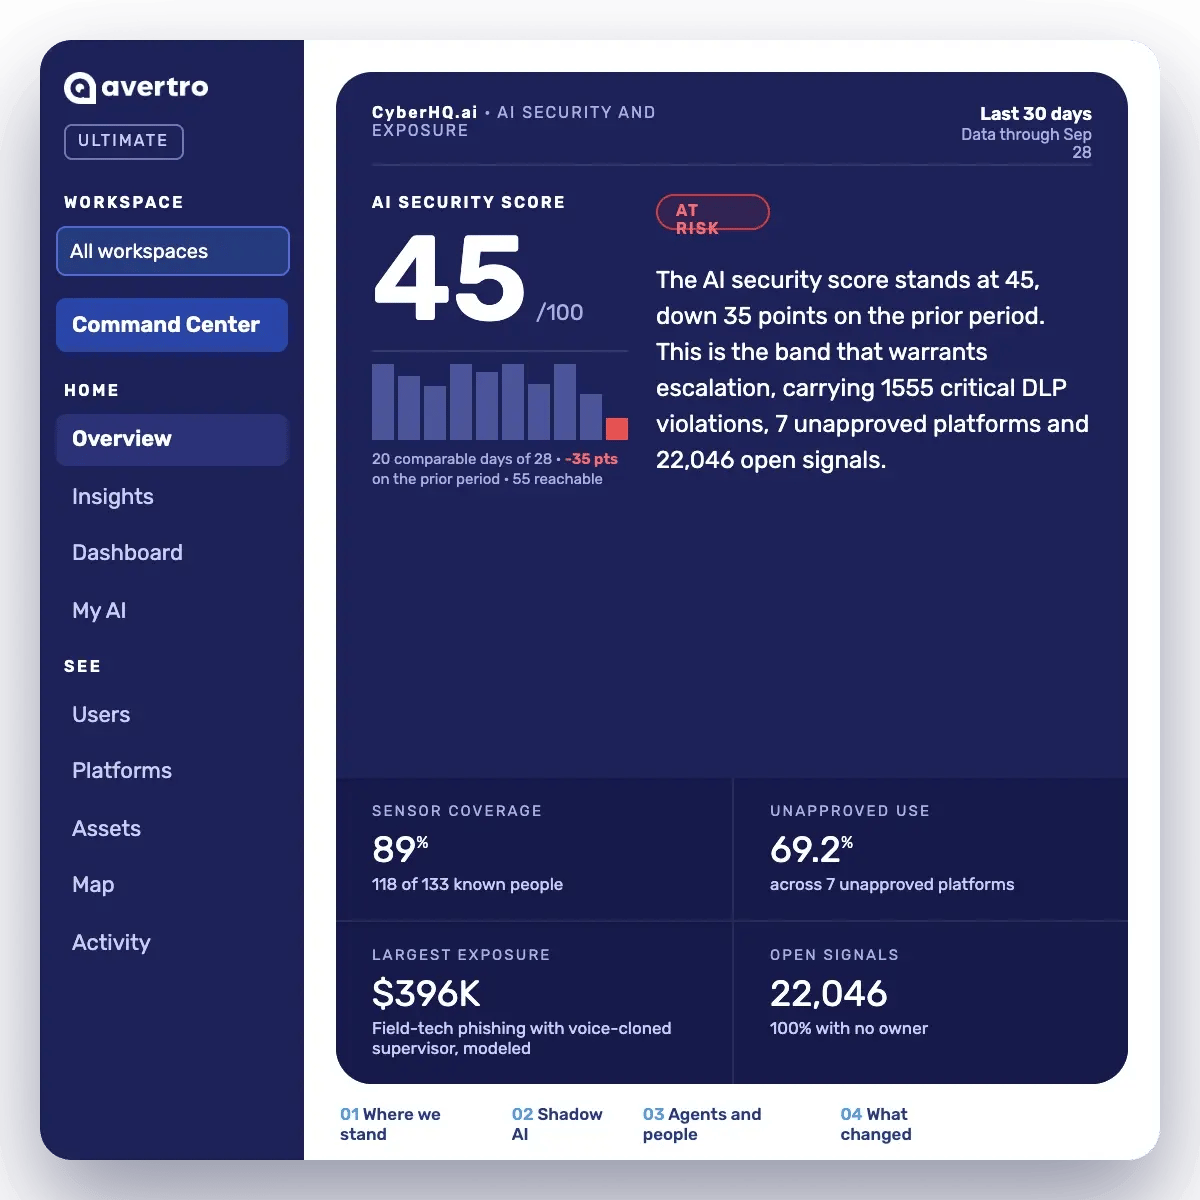
An AI Security Command Platform gives a business a continuous, evidence-backed picture of how AI is actually being used across the organization, from first shadow AI discovery through data protection, agent oversight, and audit-ready compliance. CyberHQ.ai is built to sit alongside your existing security stack, not replace it, and to answer three questions on an ongoing basis: how is AI being used right now, what does that usage expose you to, and can you prove you have control.
CyberHQ.ai
Turn Your AI Governance Activity Into Audit Ready Evidence
Trial CyberHQ.ai free for 30 days. Get meaningful insights within the first 48 hours.