Skip to content

CyberHQ.ai - See

See every AI tool Moving in through your organization

Your employees are already using ChatGPT, Claude, Gemini, Copilot, and dozens more. CyberHQ.ai shows you which ones, what data is moving through them, and where to look first, in under thirty minutes.

CyberHQ.ai
LIVE
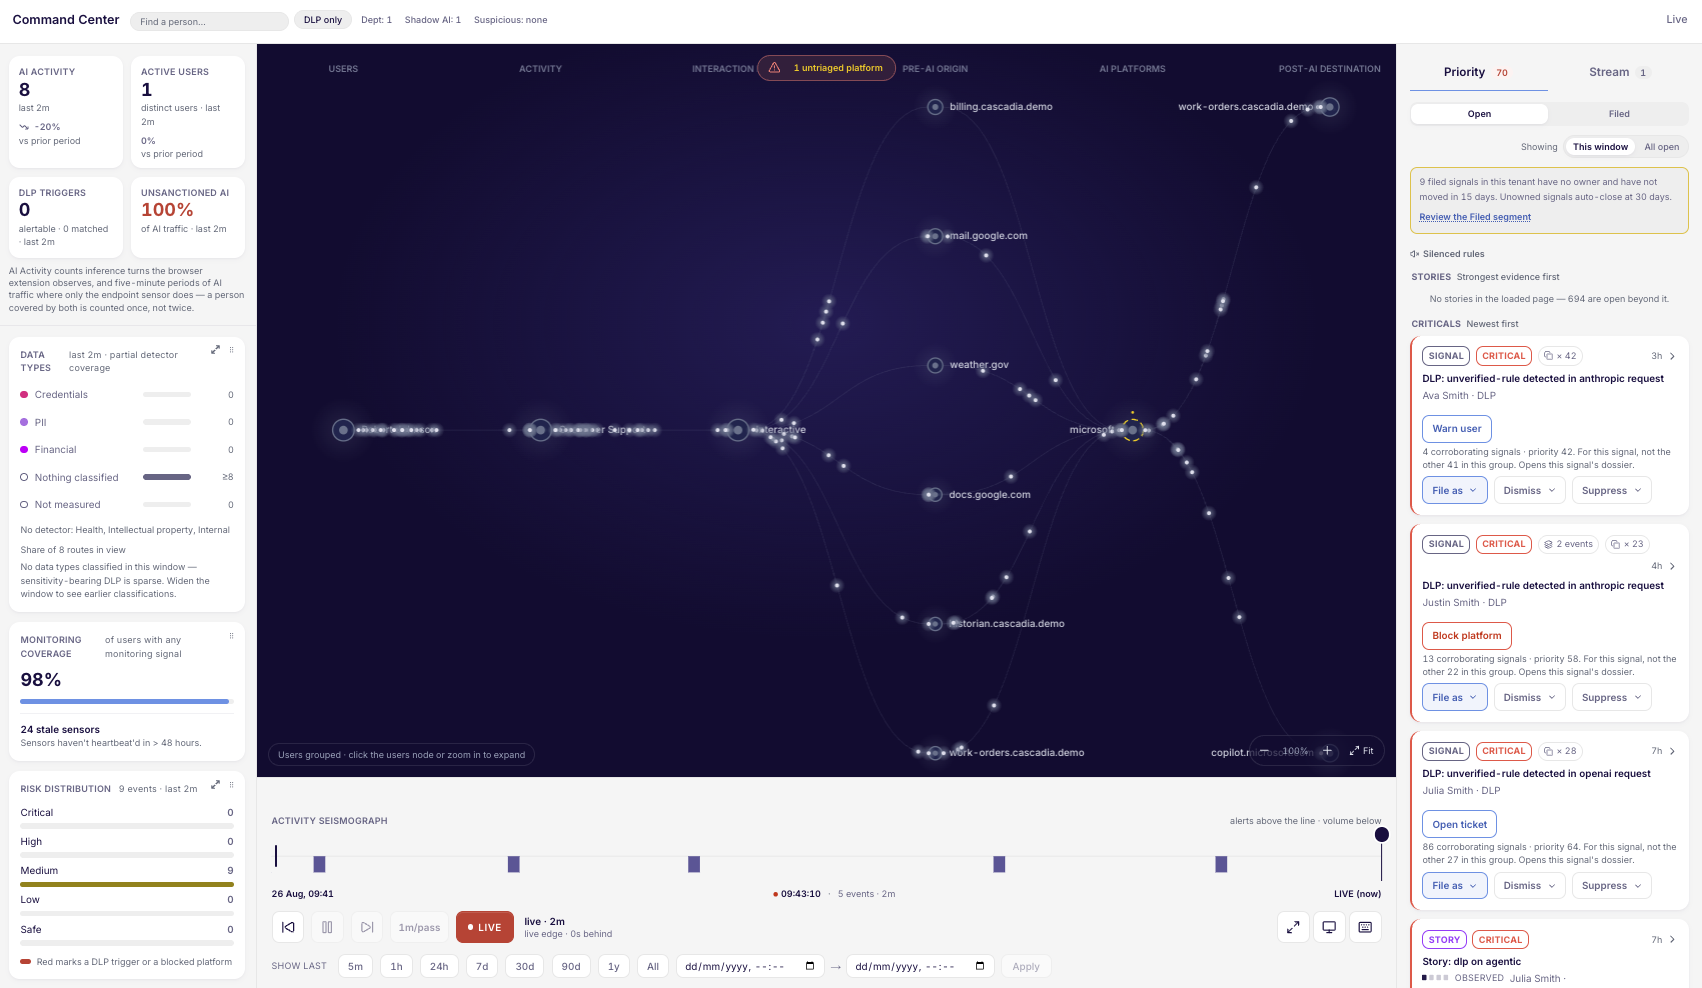
AI Activity
328
↑ 18% vs prior
Active Users
54
↑ 6% vs prior
DLP Triggers
12
7 matched
Unsanctioned AI
89%
of AI traffic
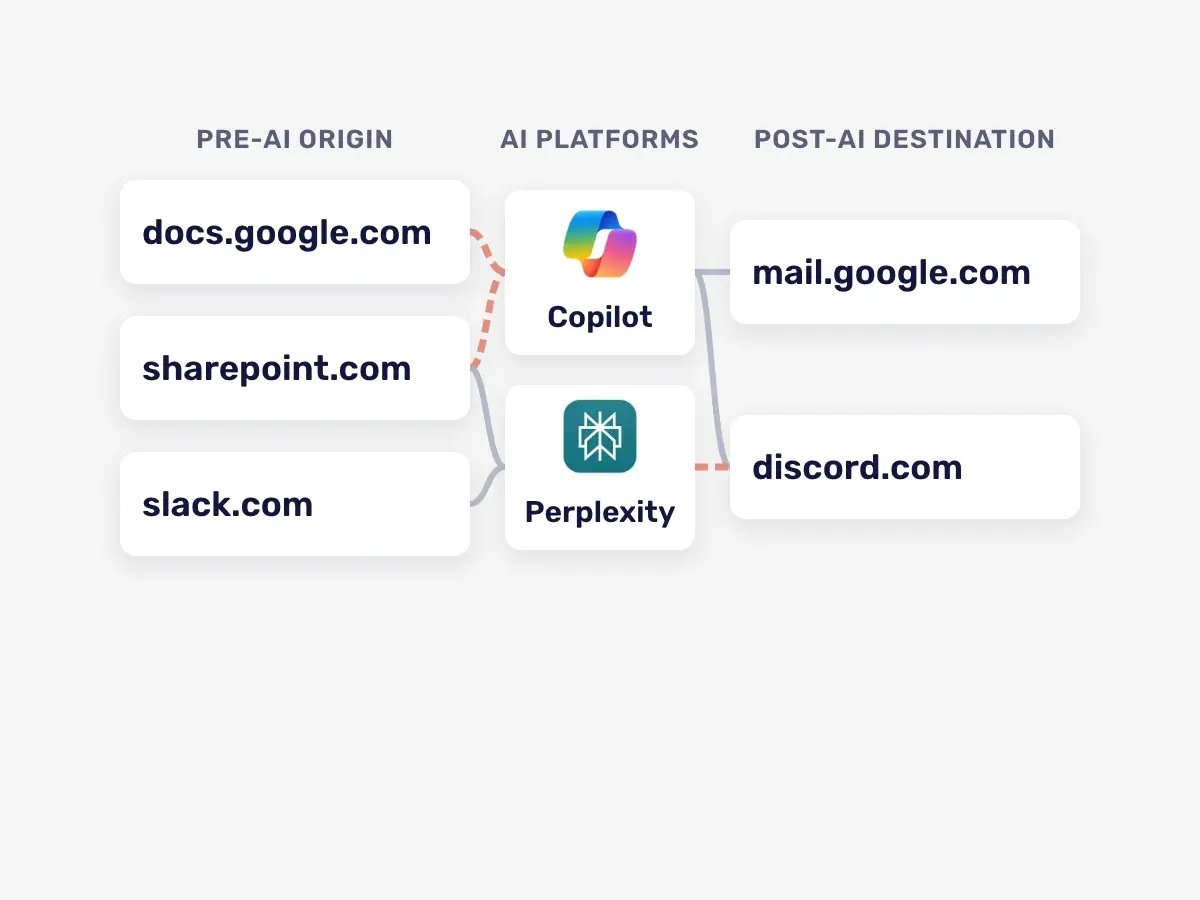
USERS ACTIVITY INTERACTION PRE-AI ORIGIN AI PLATFORMS POST-AI DESTINATION 1 grouped activity Interactive mail.google.com weather.gov docs.google.com historian.cascadia.demo work-orders.cascadia.demo AI platform 1 untriaged assistant work-orders.cascadia.demo flagged critical ai-platform.example.com
standard telemetry untriaged platform flagged critical path
20–40 %

More AI tools found in use than IT expected

40 +

AI providers monitored on a continuously expanding watchlist

< 30 mins

to full deployment, no proxy or SSL inspection required

< 48 hrs

to first meaningful finding

The Problem

The AI Blind Spot


Every week, a leader restricts AI tools across their organization. Not because AI lacks value, but because they cannot see what their people are doing with it, cannot act when something goes wrong, and cannot prove to a board or an auditor that it is under control.

Ask your security team these questions and see how many they can answer with evidence instead of a guess.

Which AI tools are our people actually using, beyond what IT approved?

What data are they sending into those tools right now?

Who is actually using AI to do real work, and who isn’t using it at all?

Which sessions are real people, and which are AI agents acting on their own?

CASB, DLP, and secure web gateways were built for documents and email, not AI model context or agent activity.

The result? AI adoption that arrived through the browser, one person at a time, unseen, unowned, and unpriced.

CyberHQ.ai

AI Blindness vs AI Visibility With CyberHQ.ai

Most organizations manage AI risk by assuming it isn't happening where they can't see it. CyberHQ.ai replaces the assumption with evidence.

Without AI Visibility With CyberHQ.AI
Security teams can say which AI tools are approved. They cannot say which ones people are actually using.
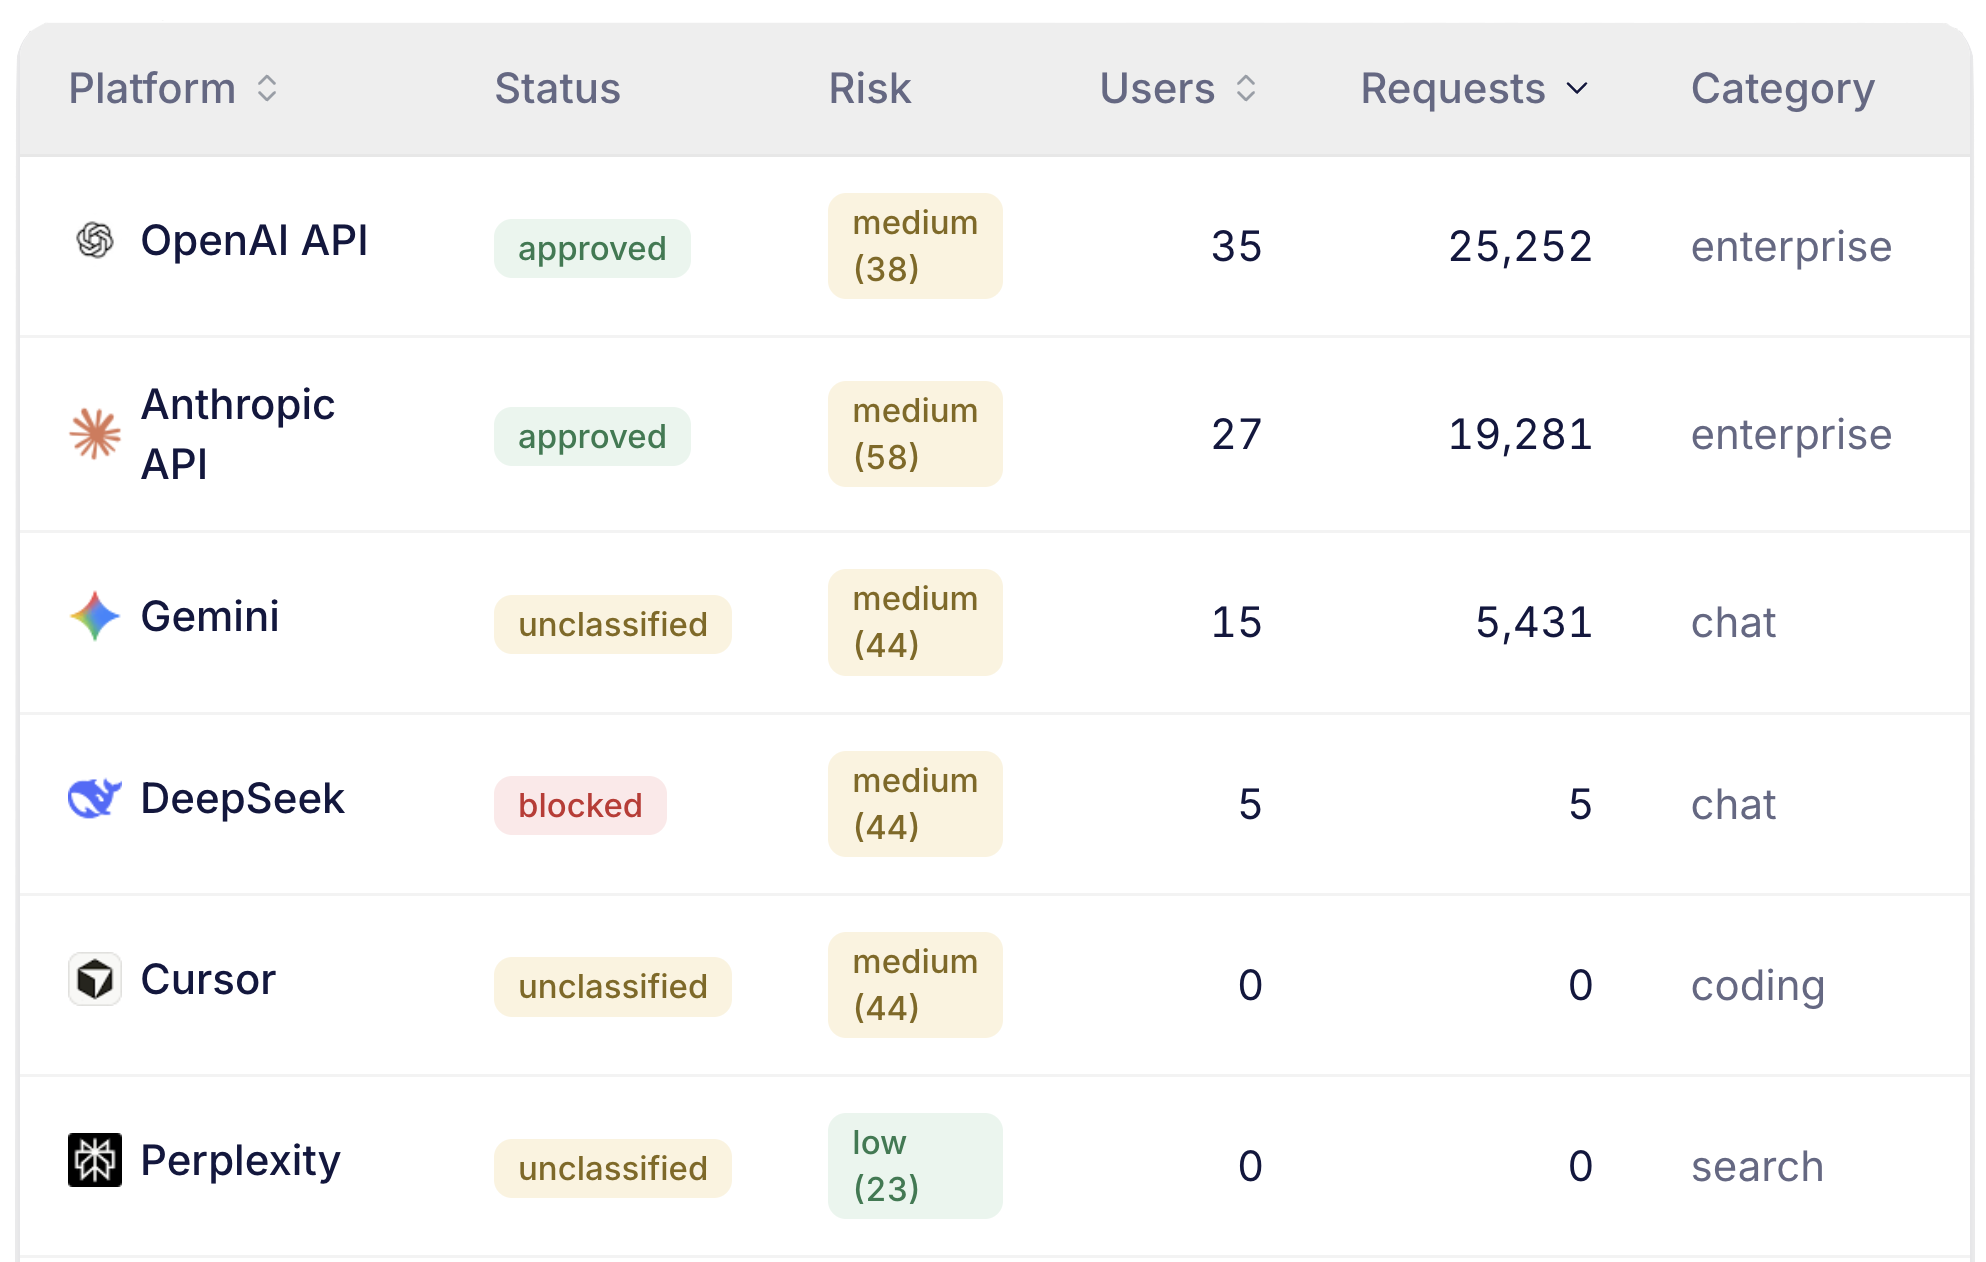
Shadow AI discovery surfaces AI platforms in use, sanctioned or not, across a continuously expanding watchlist of 38 AI providers, as soon as anyone touches them.
AI adoption happens one person, one browser tab, at a time, with no one watching.
A browser extension and native endpoint sensor cover AI activity in the browser and beyond, including activity from desktop apps like Cursor and Claude Desktop that never open a browser.
Nobody knows what data left the organization through an AI prompt until something goes wrong.
Data flow monitoring shows where information moves into and out of AI, alerting you to potential risks and areas for optimization.
The board asks about AI governance and gets an anecdote, not a metric.
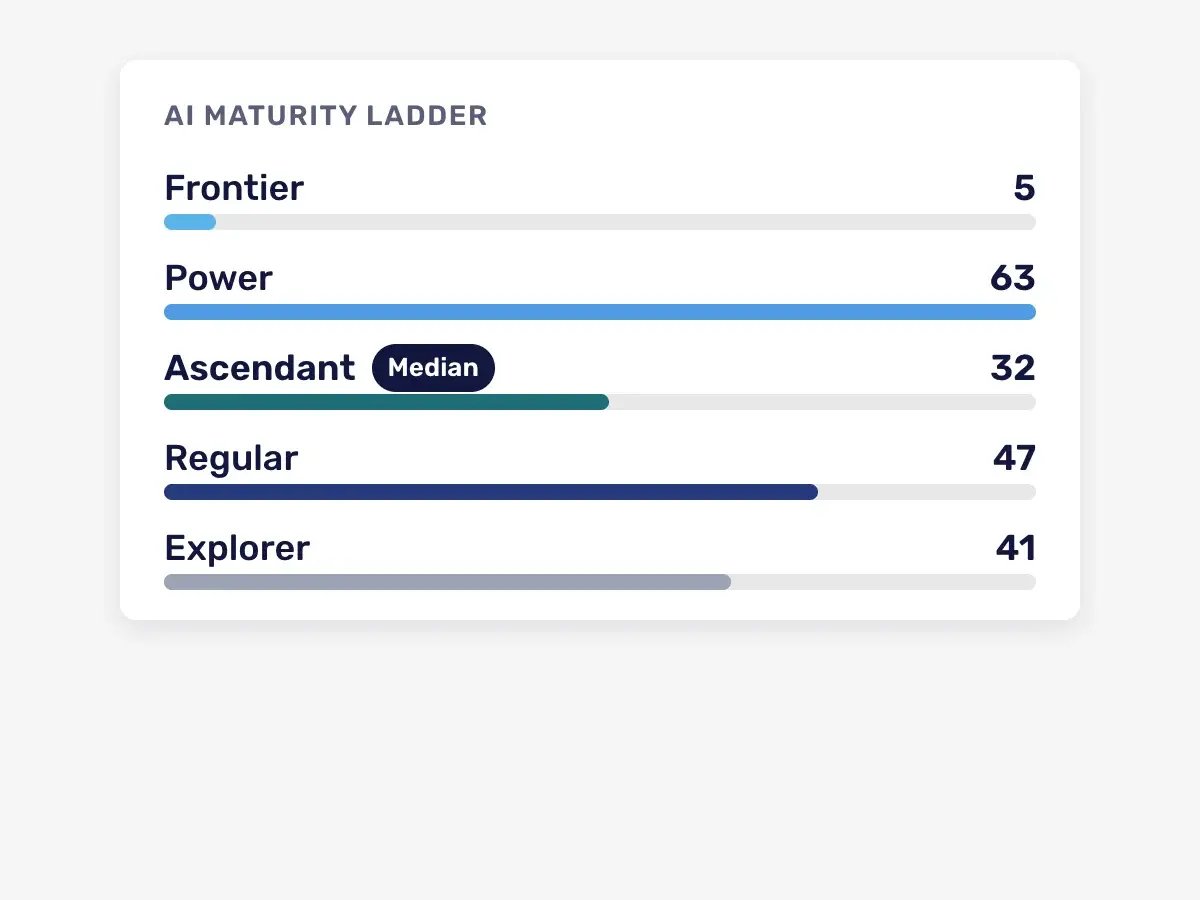
The AI Maturity Ladder turns real usage into a board-ready view of adoption, ranking every active user from Explorer to Frontier, exportable as a PDF from day one.
Finding out how many AI tools are really in use takes a survey, a spreadsheet, and a few weeks.
Deployment takes minutes, no proxy, no SSL inspection, with first meaningful findings within 24 to 48 hours.
Nobody can say which employees are actually being monitored and which slipped through.
Coverage gap detection flags people using AI without full browser extension or endpoint sensor coverage, in one prioritized view.Beta

How CyberHQ.ai sees everything

One Continuous Picture

See-where-data-flows (2)

See where your data actually flows

See where data flows into and out of AI tools to identify risk and areas for improvement rather than reacting to incidents.

See-AI-maturity-ladder (2)

How mature your AI adoption really is

A board-ready view of who is getting real value from AI and who hasn't started, built from actual usage rather than a survey.

AI Usage Insights

AI Usage Insights Within 48hrs Of Deployment

Start a free 30-day trial and see results on your insights dashboard within 48 hours of deploying your sensor.

What AI tools are moving through your organization

Who is using AI and how they are using it

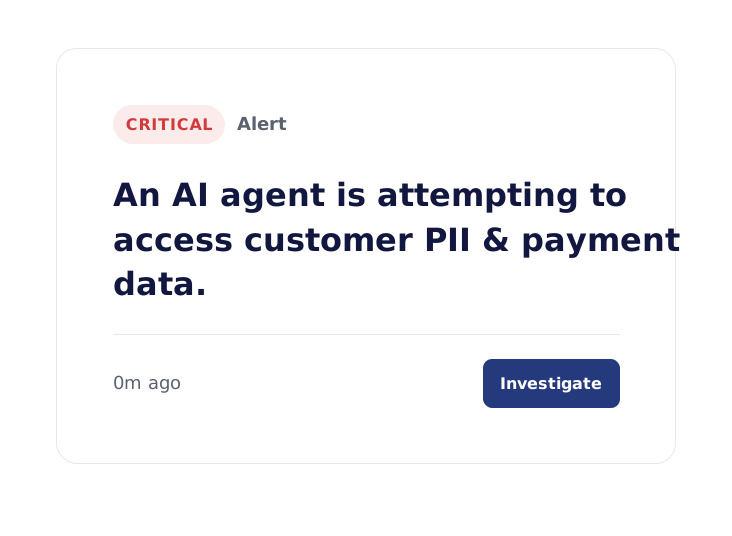
How agentic AI is acting and what it's accessing

Which AI tools are putting your data at risk and why

Start your 30-day free trial

ai-usage-dashboard

Built For AI Stakeholders

Every Function Has a Different
AI Question

Operations

Which sessions are people and which are AI agents?

Every session classified as interactive human use, human-supervised agentic use, or fully autonomous agentic use, continuously, as activity arrives.

Data & AI

What is actually deployed, not what was approved?

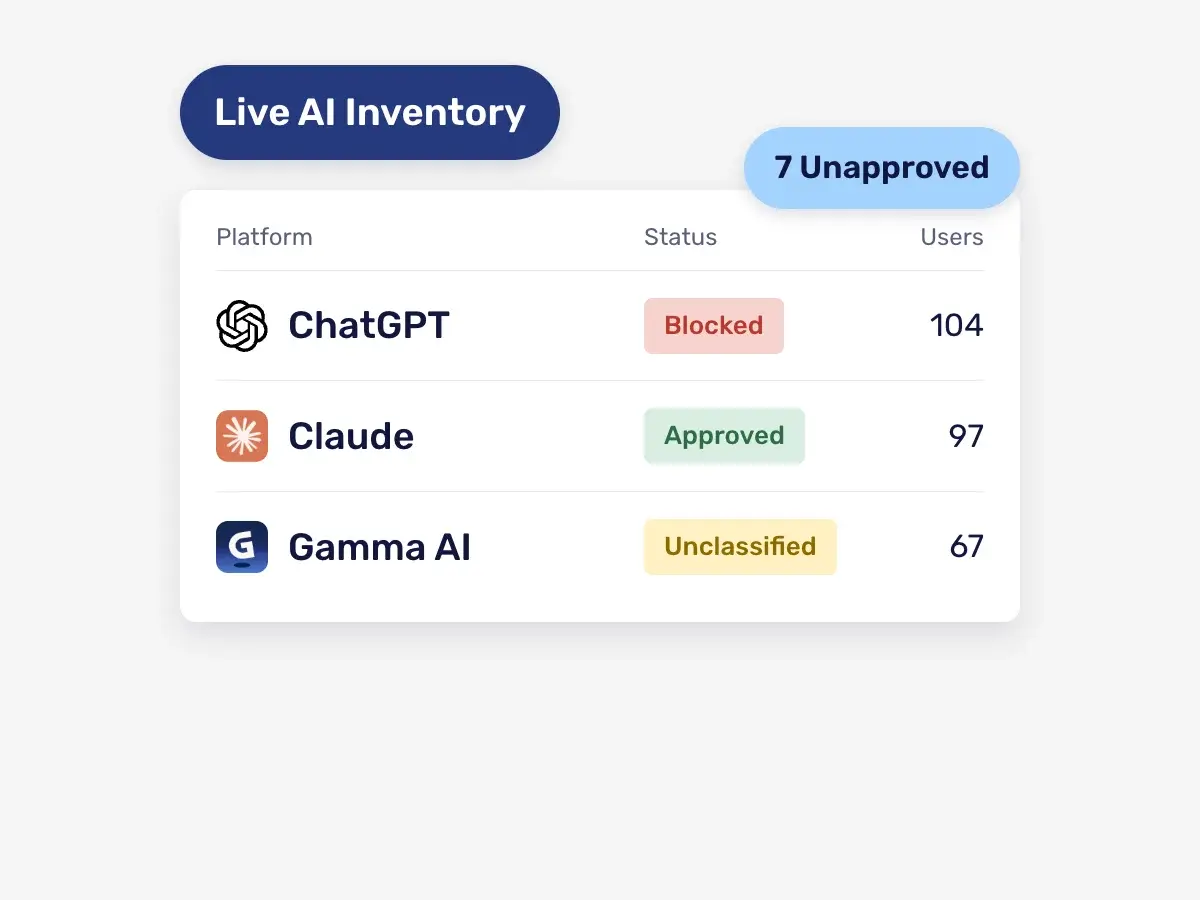
A continuous inventory of every AI tool in use, and how well your teams are using it.

Finance

Is your AI spend actually paying off?

Is AI actually paying off? See which departments get real value, with a modeled estimate of time saved built from verified prompt turns, not raw event counts.

Security & IT

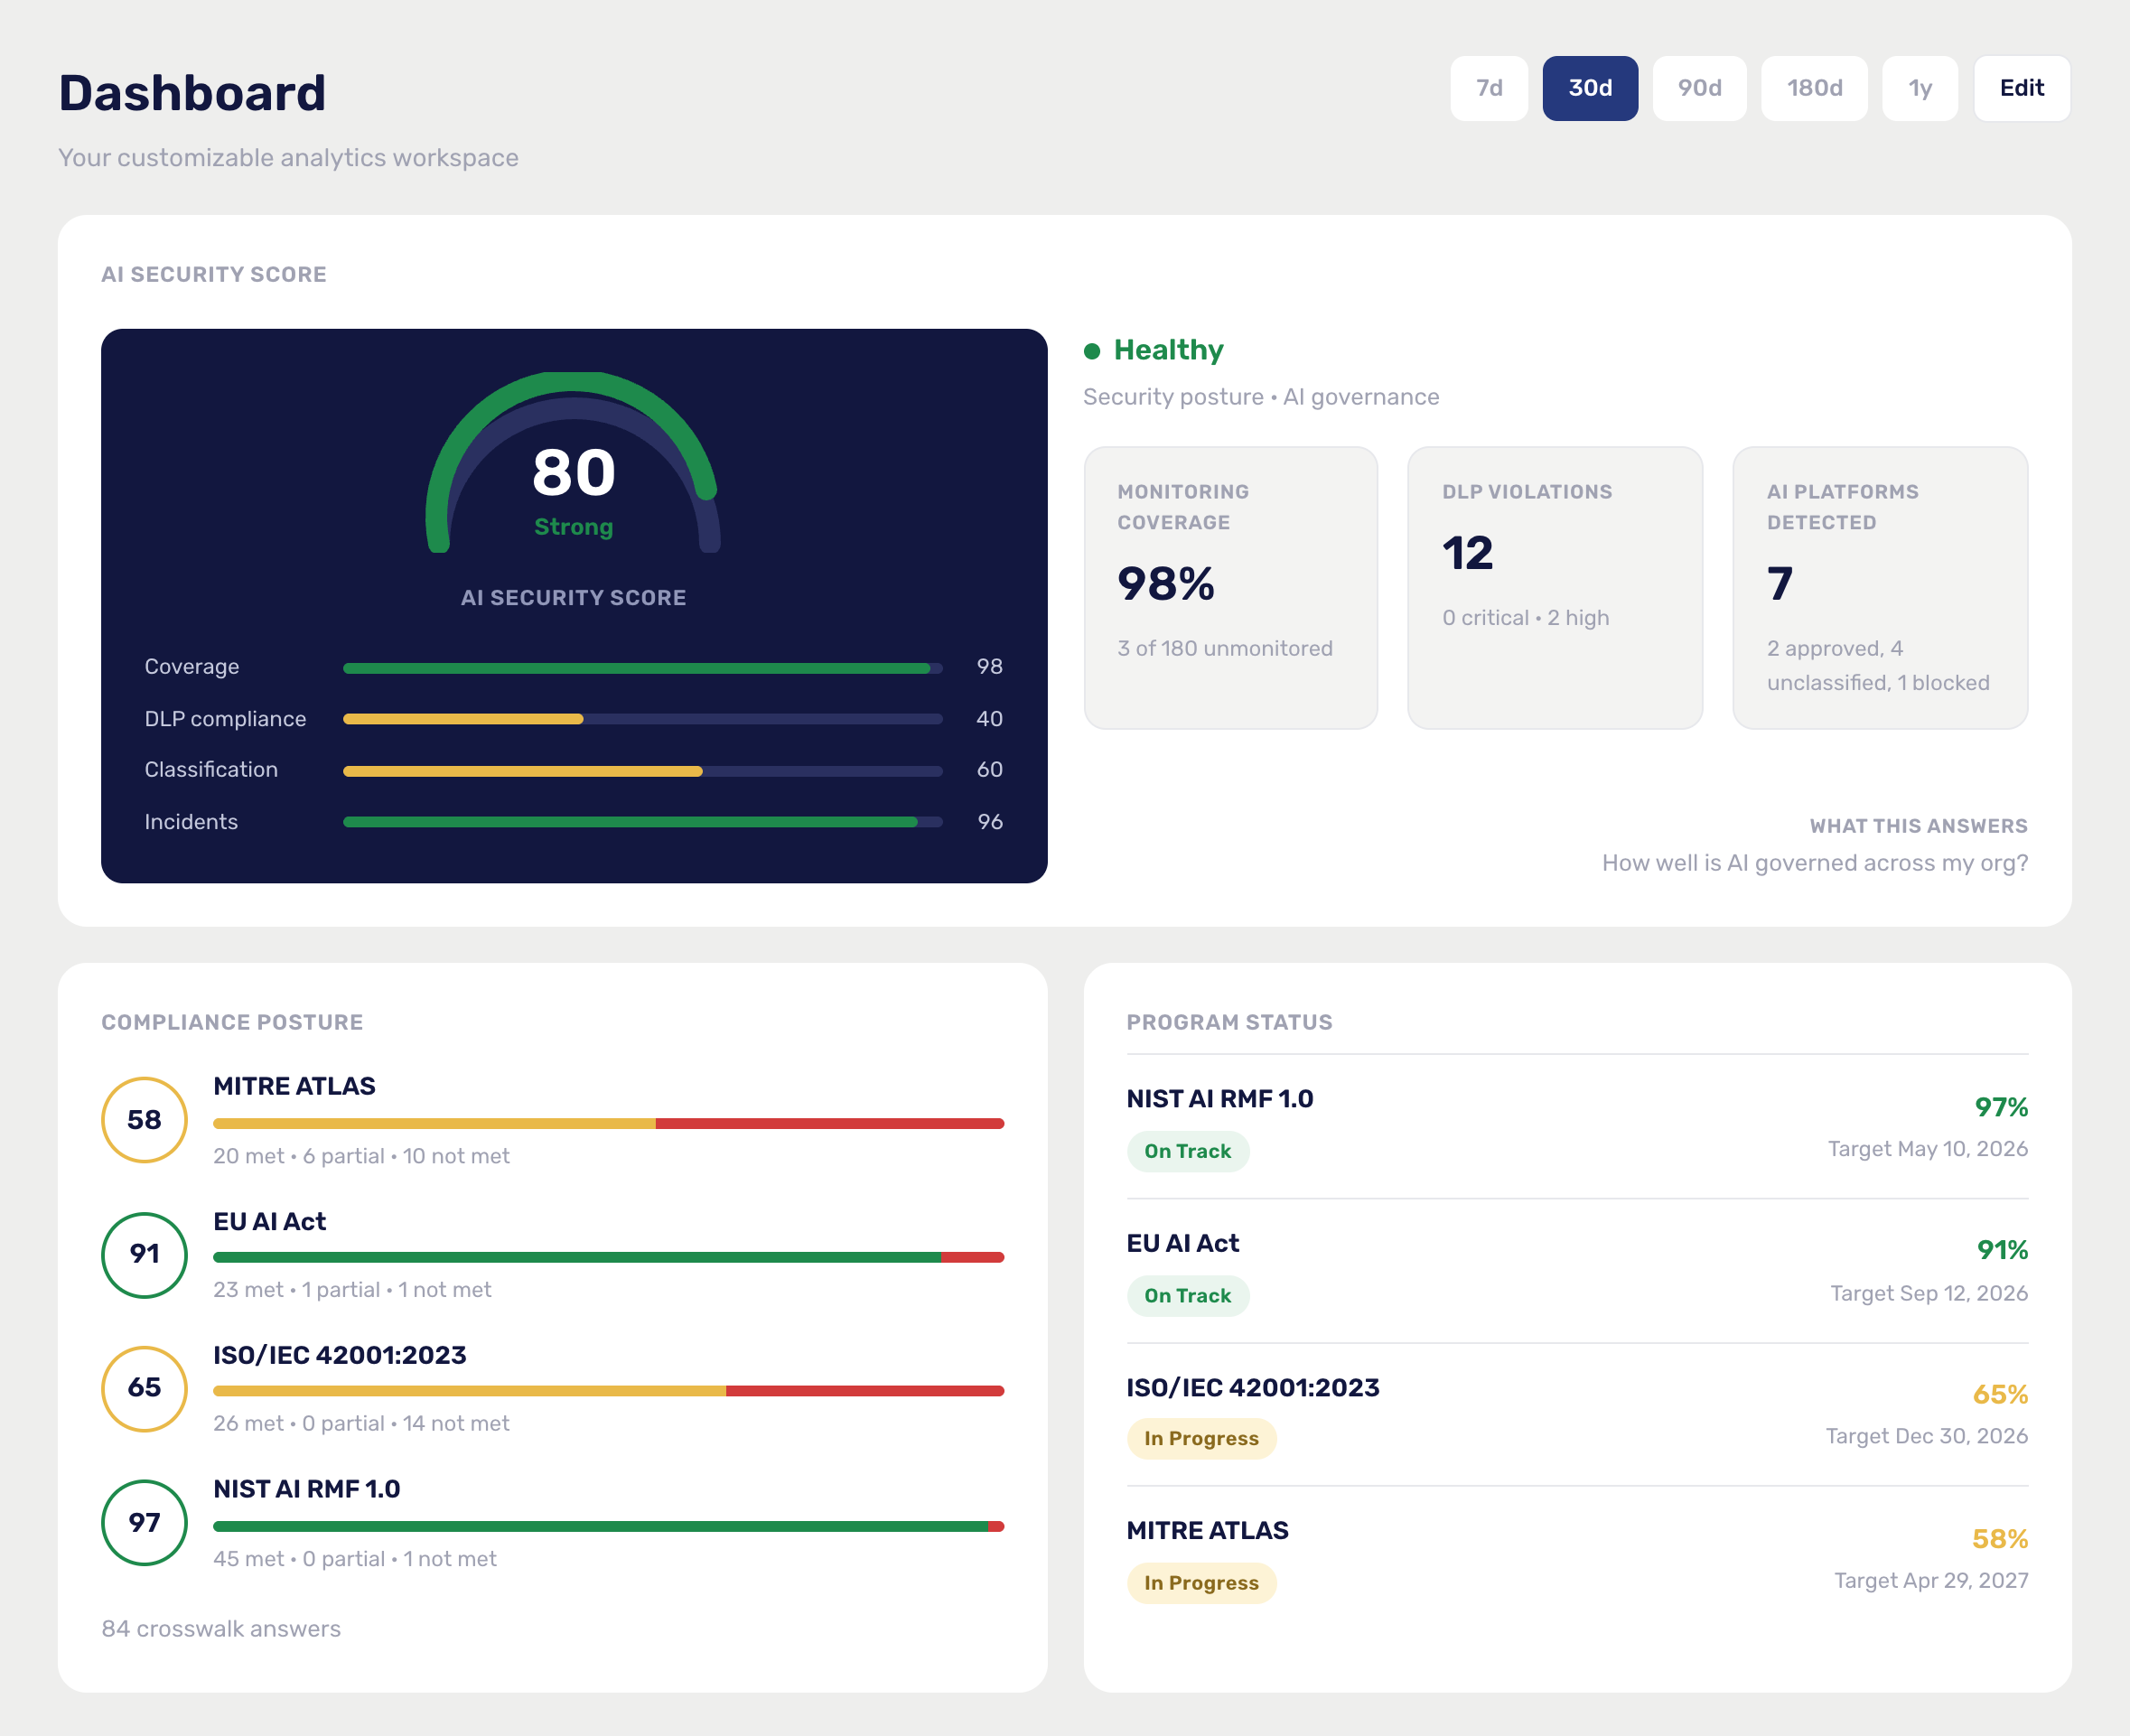
How does our AI governance hold up?

How far has our AI adoption actually come? A maturity ladder built from real usage, not a policy binder.

Key Capabilities

binocular

Shadow AI discovery

See every catalogued AI tool in use, sanctioned or not, within minutes of someone opening it.

Validate Compliance Against the Threats That Actually Matter

Data flow investigation

See where your data moves into and out of AI, before it becomes a problem.

Arrange-List-Descending--Streamline-Ultimate

AI maturity ladder

See where every active user sits, from Explorer to Frontier.

Checklist--Streamline-Ultimate

Approved platform list 

Mark which AI tools are sanctioned, and any use of one that isn't raises a signal automatically.

Shrink--Streamline-Ultimate

Actor classification

Know instantly whether a session is a person or an autonomous agent.

analytics-mountain

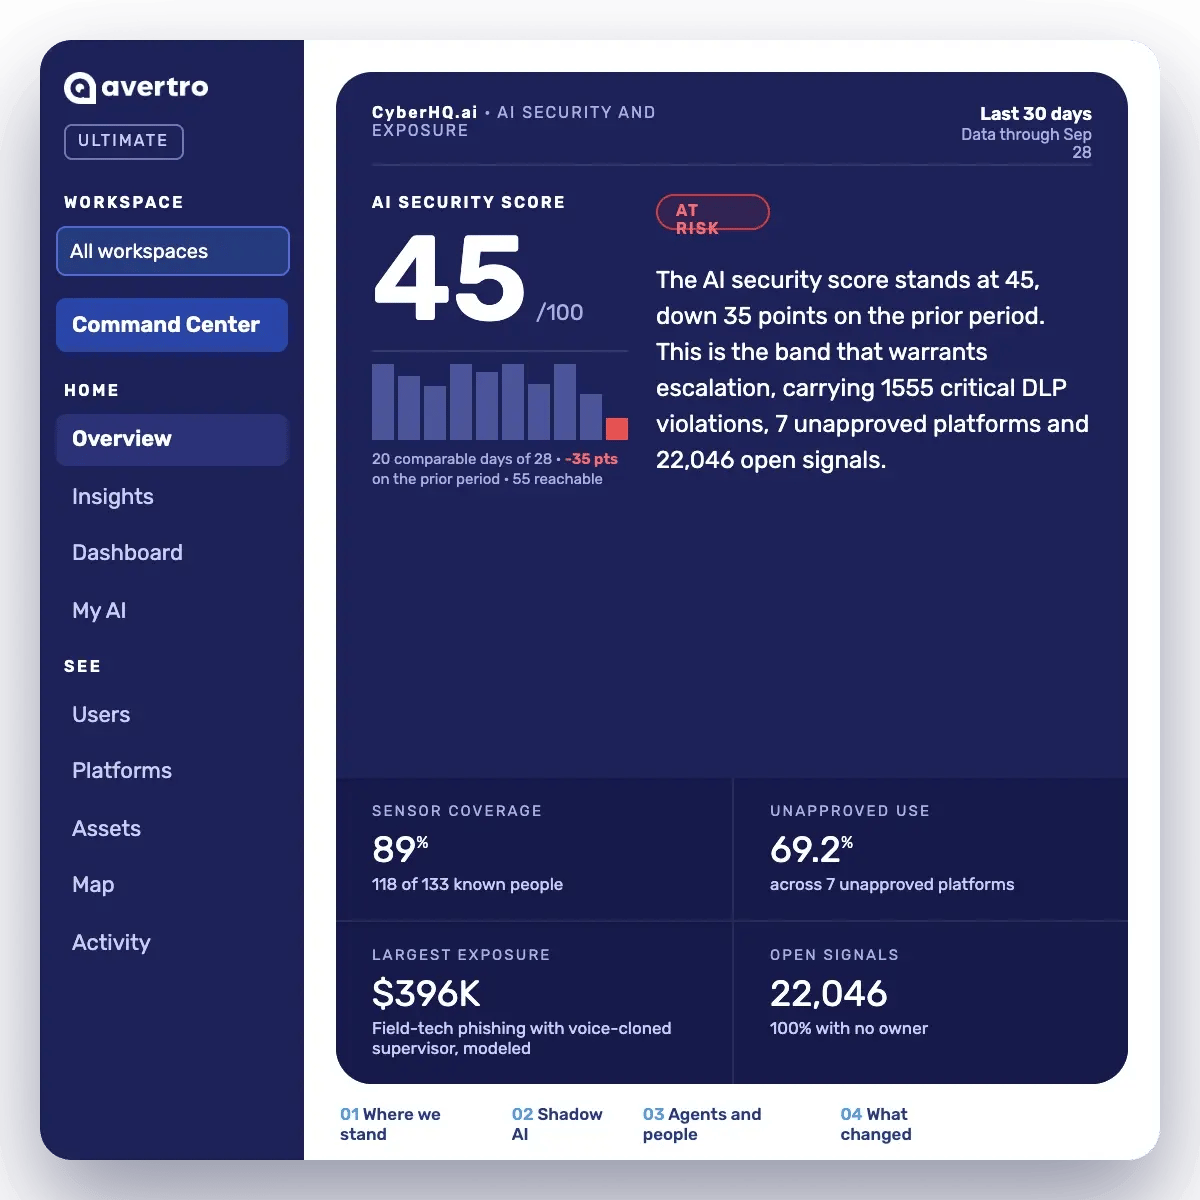
Command center

Every AI signal in one place, not spread across multiple dashboards.

AI-Specific Security Tool

Works Alongside Your Existing Stack

CyberHQ.ai does not compete with the tools you already run. It sees what they were never built to see.

CyberHQ.ai is not a replacement for your CASB, DLP, or SIEM tools. It sits alongside them and provides the AI-specific context those tools were never built to deliver.

Frequently Asked Questions

What is the difference between See, Act, and Prove?

See tier gives you continuous shadow AI discovery, the endpoint sensor with device-level blocking, coverage gap detection, actor classification, and the AI Maturity Ladder. Act adds the AI Security Score, alert triage, custom DLP rules, incident response workflow, per-person block rules, and per-framework compliance attestation. Prove adds multi-framework compliance programs with audit engagements, browser-level blocking, attack simulation with a modeled dollar loss estimate, and AI-agent governance. Each tier includes everything below it.

Does See block anything, or only alert?

See is read-only by design. It tells you what is happening so you can decide what to do about it. Functional blocking, including paste prevention with clipboard clearing, is part of Act.

How CyberHQ.ai different from a CASB or SIEM? 

Your CASB and SIEM were built for documents and email traffic, not AI model context. They cannot tell you whether a session is a person chatting or an autonomous agent acting on your systems. See is purpose-built for that distinction and sits alongside what you already run.

Who is the See tier best fit for? 

CyberHQ.ai's See tier fits organizations still in discovery mode, ones that don't yet have a confirmed picture of which AI tools are in use, what data is moving through them, or where to look first. It's built for teams that need visibility before they can decide what to act on, without committing to a formal compliance program yet. If you already have a DLP or shadow AI finding that needs a workflow, Act is the better starting point.

How long does deployment actually take?

Under 30 minutes for most organizations. The browser extension deploys through your existing browser-management policy (Google Admin, Intune, Group Policy, Jamf, or Kandji), and the endpoint sensor installs through MDM, a one-command install, or a self-enrollment page your admin can turn on, with no proxy or SSL inspection required. Most teams see their first meaningful findings within 24 to 48 hours.

What is an AI Governance Command Platform?

An AI Governance Command Platform gives a business a continuous, evidence-backed picture of how AI is actually being used across the organization, from first shadow AI discovery through cost governance, agent oversight, and audit-ready compliance. CyberHQ.AI is built to sit alongside your existing security stack, not replace it, and to answer three questions on an ongoing basis: how is AI being used right now, what does that usage expose you to, and can you prove you have control.

CyberHQ.ai

Say Yes to AI with Evidence

Trial CyberHQ.ai for 30-days and get a personalized AI usage report you can act on.

No commitment, proxy or SSL inspection required.