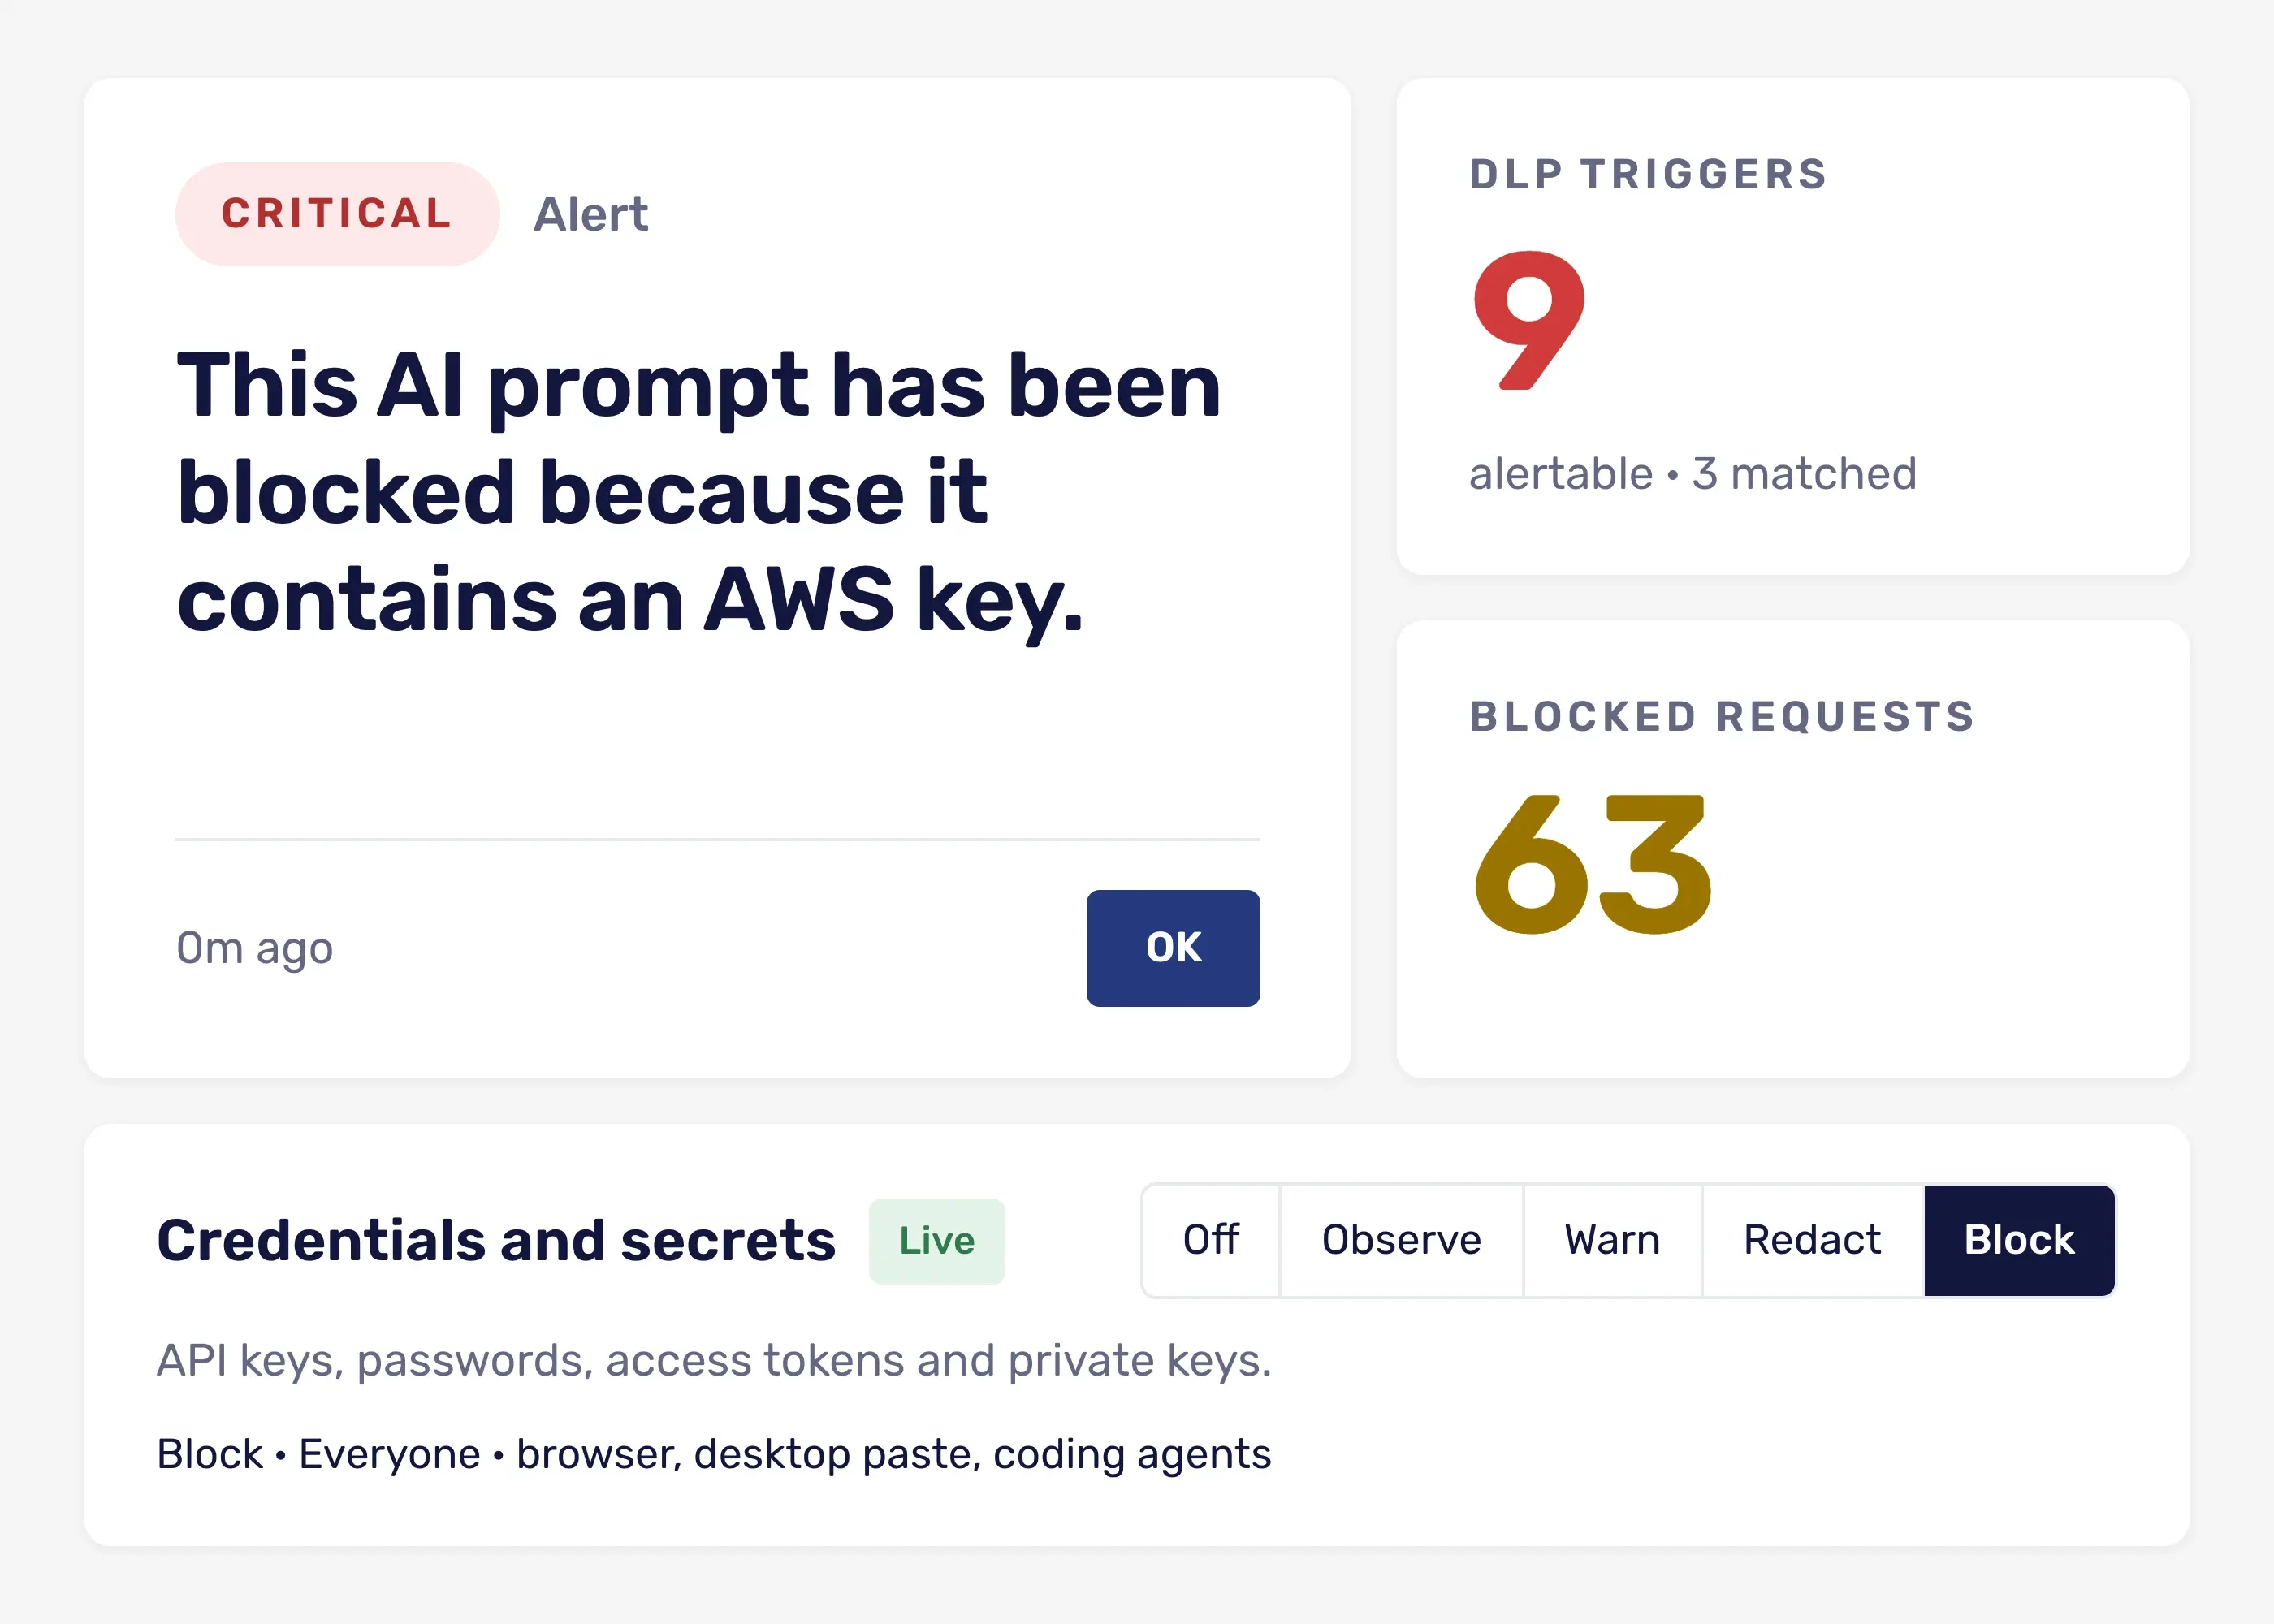
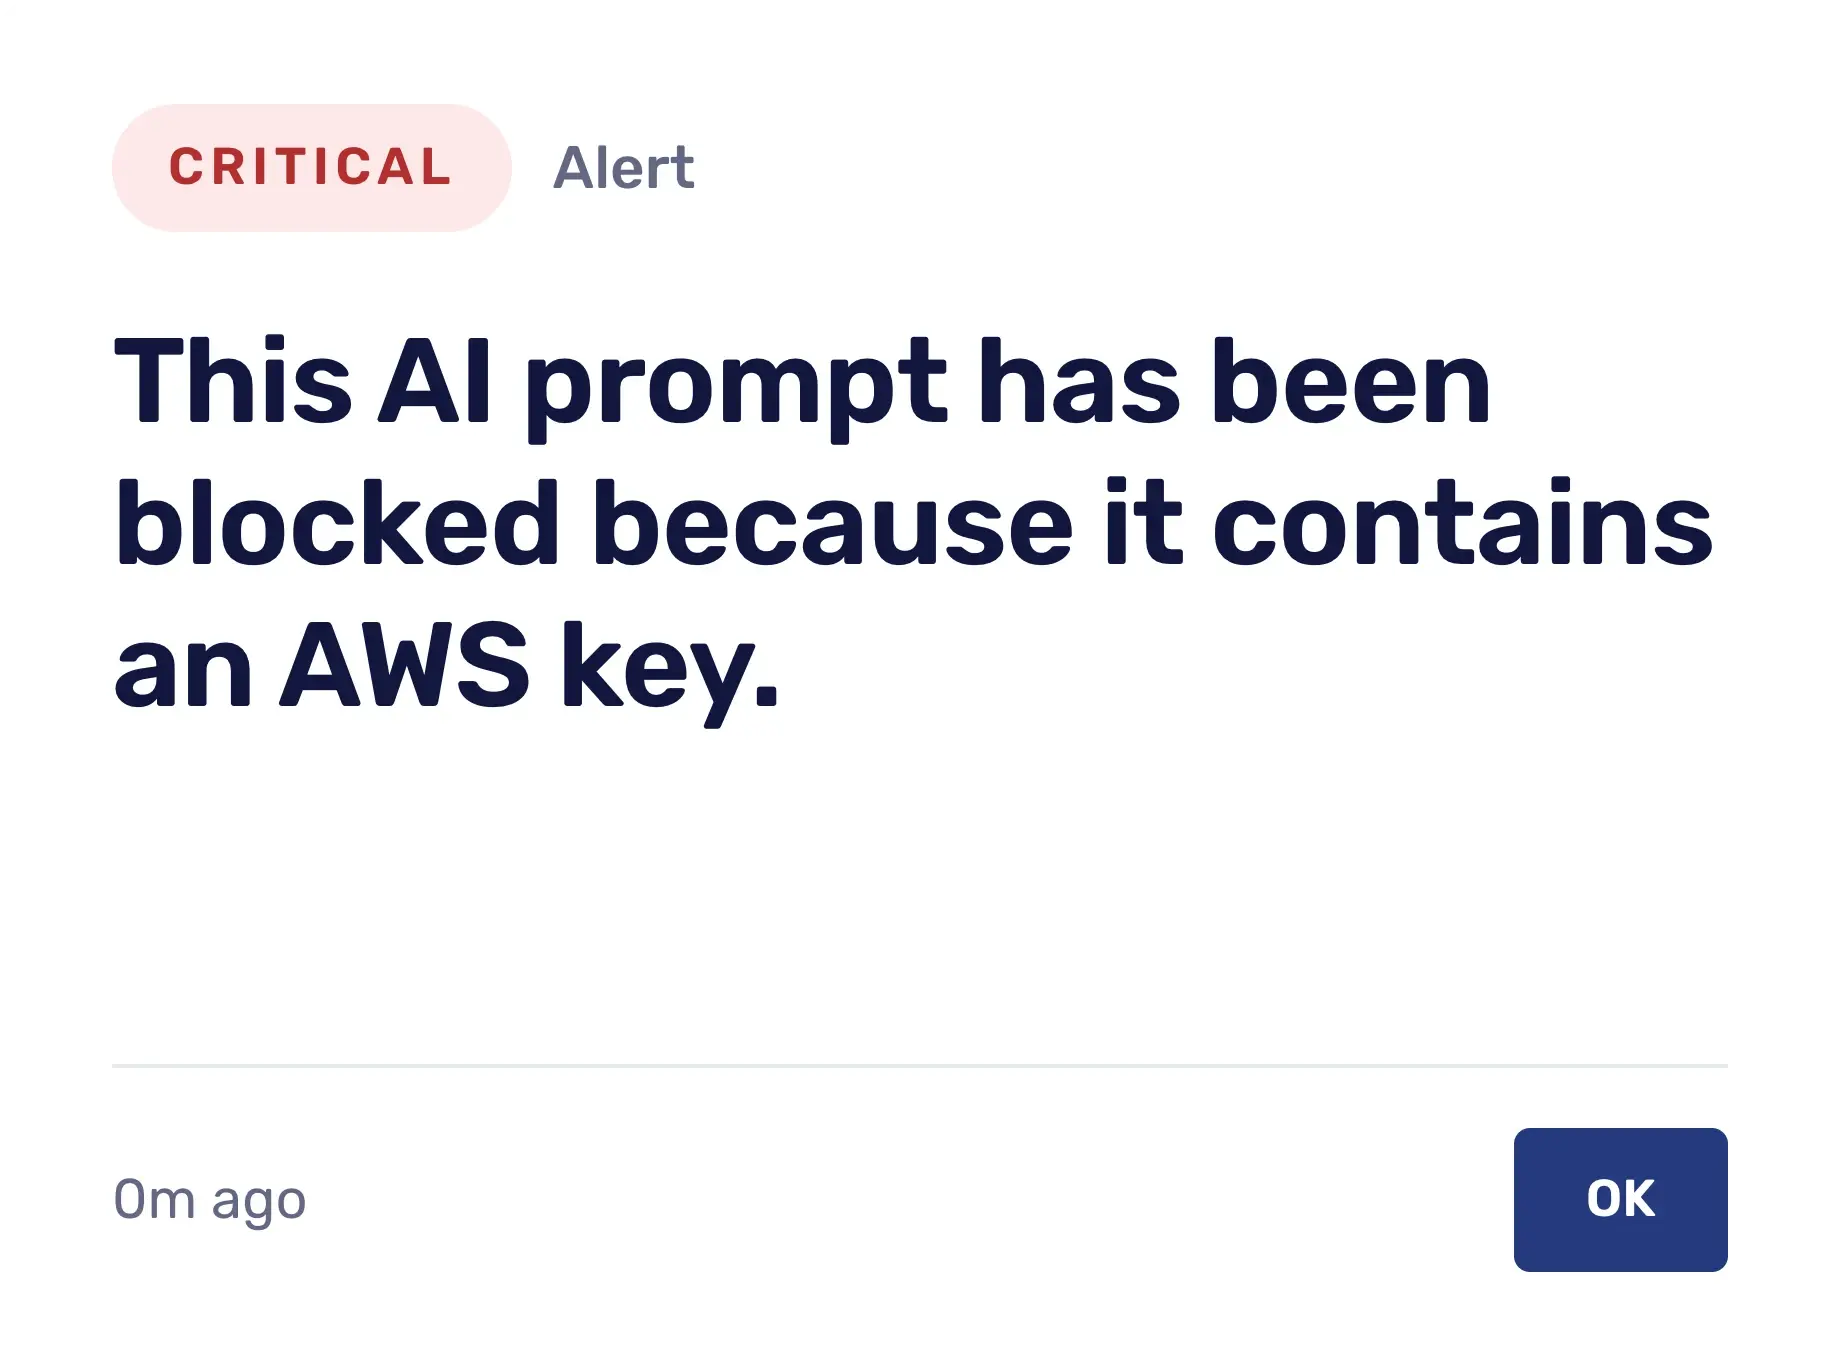
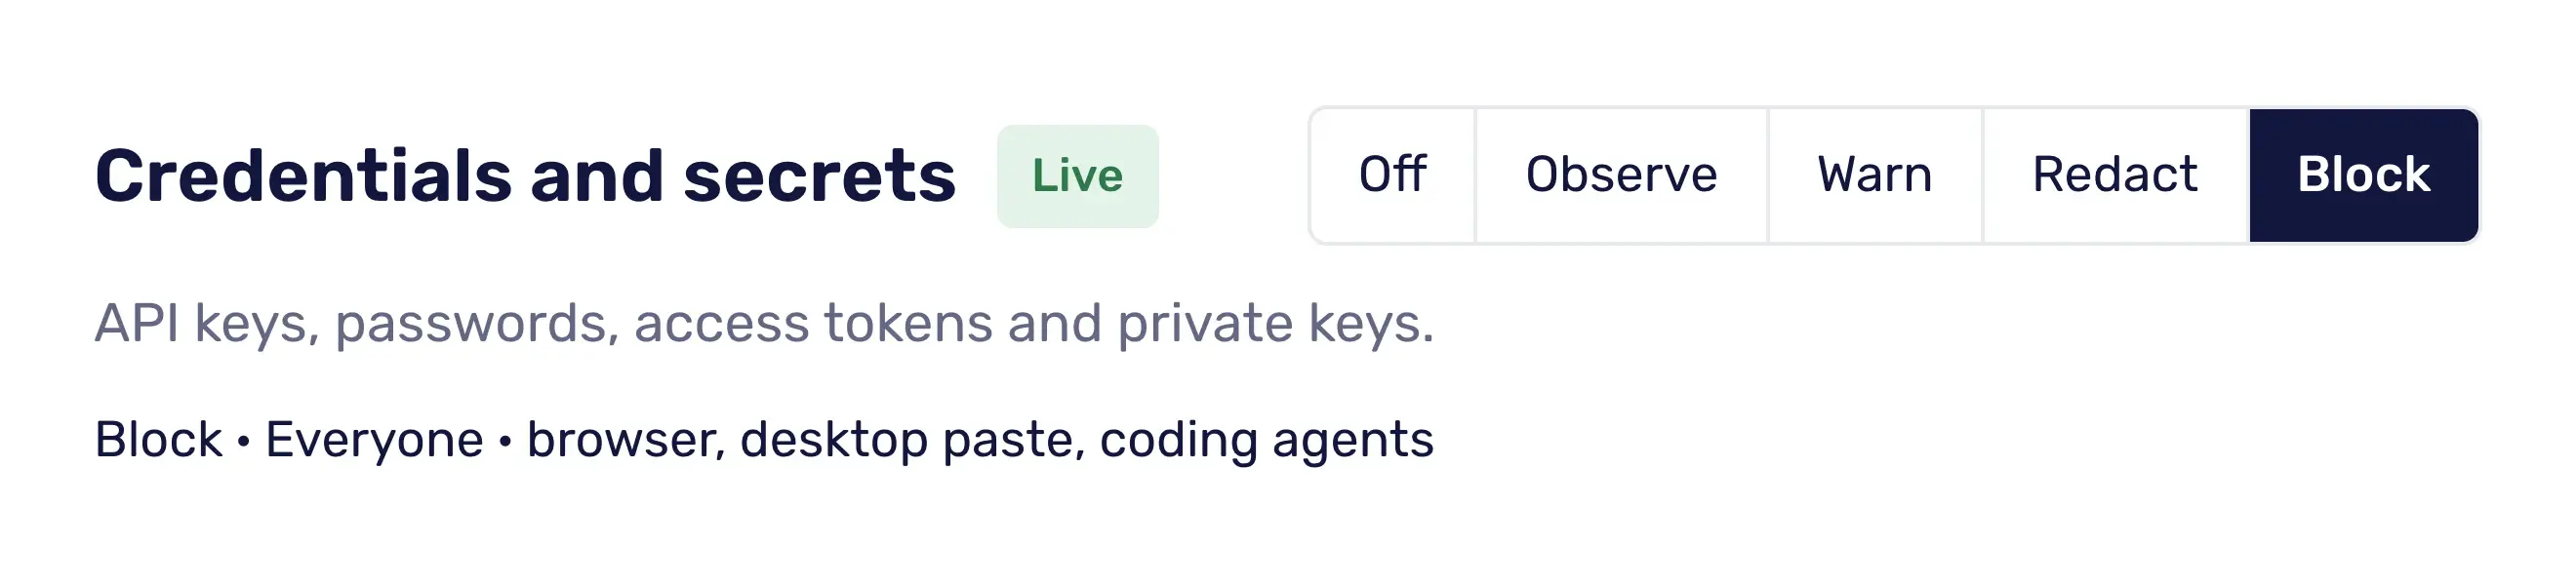
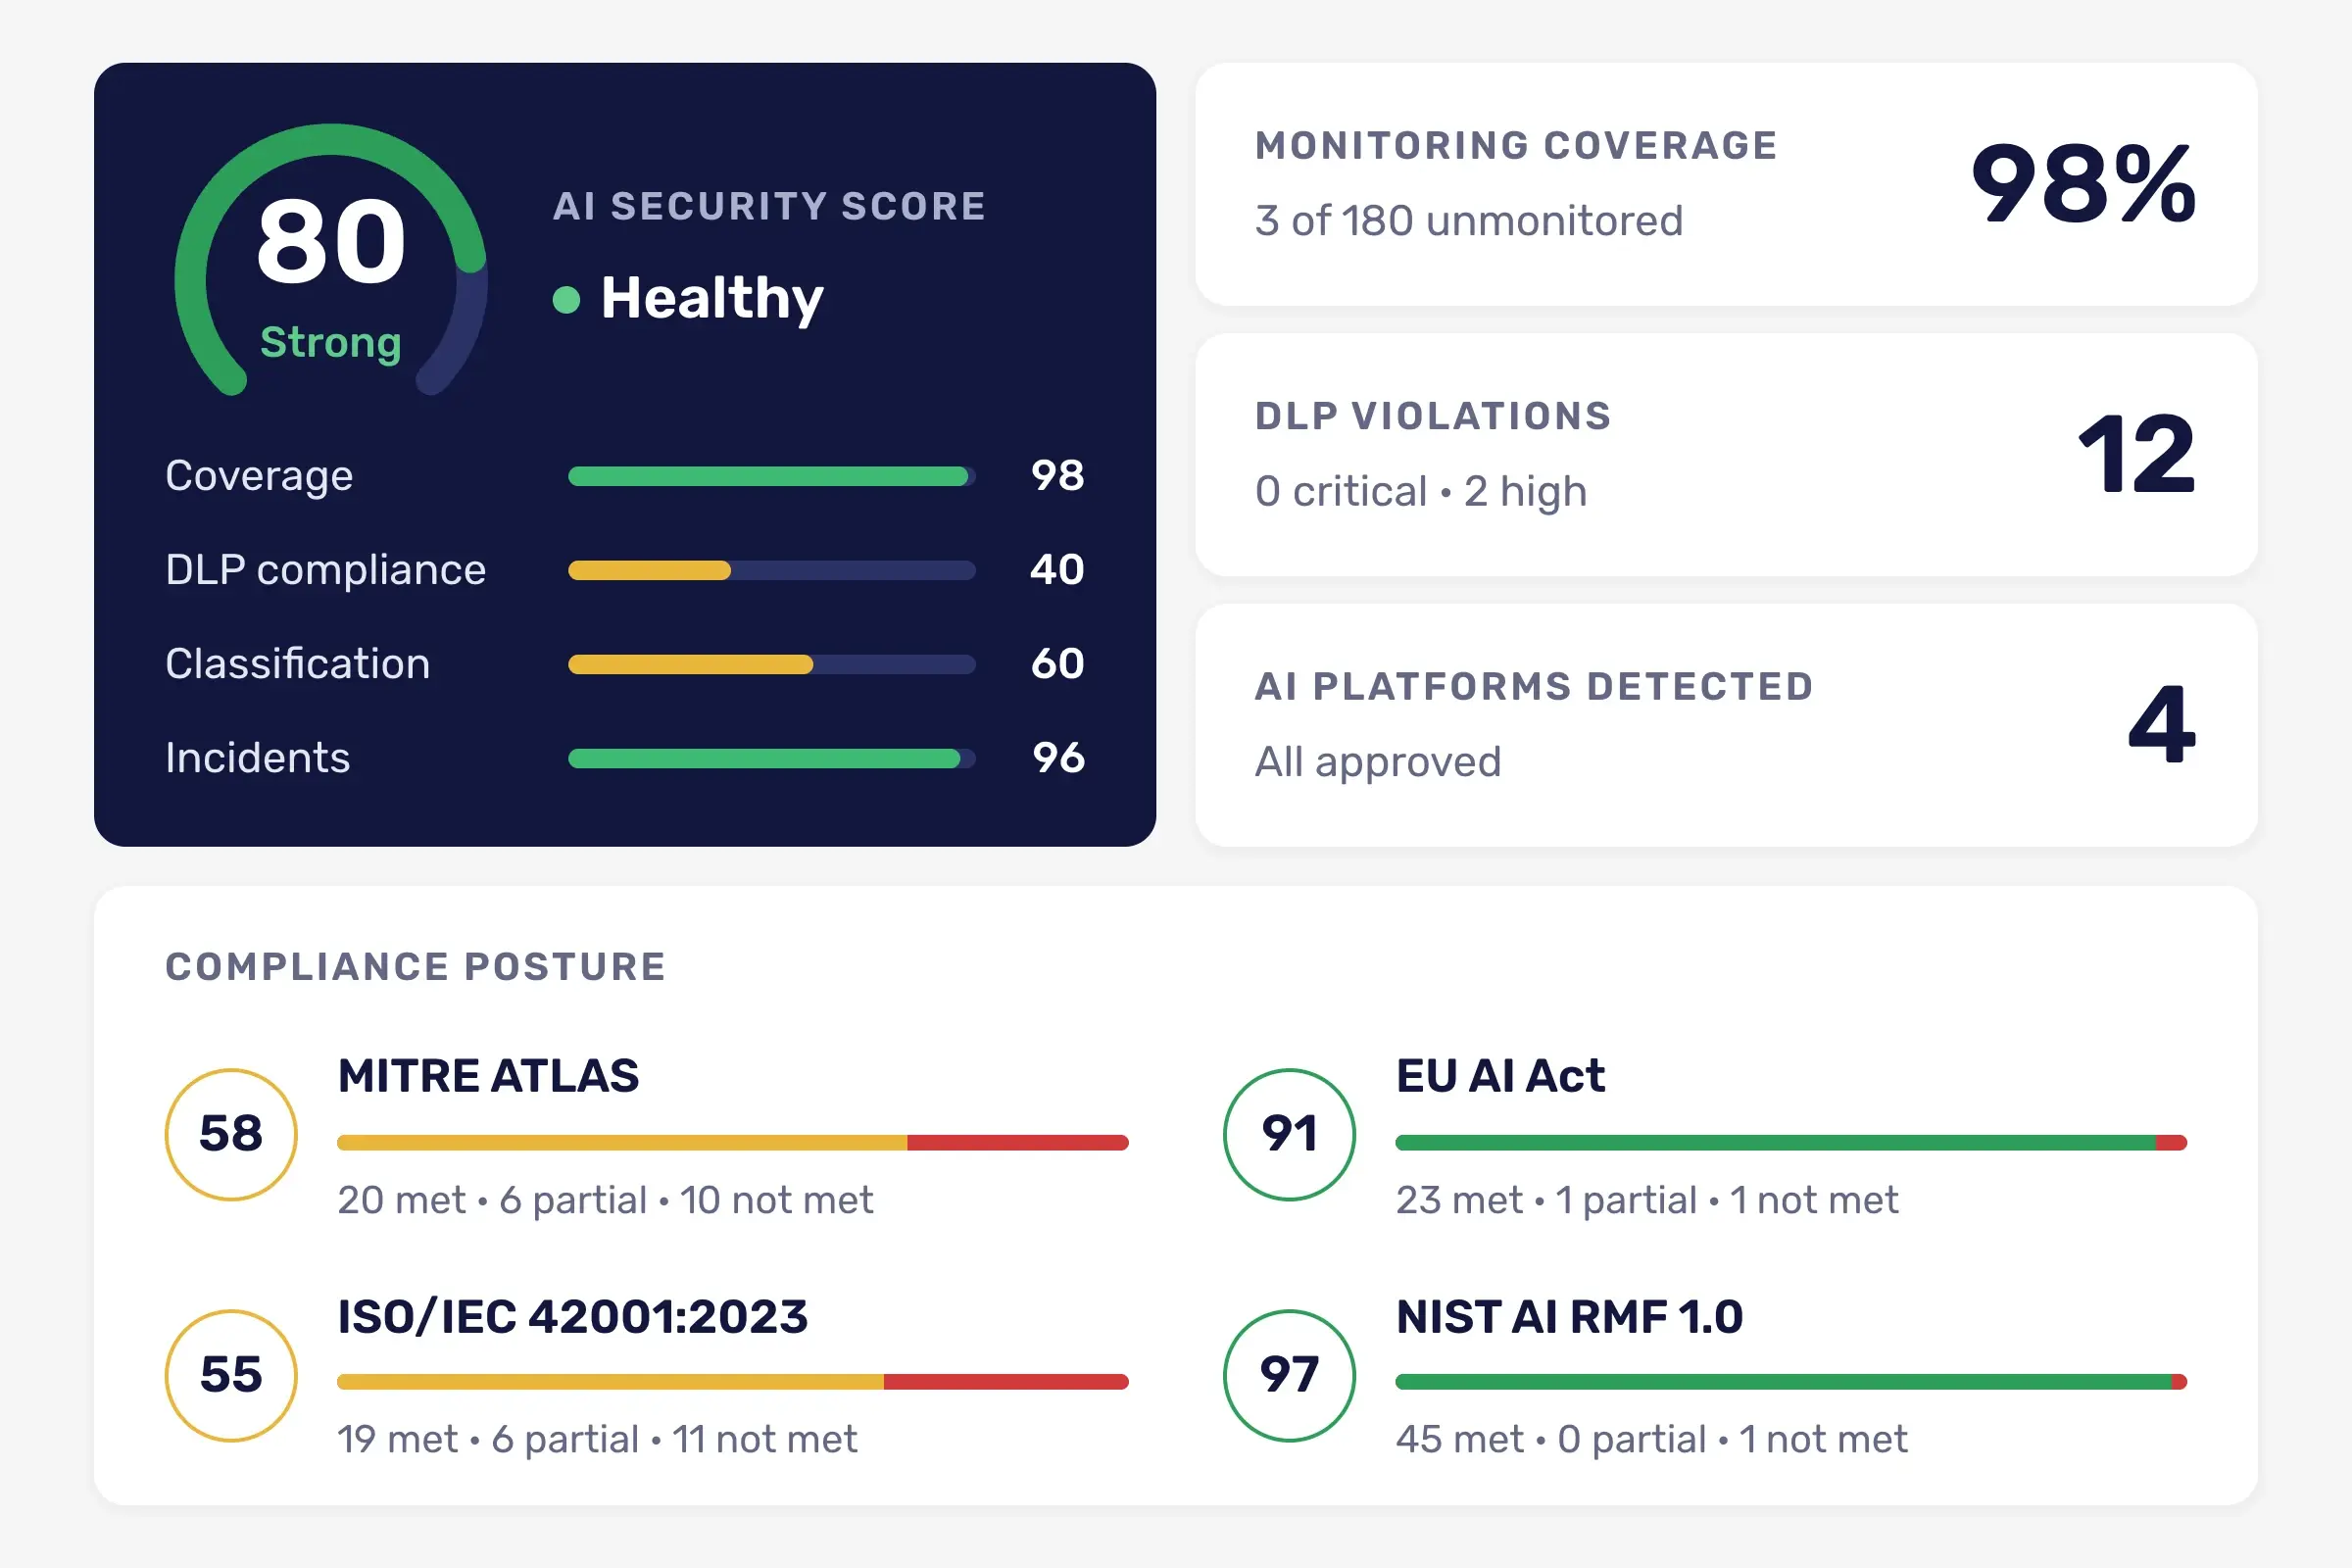
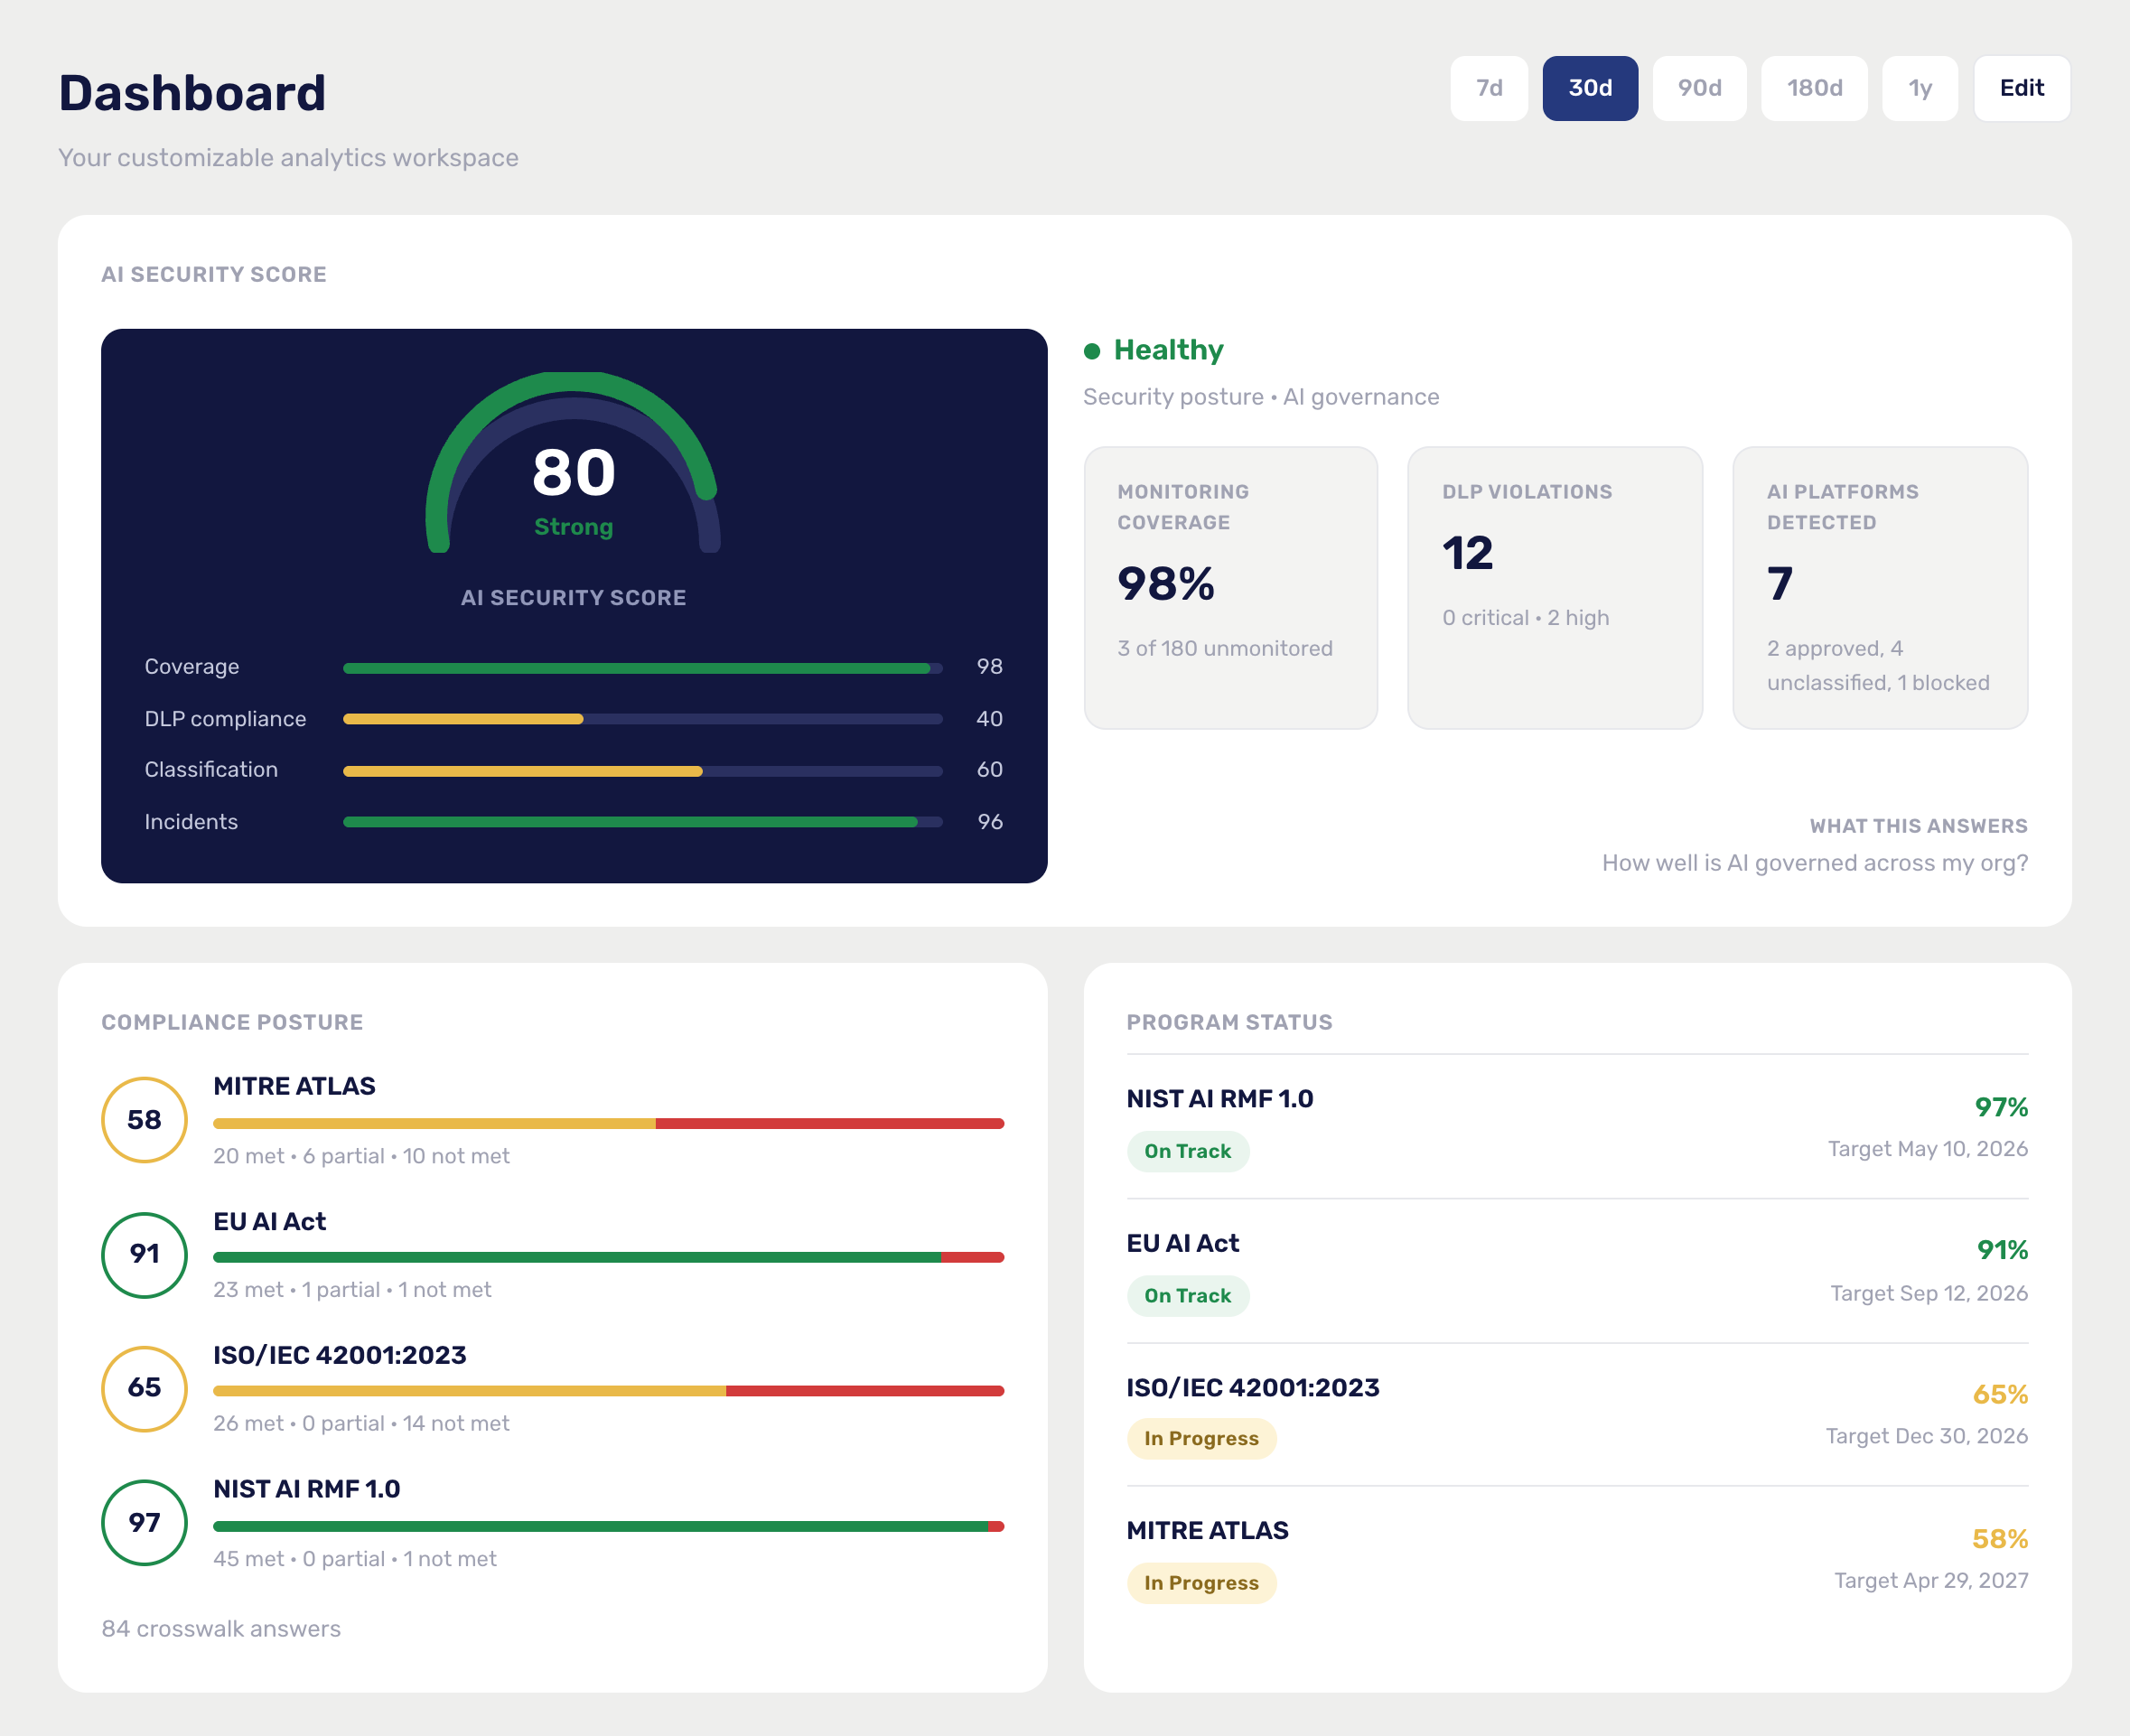
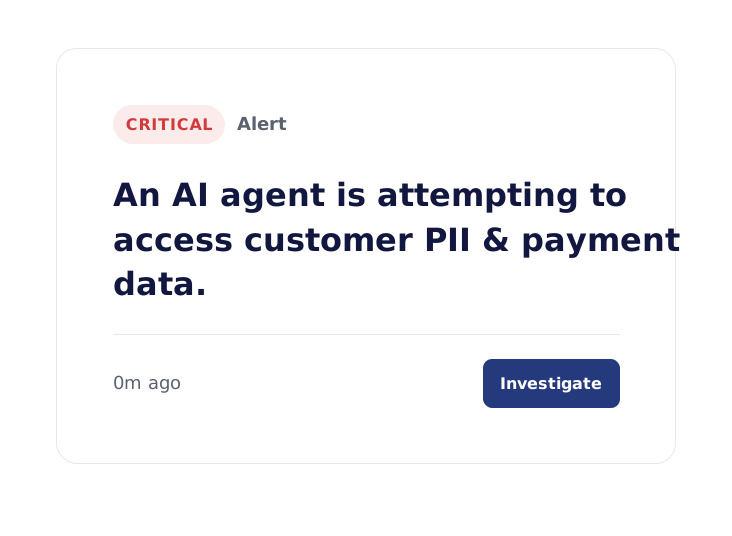
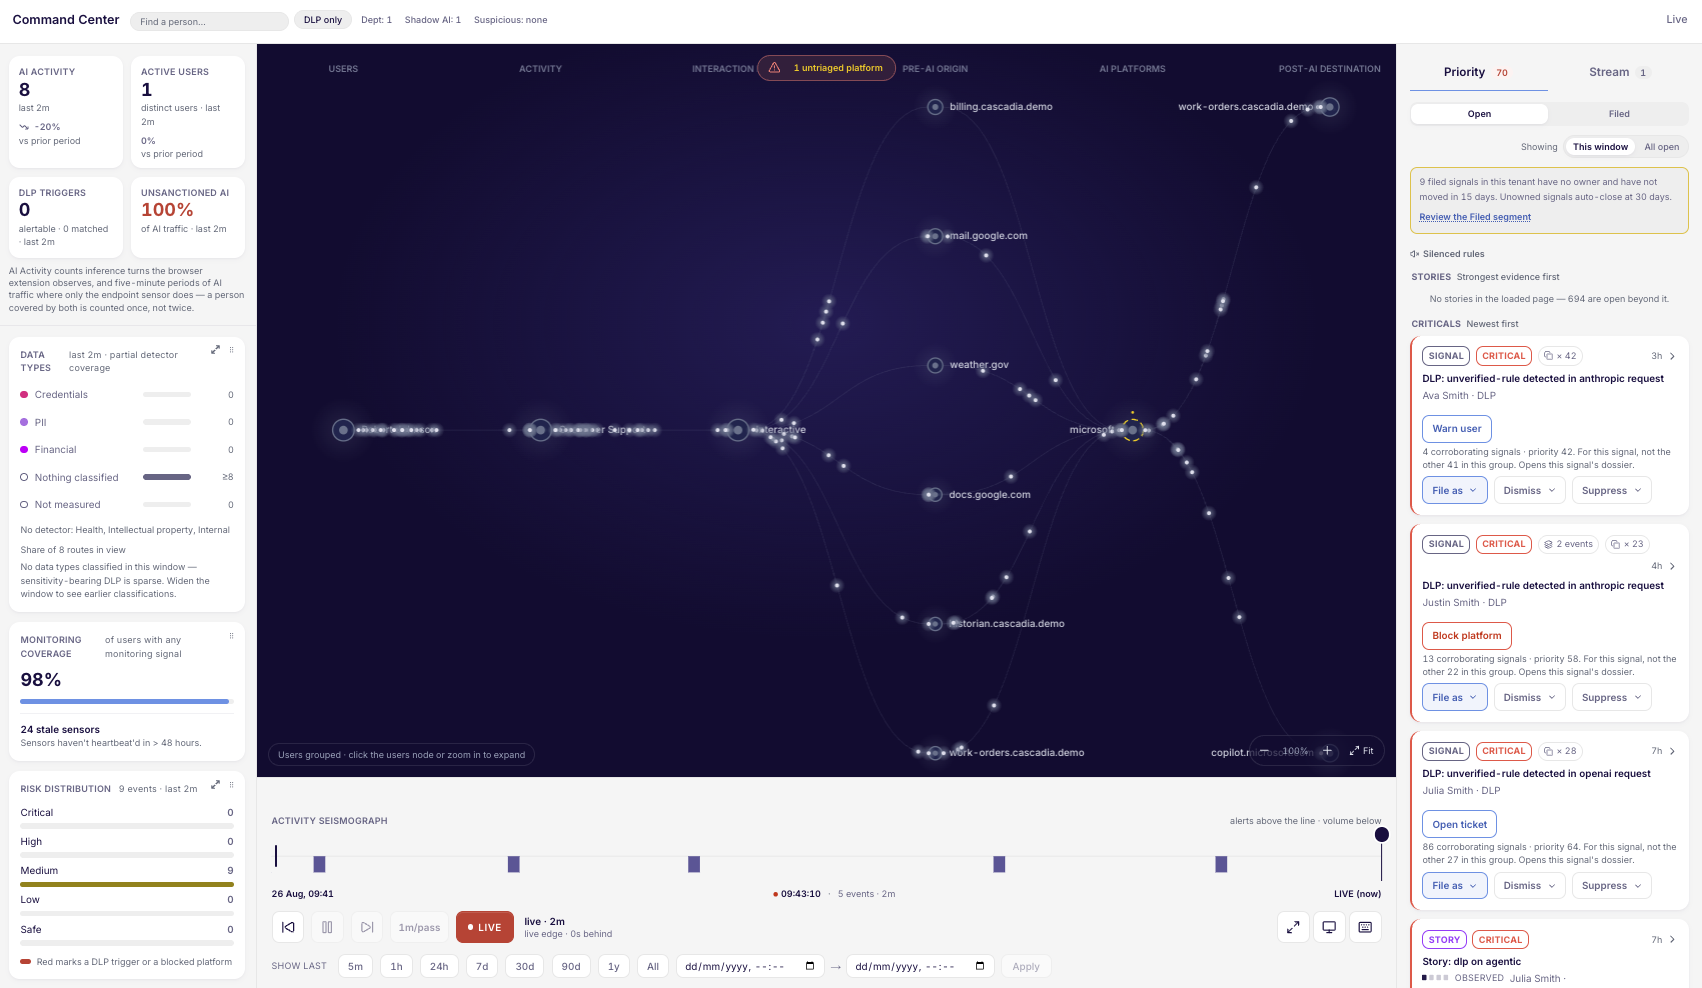
DLP on AI traffic scans every prompt as it is sent, and every paste on sensor-equipped endpoints, for credentials, payment card numbers, US Social Security numbers, and your own custom patterns. Set each rule to Observe, Warn, Redact, or Block, and, once paste protection is on, stop a sensitive paste with clipboard clearing on macOS and Windows.
Catch sensitive data before it leaves
Real-time prompt and paste scanning
Clipboard clearing on block
3
DLP enforcement modes per rule: monitor, warn, or block
<48 hrs
to a first meaningful DLP finding after extension deployment
40 +
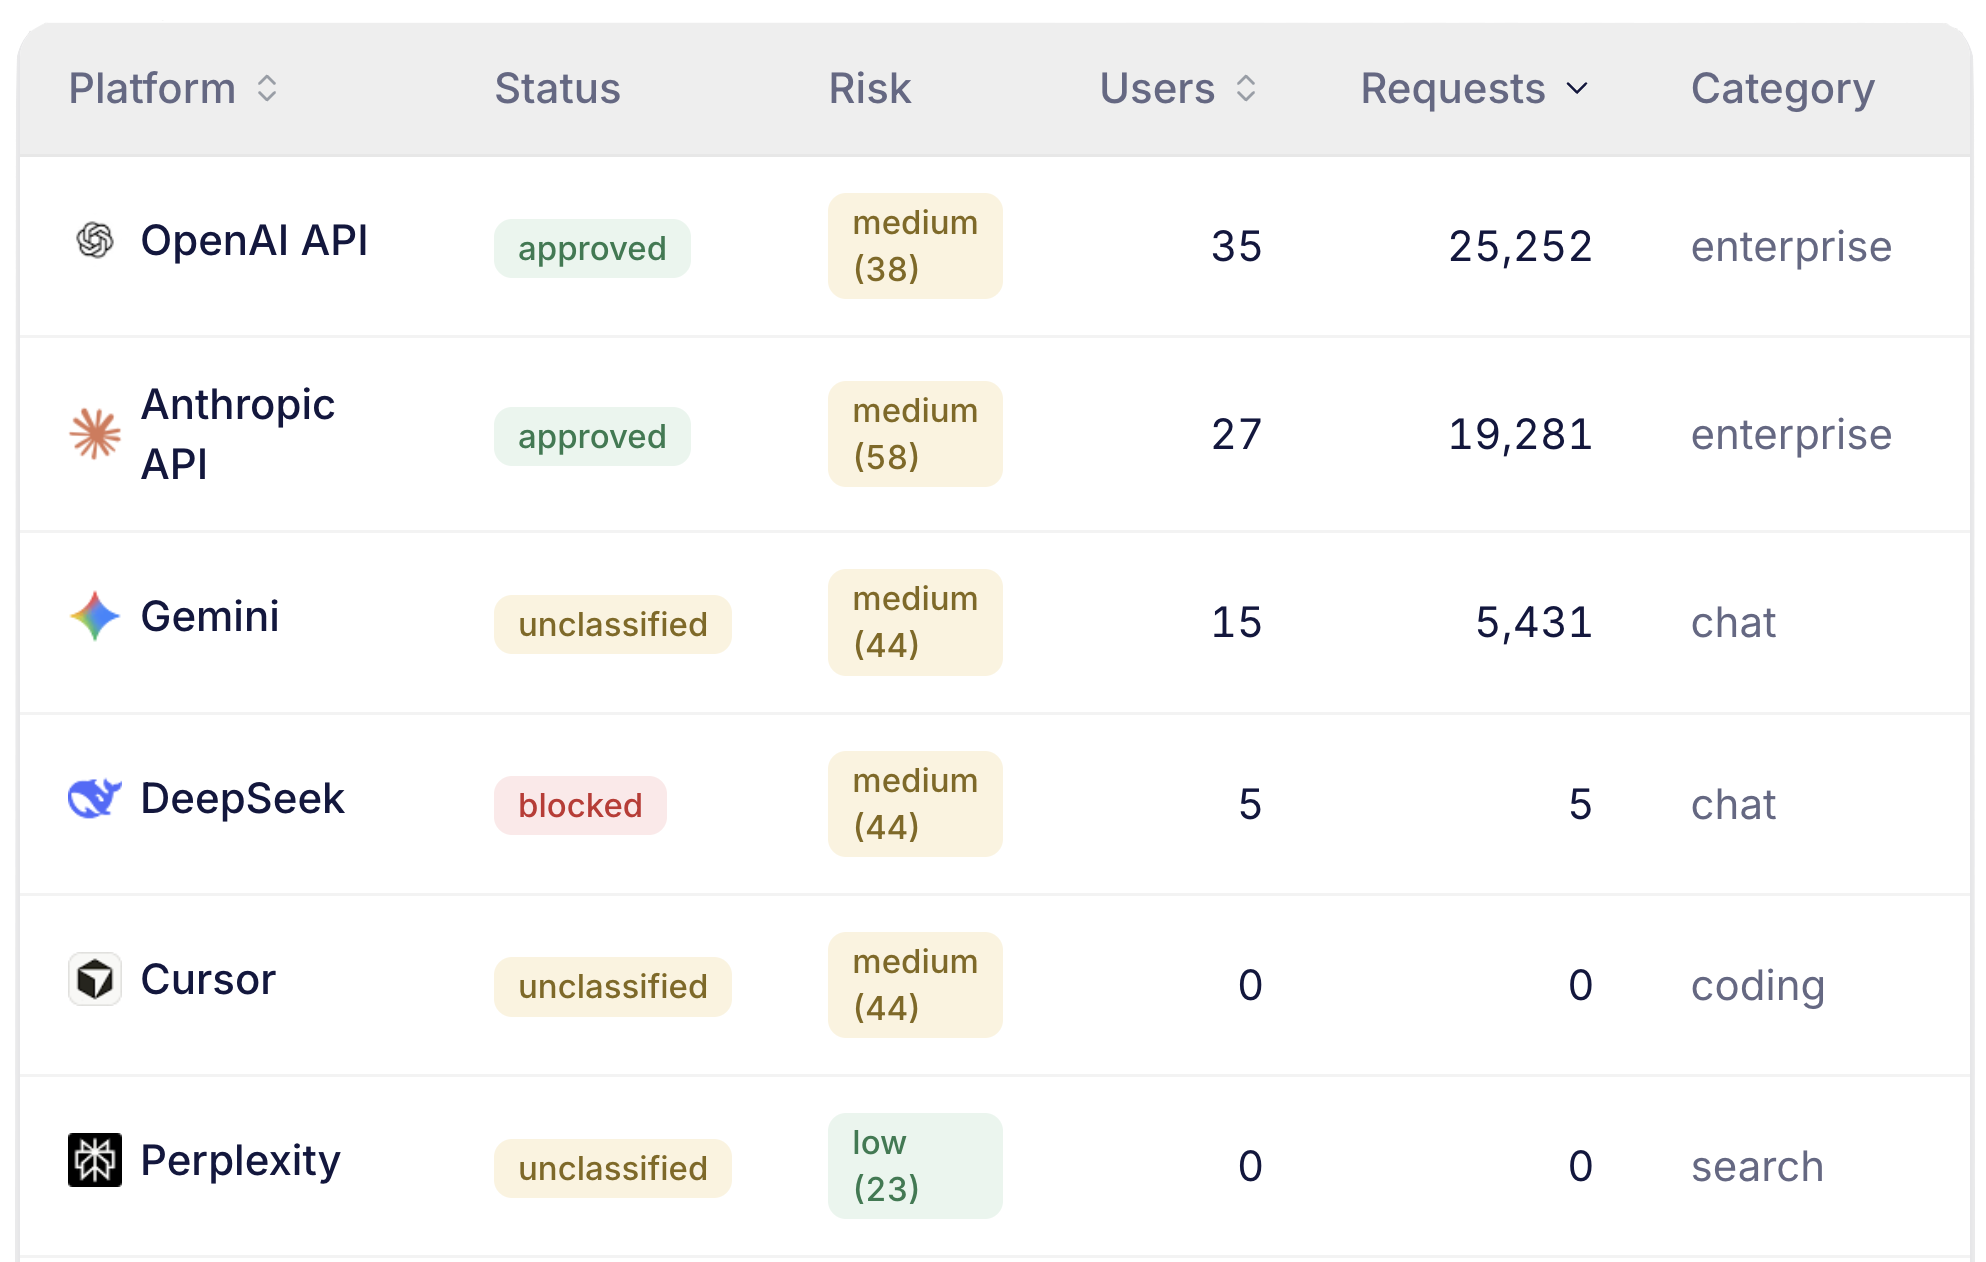
AI providers monitored on a continuously expanding watchlist
< 30 mins
to full deployment, no proxy or SSL inspection required
The Problem
Authorized Access, Unauthorized Destination
A commercial team pastes a signed contract, a rate card, and a clause library into an AI tool to write a proposal. No rule gets broken. The person already had access to every one of those documents. But the negotiated terms and the margin logic just left the building through a channel that looked authorized.
CASB and DLP tools were built to watch documents and email. They cannot read a prompt, tell what a model is being asked to do with it, or tell a person drafting a memo from an agent forwarding a file. The access is legitimate, so nothing trips.
The same thing happens in HR, when CVs and case files get summarized outside the system of record, and in Engineering, when source code gets pasted in for a quick refactor. The exposure stays silent until Legal, Privacy, or a customer asks where the data went.
AI Security Command
What CyberHQ.ai Does Differently
See it the moment it happens. Real-time pattern matching scans every prompt as it is sent, and every paste on sensor-equipped endpoints, for credentials, payment card numbers, US Social Security numbers, and custom patterns.
Set the response, not just the alert. Every DLP rule runs as Observe, Warn, Redact, or Block, or follows the tenant's default action for its severity when none is set, with precision tracked as a measured state per rule.
Block the paste, not just log it. A flagged paste into an AI tool is stopped before it reaches the model, and cancelling clears the clipboard. On Linux, the same rule still fires, caught after the fact through DLP scanning and, where enabled, file-read detection.
AI Security Command
How to Prevent Data being shared with AI
Three capabilities that turn an authorized paste into a governed one, without slowing the person doing legitimate work.
Real-time pattern matching
Scans every prompt and paste for credentials, payment card numbers, US Social Security numbers or your custom rules.
Four-response DLP rules
Runs each rule as Observe, Warn, Redact, or Block, or follows the tenant's default action for its severity, with precision tracked as a measured state, not a rolling score.
Functional paste enforcement
Cancels the paste and clears the system clipboard before data leaves the browser.
AI Usage Insights
AI Usage Insights Within 48hrs Of Deployment
Start a free 30-day trial and see results on your insights dashboard within 48 hours of deploying your sensor.
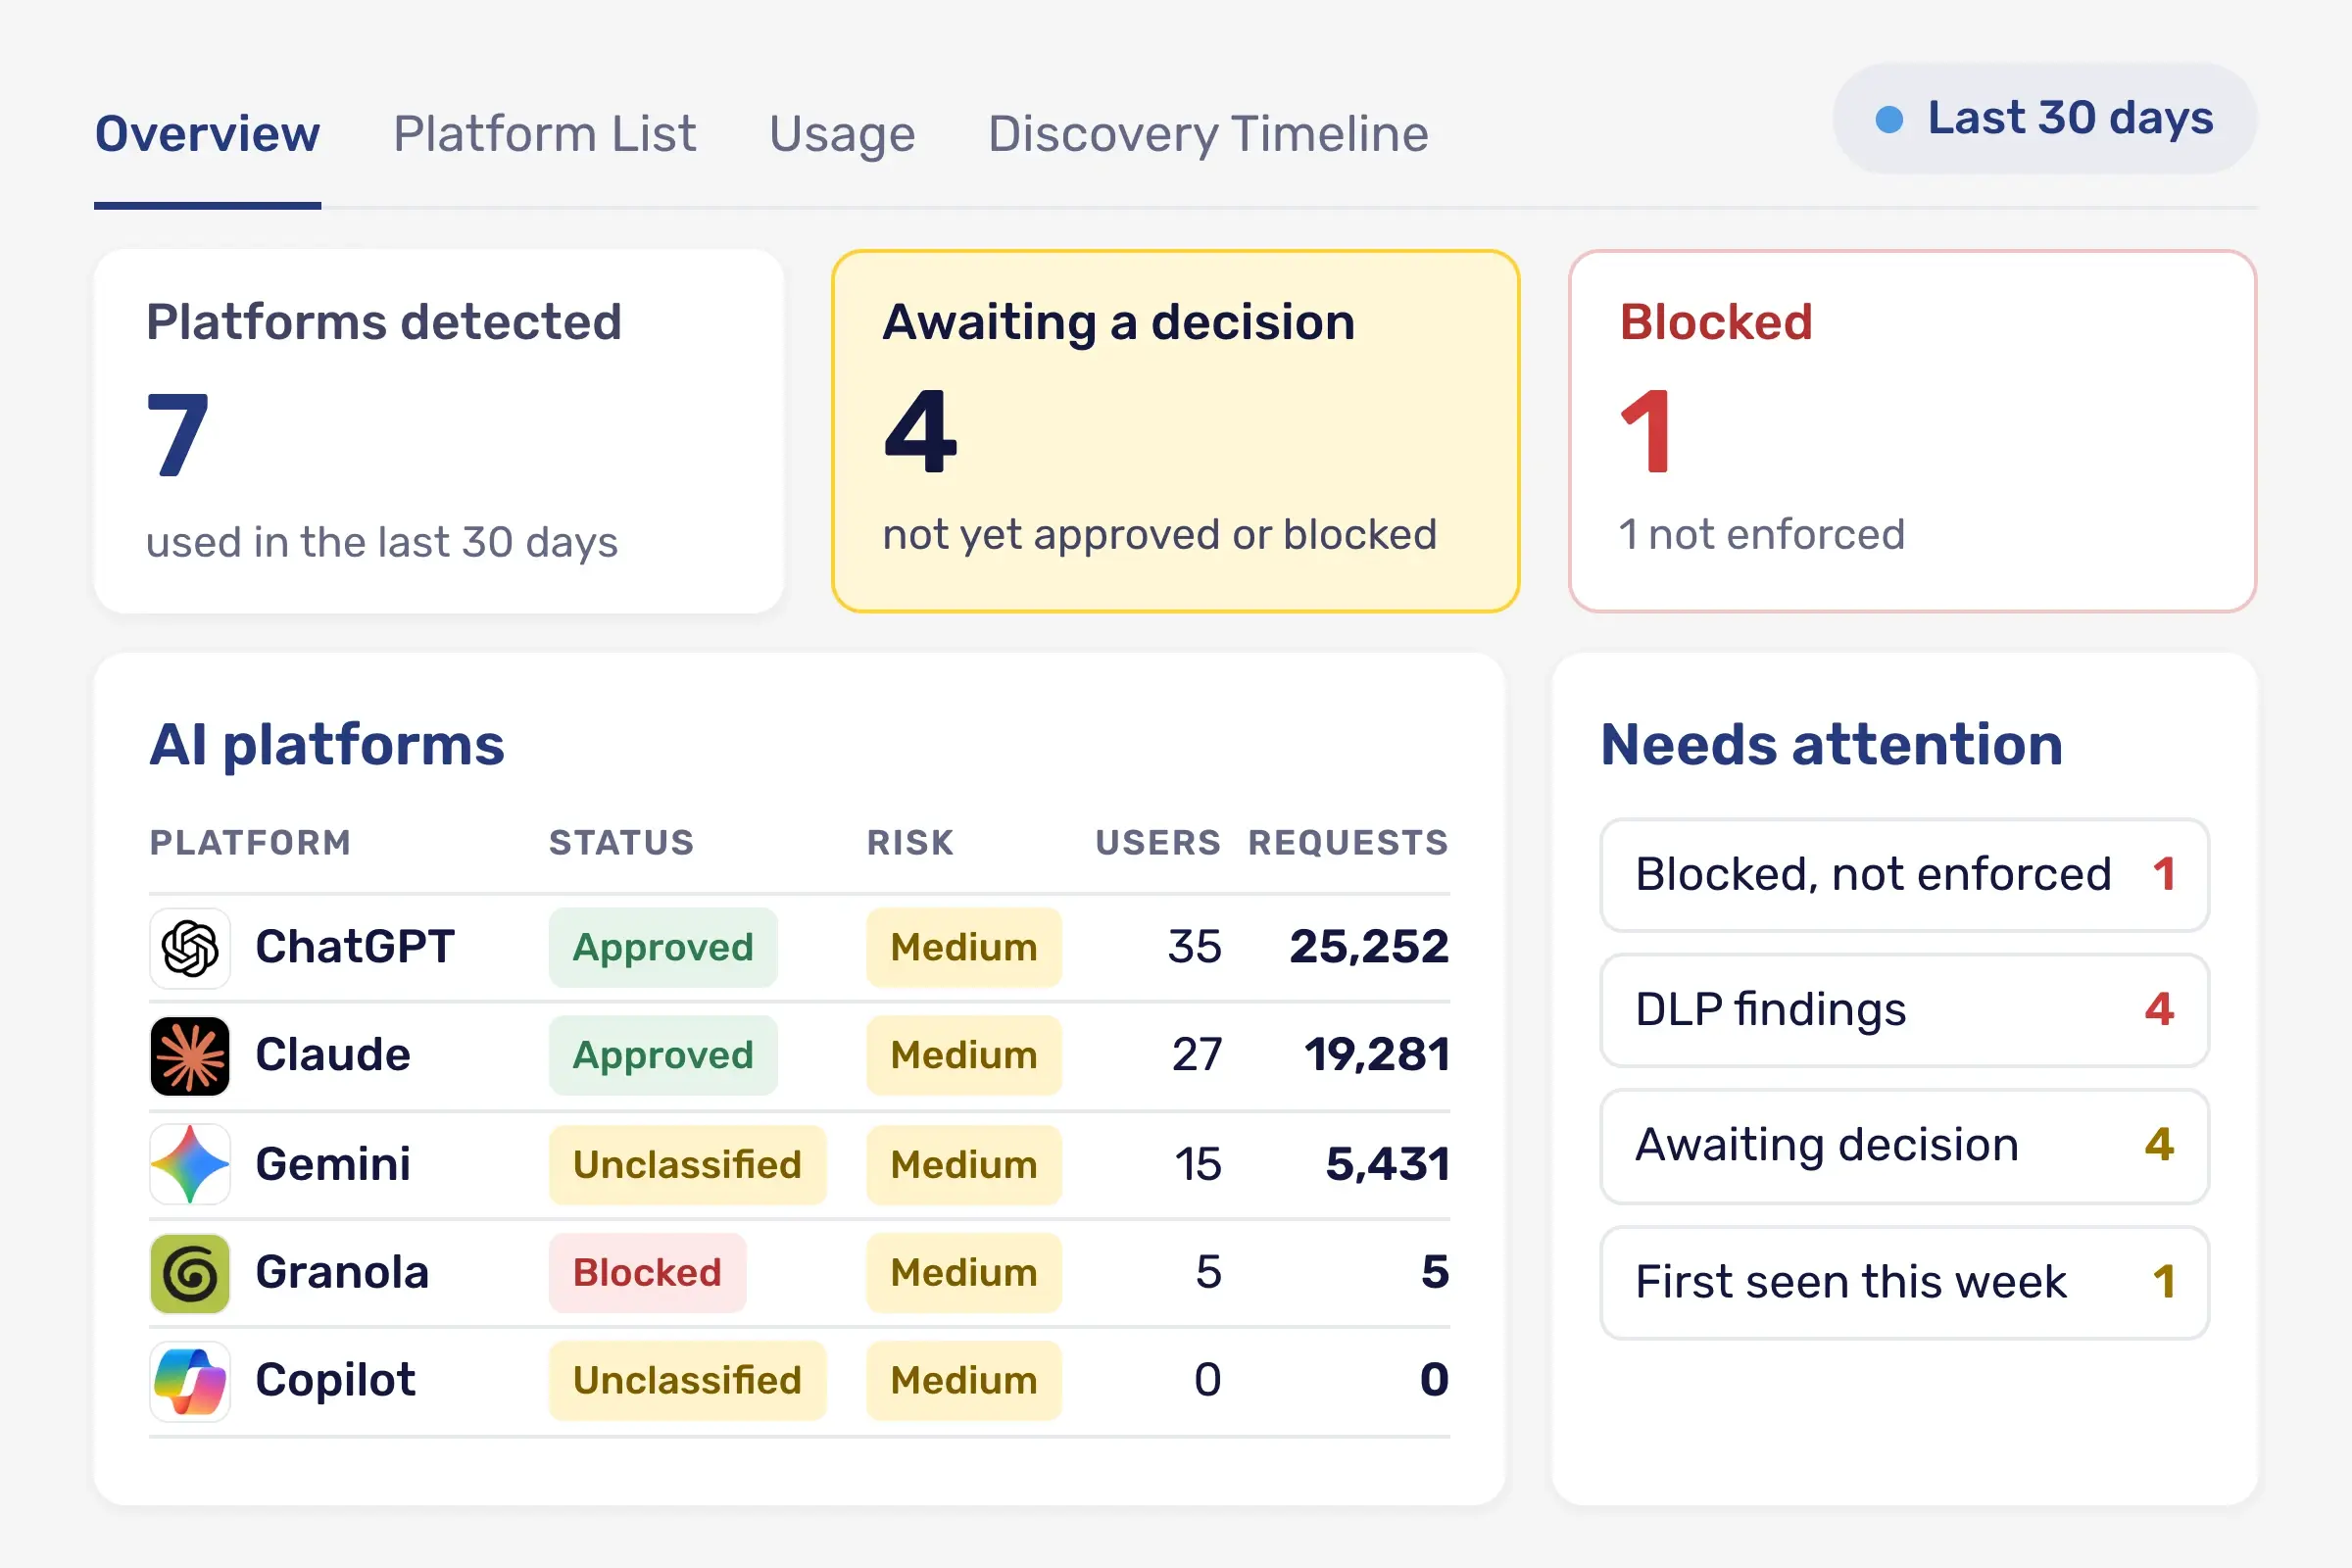
What AI tools are moving through your organization
Who is using AI and how they are using it
How agentic AI is acting and what it's accessing
Which AI tools are putting your data at risk and why
Start your 30-day free trial
CyberHQ.ai Does Not Replace Your Tools
Catches What Other Security Tools Miss
CyberHQ.ai is not a replacement for your CASB, DLP, or secure web gateway. It sits alongside them and reads the one channel they were never built to understand: what a prompt is actually asking a model to do with the data behind it.
Scans every prompt as it is sent, across a continuously expanding watchlist of AI providers.
CyberHQ.ai turns DLP alerts into Jira or ServiceNow tickets automatically, so findings land in the queue your team already works.
Stops a flagged paste and clears the clipboard on cancel when paste protection is enabled.
Every prompt sent to a monitored AI tool, and every paste on sensor-equipped endpoints, for credentials, payment card numbers, US Social Security numbers, and your own custom patterns, plus health, financial-account, and source-code detectors that start in Preview. Matching runs in the browser as the prompt is sent, so a match is flagged then, not after the fact in a log review.
Does CyberHQ.ai block employees from using AI tools altogether?
No. DLP rules target specific data patterns, not the tool itself, and each rule's response is set on its own. Where enabled, Warn prompts a person in the moment instead of stopping their work outright. If one person does need stopping, Act adds per-user hard-block, soft-block, or monitor-only controls.
Can we block a paste, or only get alerted after it happens?
Both, depending on the rule. Each DLP rule runs as Observe, Warn, Redact, or Block, or follows the tenant's default action for its severity when none is set. A flagged paste into an AI tool can be stopped before it reaches the model.
Does enforcement work the same way on Windows and Linux?
On Windows, the sensor prompts on a flagged paste into a verified AI desktop app and clears the clipboard if the person cancels. MacOS can also hard-block the paste. Linux doesn't have paste-blocking yet. It relies on DLP scanning and, where enabled, file-read detection, which surfaces the same violation after the fact.
How do we know a DLP rule is actually working and not just noisy?
Every rule carries a measured precision state, computed from all-time cumulative true and false-positive labels, that moves through unmeasured, healthy, degraded, and monitor-downgraded, so a degraded rule surfaces before analyst trust in the queue erodes. A separate trigger and suppression stat is tracked on a rolling 30-day window.
What is an AI Security Command Platform?
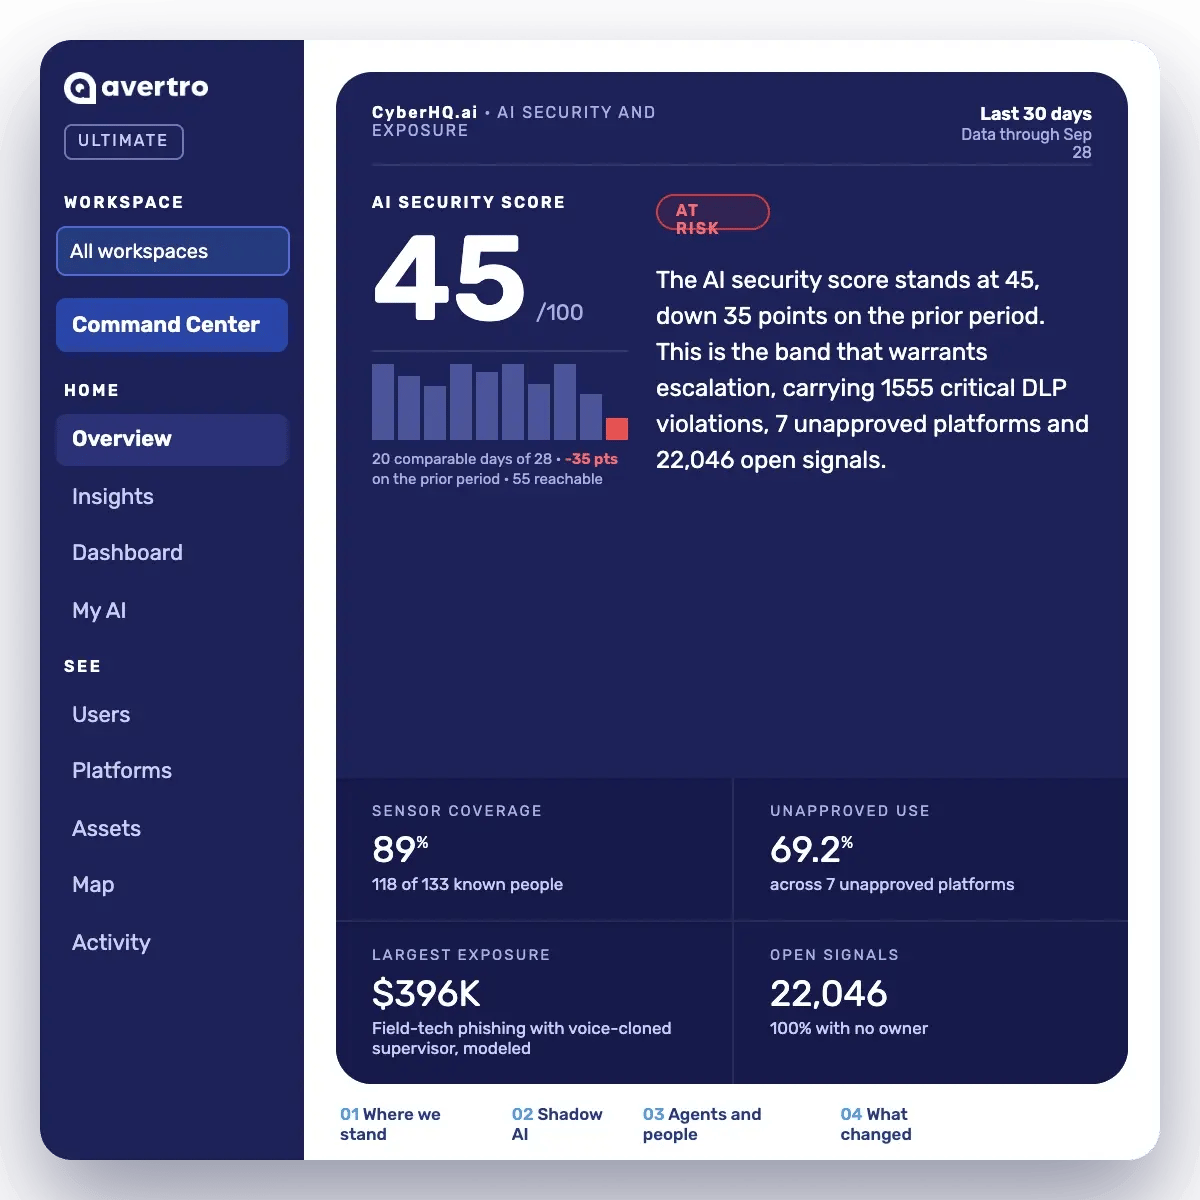
An AI Security Command Platform gives a business a continuous, evidence-backed picture of how AI is actually being used across the organization, from first shadow AI discovery through cost governance, agent oversight, and audit-ready compliance. CyberHQ.ai is built to sit alongside your existing security stack, not replace it, and to answer three questions on an ongoing basis: how is AI being used right now, what does that usage expose you to, and can you prove you have control.
CyberHQ.ai
Measure the Real ROI of AI Adoption Across Your Workforce
Trial CyberHQ.ai for 30-days and get your first meaningful DLP finding in the first 48 hours.