Cyber Resilience Command
Security tools generate data.
CyberHQ® generates answers.
-
Prove resilience with evidence; not assumptions.
-
Know where to invest next; Prioritize by real impact.
-
Quantify your financial exposure; see risk in monetary terms.
Works with what you have. Designed to your environment.
Trusted By
The Questions Leaders Ask
Start With the Question You Cannot Answer Yet
Select a question to see the CyberHQ® use case built to answer it. It does not replace your tools. It makes sense of them.
-
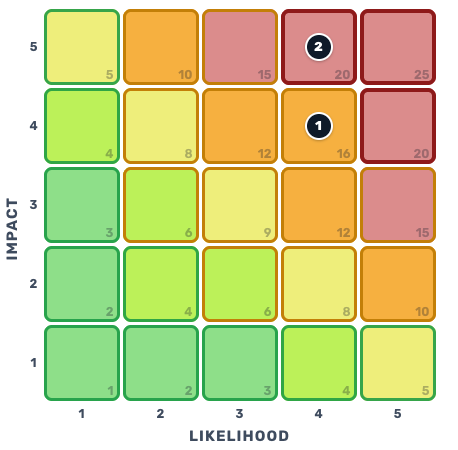
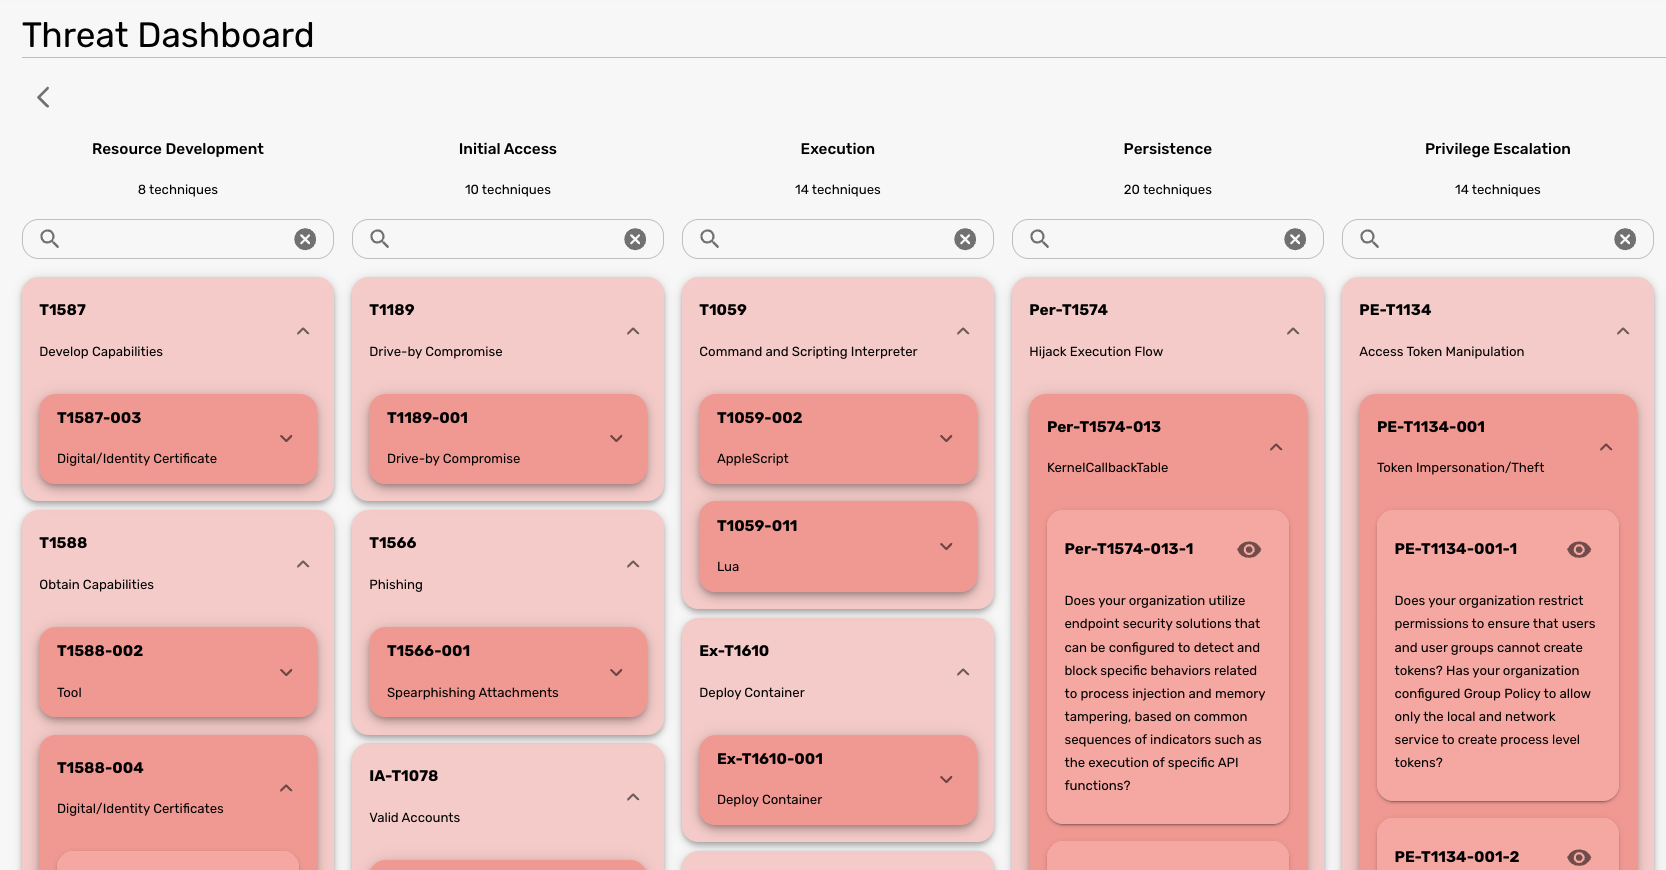
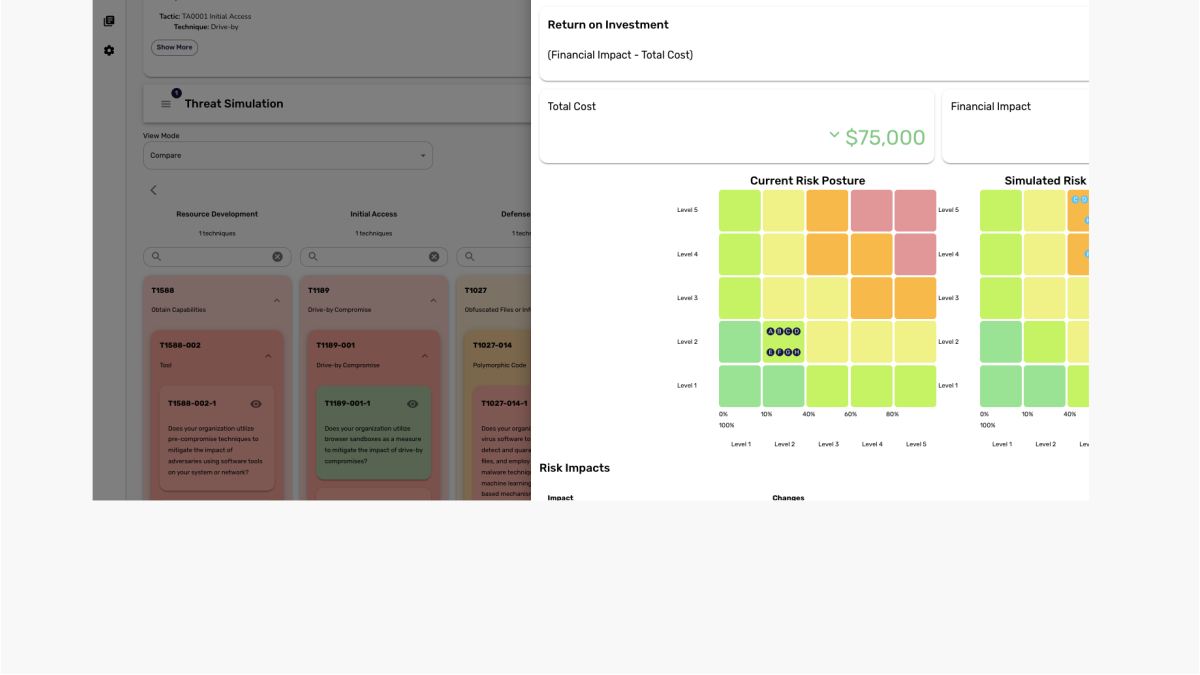
Simulate real-world attack scenarios and map them to business services and dependencies. Prioritize by operational and financial impact, not just severity.
Explore Threat Scenario Planning → -
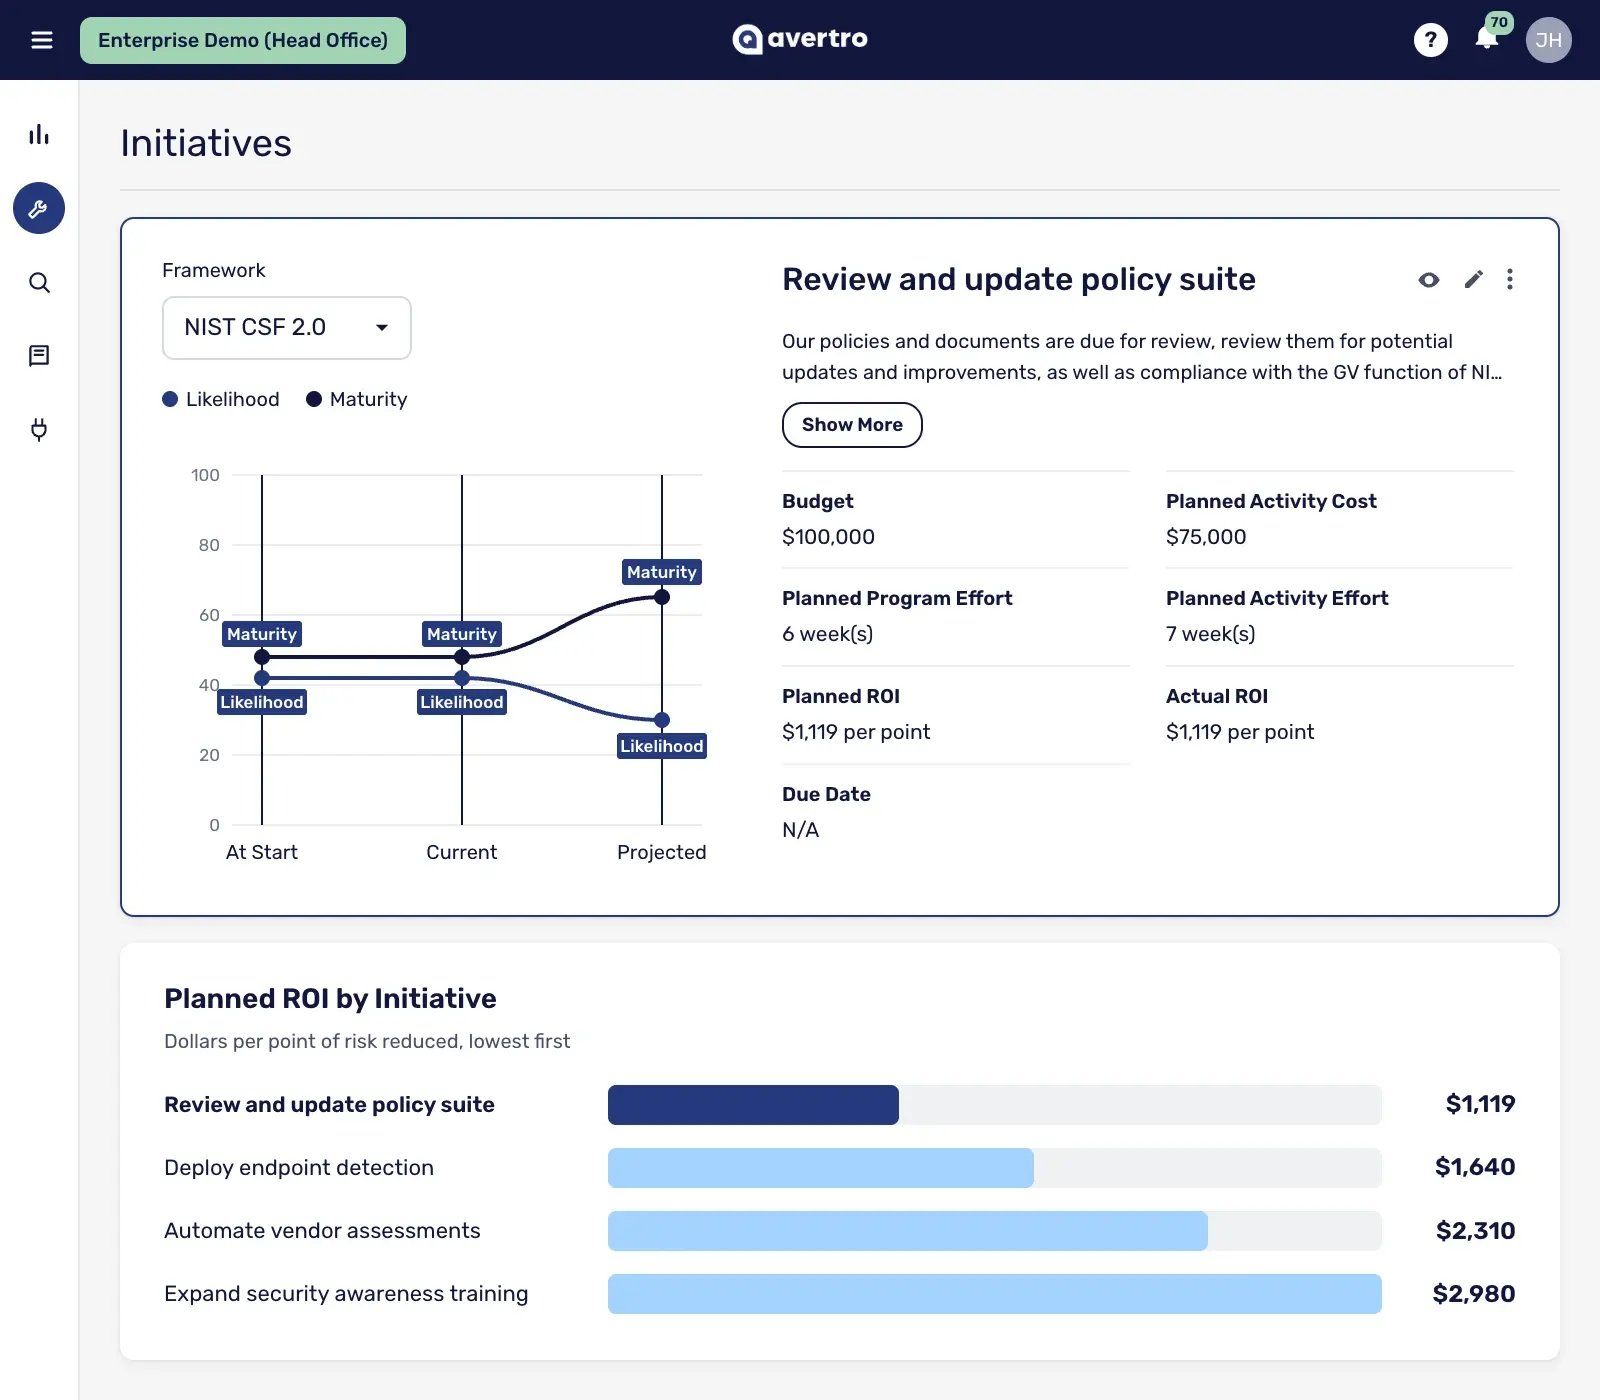
Link security investment directly to risk reduction. Use financial modeling to support budget decisions and give the board data it can approve.
Explore Business Case Justification → -
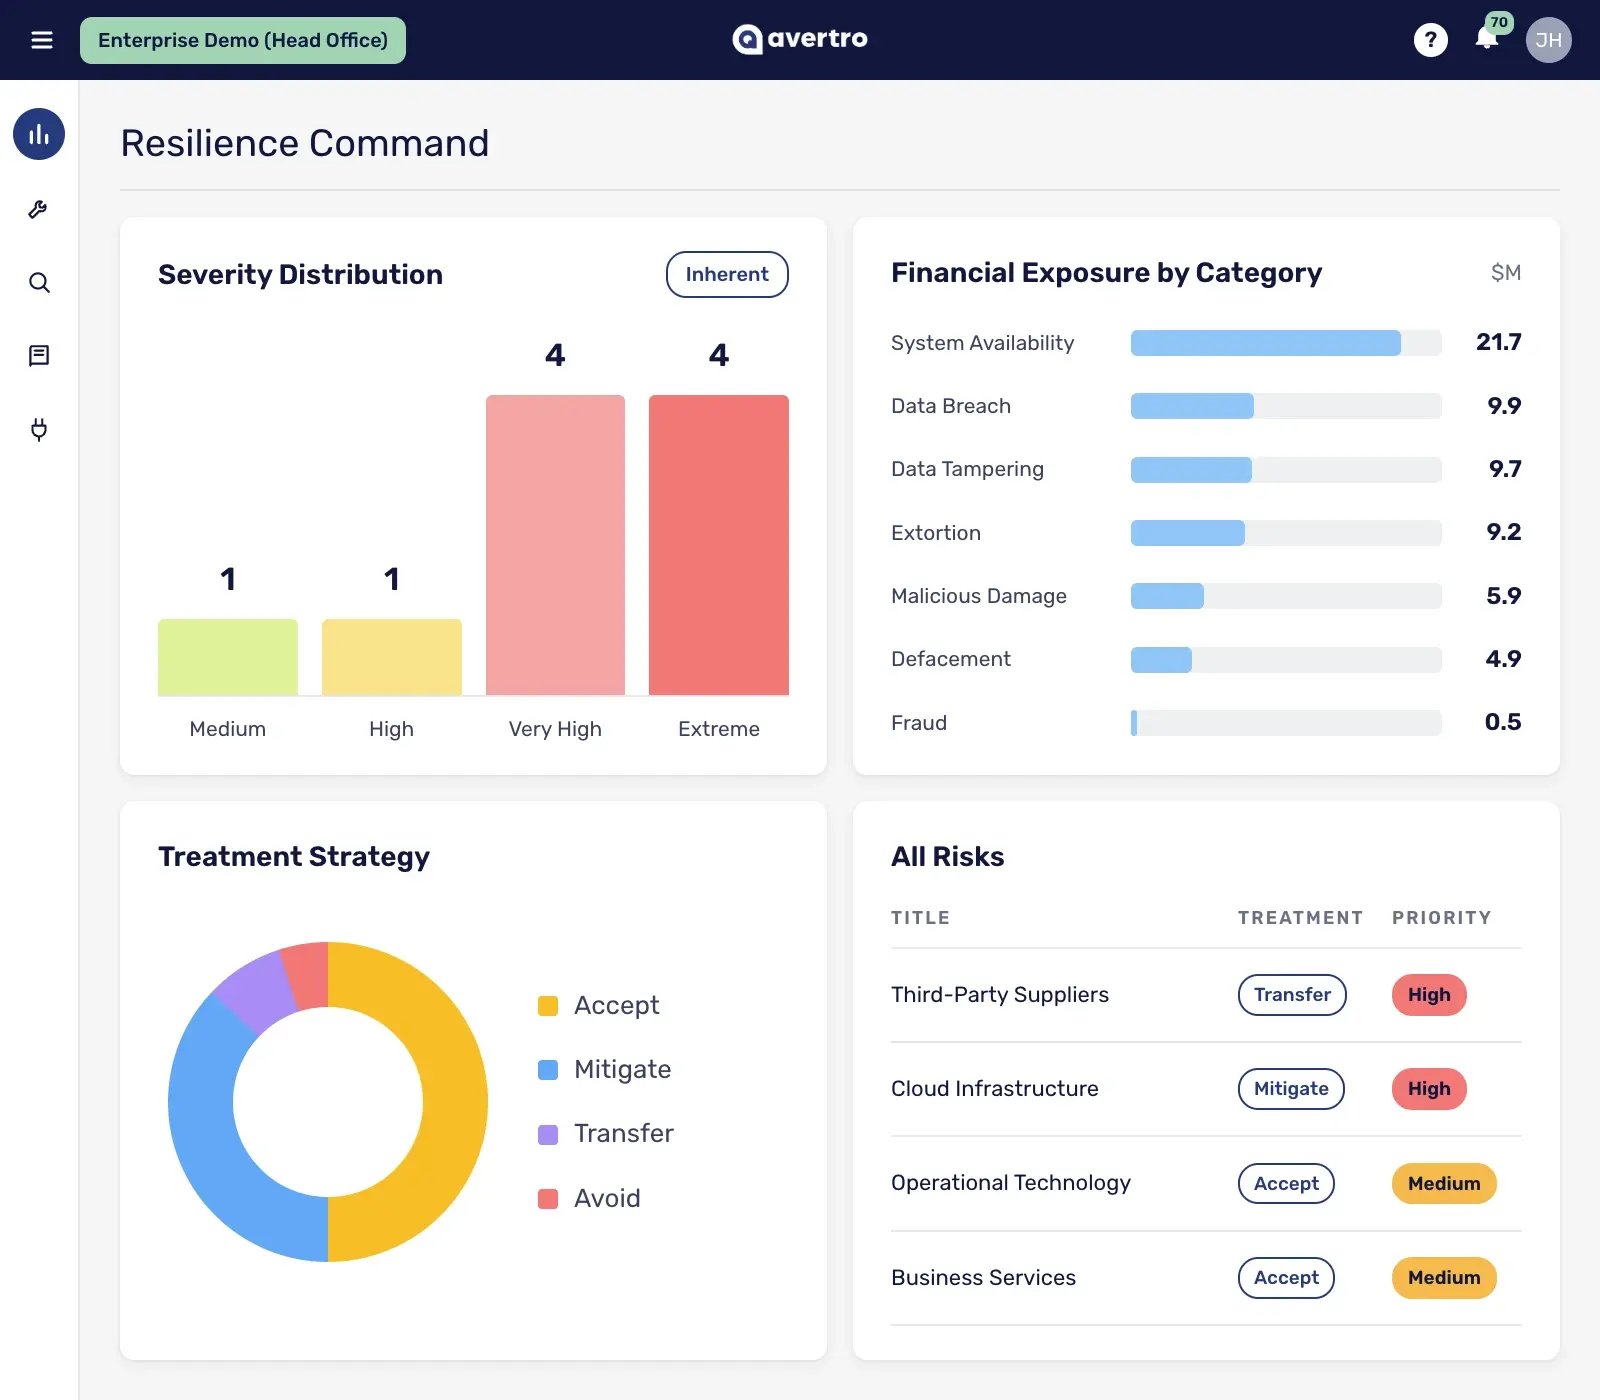
Report in financial and operational terms, with clear visibility into risk exposure, investment effectiveness, and resilience posture.
Explore Executive & Board Visibility → -
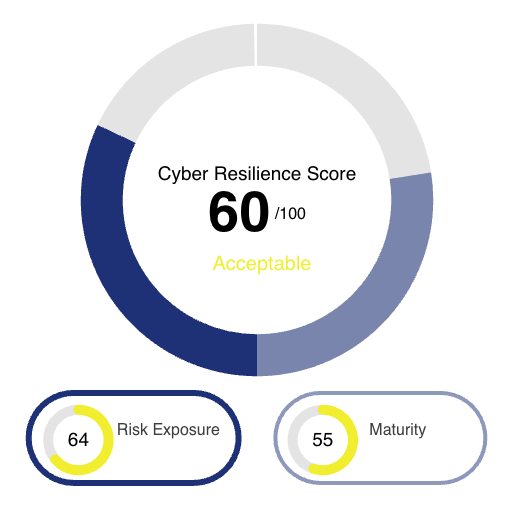
See controls, vulnerabilities, and their effectiveness continuously, mapped to business services, so you know what matters to the business.
Explore Security Posture Management → -
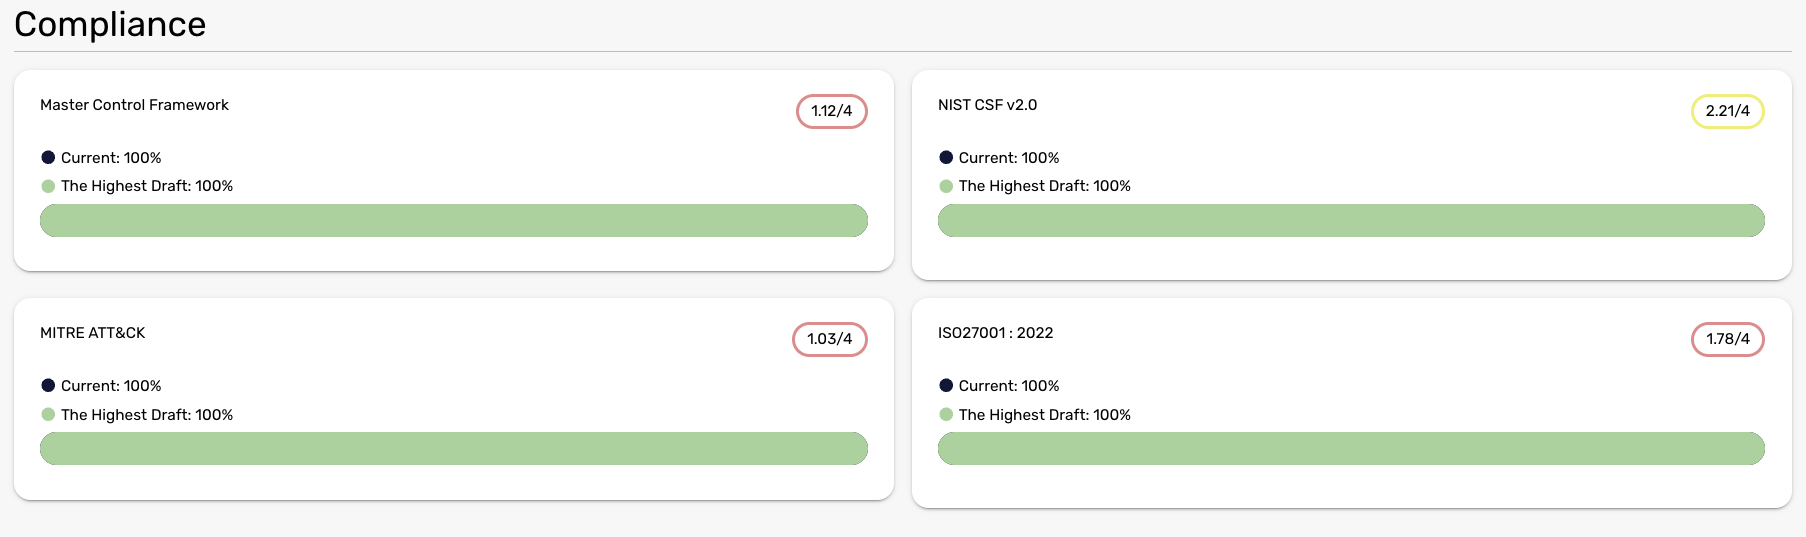
Automate compliance across frameworks and align it to real business risk, so every compliance activity is tied to reduced exposure.
Explore Compliance & Assurance → -
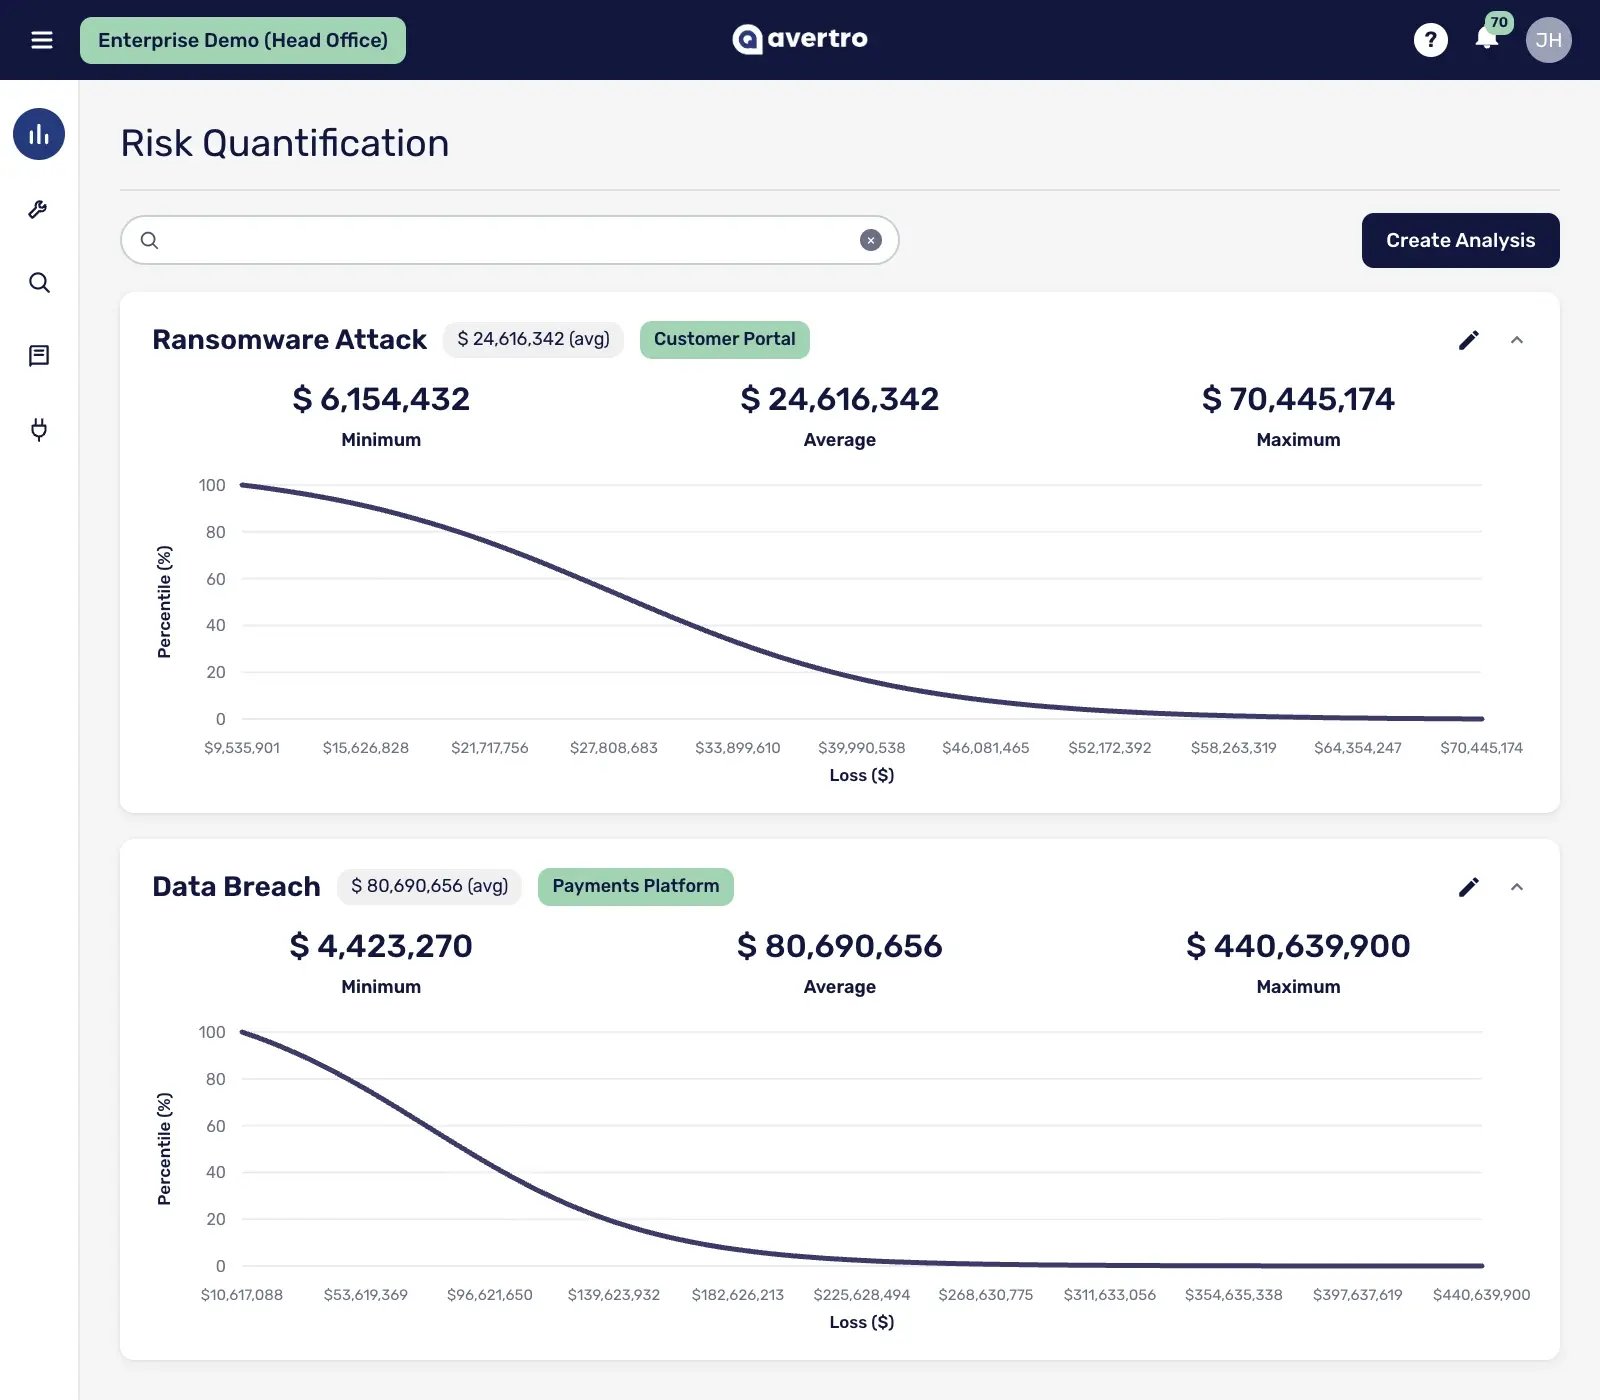
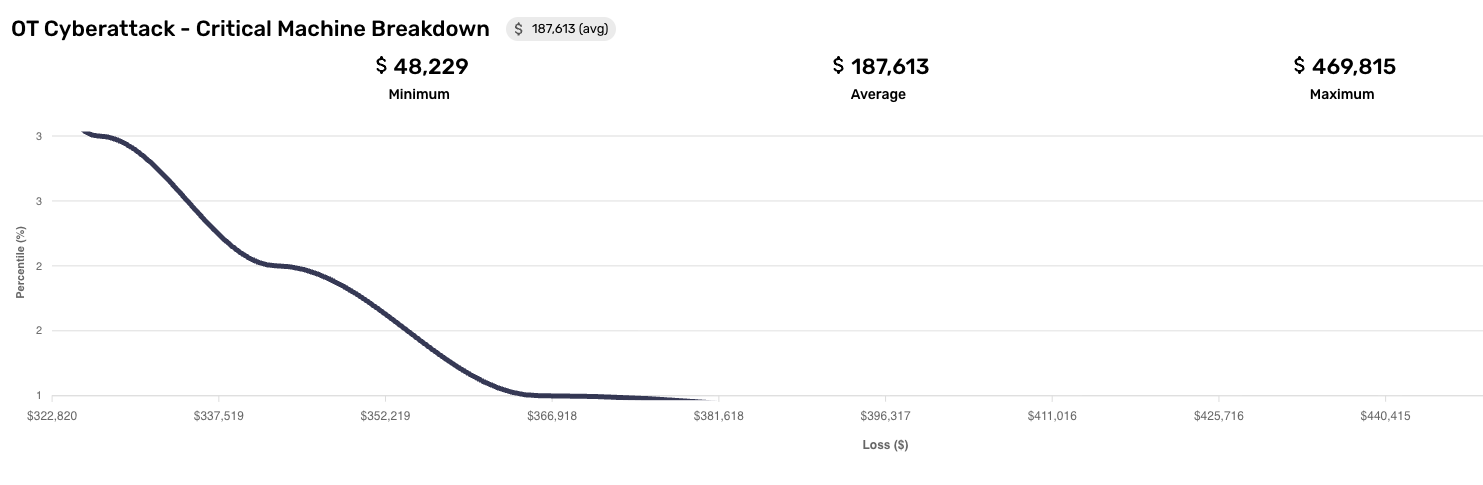
Quantify cyber risk exposure in monetary value and translate technical risk into business impact. Base decisions on financial exposure.
Explore Cyber Risk Quantification → -
Map third-party risk to critical services and operations. See systemic and supply chain exposure, and prioritize by business dependency and impact.
Explore Third-Party & Supply Chain Risk →
- Business Case Justification Justify cybersecurity investments with measurable business impact
- Executive & Board Visibility Communicate cyber risk in a way the business understands
- Compliance & Assurance Turn compliance into a driver of real resilience
- Cyber Risk Quantification Understand cyber risk in financial and operational terms
- Security Posture Management Understand how your security posture impacts critical business functions
- Threat Scenario Planning Understand how cyber attacks impact real operations and services
- Third-Party & Supply Chain Risk Understand how external dependencies impact business resilience
Simulate real-world attack scenarios and map them to business services and dependencies. Prioritize by operational and financial impact, not just severity.
Explore Threat Scenario Planning →Link security investment directly to risk reduction. Use financial modeling to support budget decisions and give the board data it can approve.
Explore Business Case Justification →Report in financial and operational terms, with clear visibility into risk exposure, investment effectiveness, and resilience posture.
Explore Executive & Board Visibility →See controls, vulnerabilities, and their effectiveness continuously, mapped to business services, so you know what matters to the business.
Explore Security Posture Management →Automate compliance across frameworks and align it to real business risk, so every compliance activity is tied to reduced exposure.
Explore Compliance & Assurance →Quantify cyber risk exposure in monetary value and translate technical risk into business impact. Base decisions on financial exposure.
Explore Cyber Risk Quantification →Map third-party risk to critical services and operations. See systemic and supply chain exposure, and prioritize by business dependency and impact.
Explore Third-Party & Supply Chain Risk →The platform
The Cyber Resilience Command Layer Your Stack Has Been Missing
CyberHQ® connects risk, threat, compliance, and business context into a single, intelligence-driven decision layer. It makes sense of technical noise so you can validate cyber effectiveness, prove defensible resilience, and optimize security-per-dollar with absolute confidence.
Make Sense of Your Exisiting Security tools
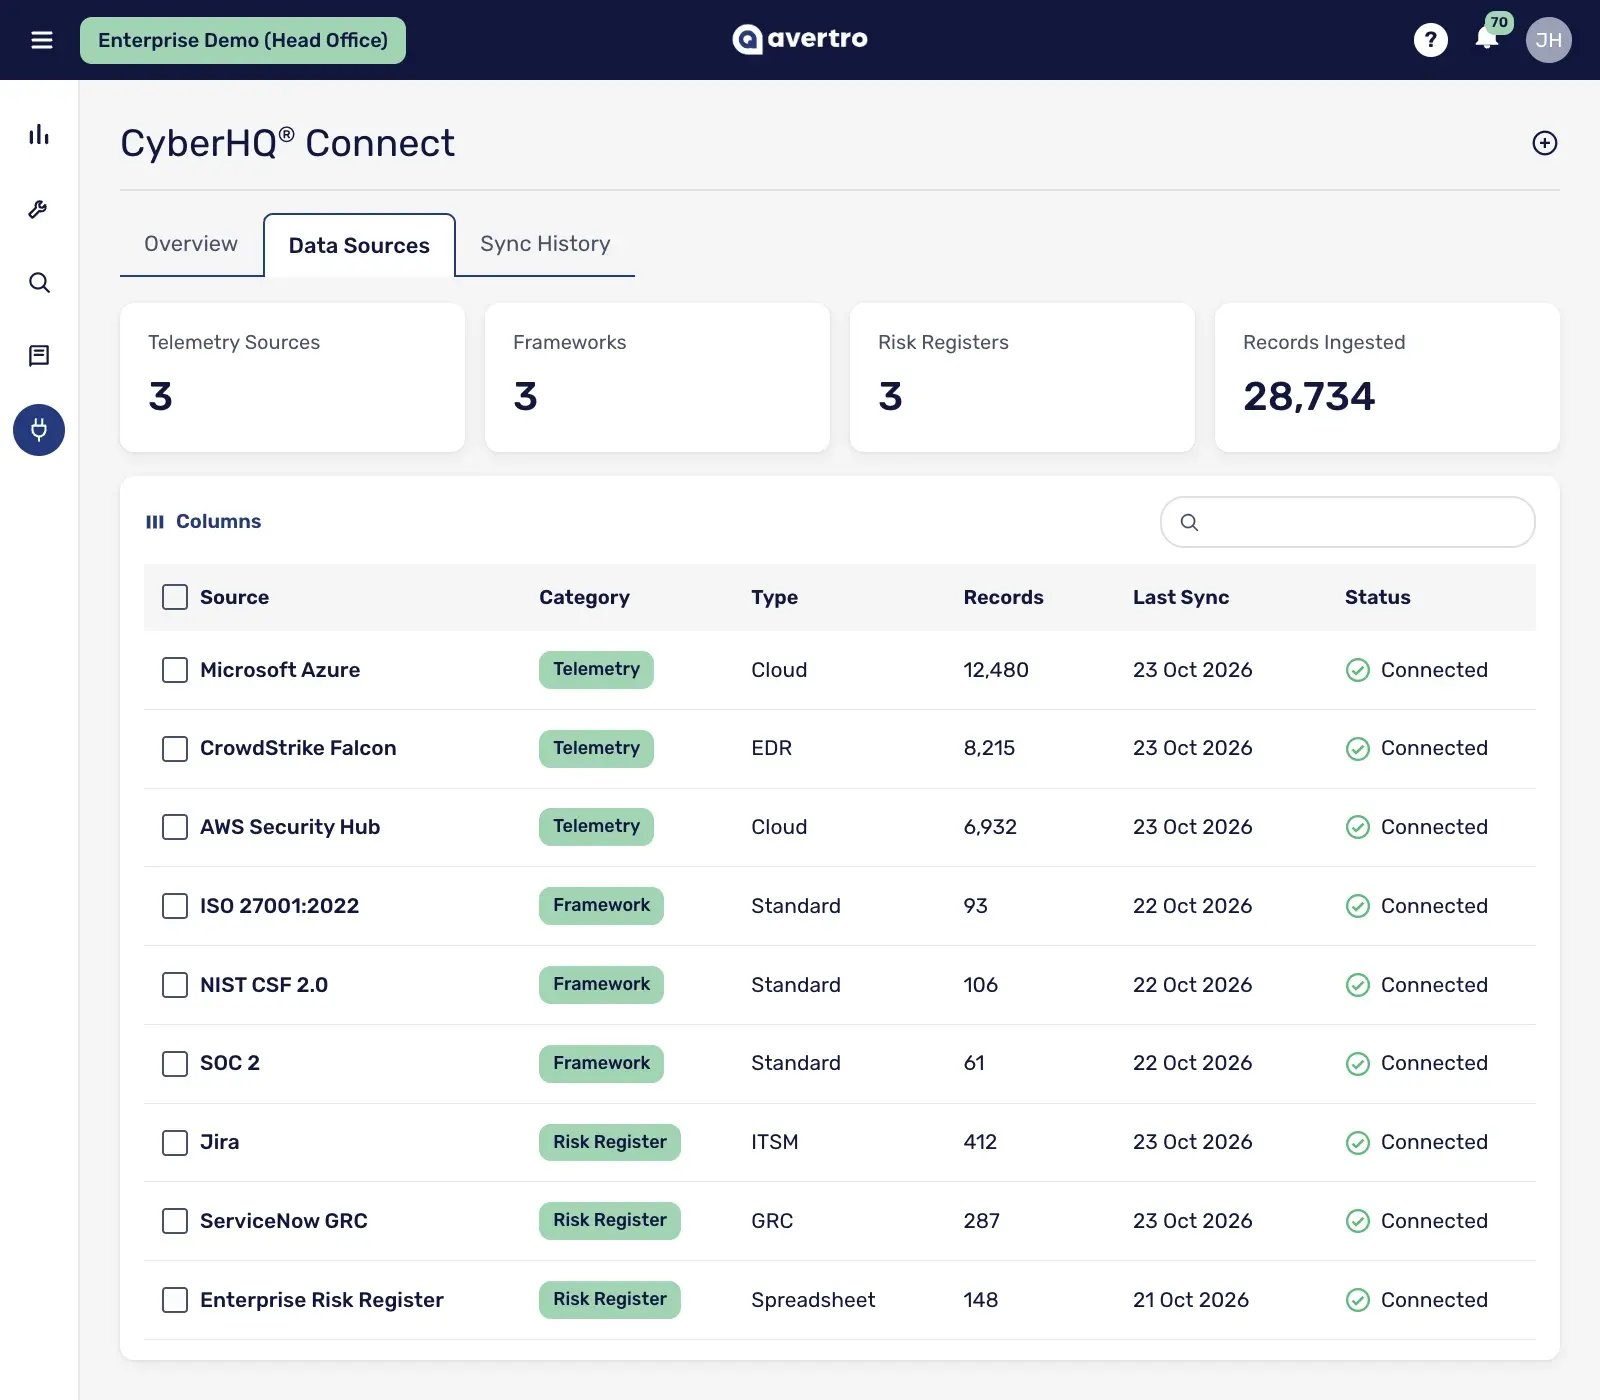
CyberHQ® is not a traditional security tool. It sits above your existing ecosystem — integrating with any system via API — to transform your fragmented data into a single, intelligence-driven decision layer.
It does not replace your tools. It makes sense of them.
CyberHQ® Connect
SIEM · EDR / XDR · Vuln Mgmt · Cloud Security · ITSM · Threat Intel · OT / ICS · GRC / Risk · IoT Security
75 %
reduction in manual compliance effort
90 %
reduction in compliance costs
100 +
integrators & connectors
20 +
supported compliance frameworks
How it works
From Security Data to Resilience Ccommand in Five Steps
Ingest telemetry, frameworks, and risk registers through CyberHQ® Connect. No rip-and-replace.
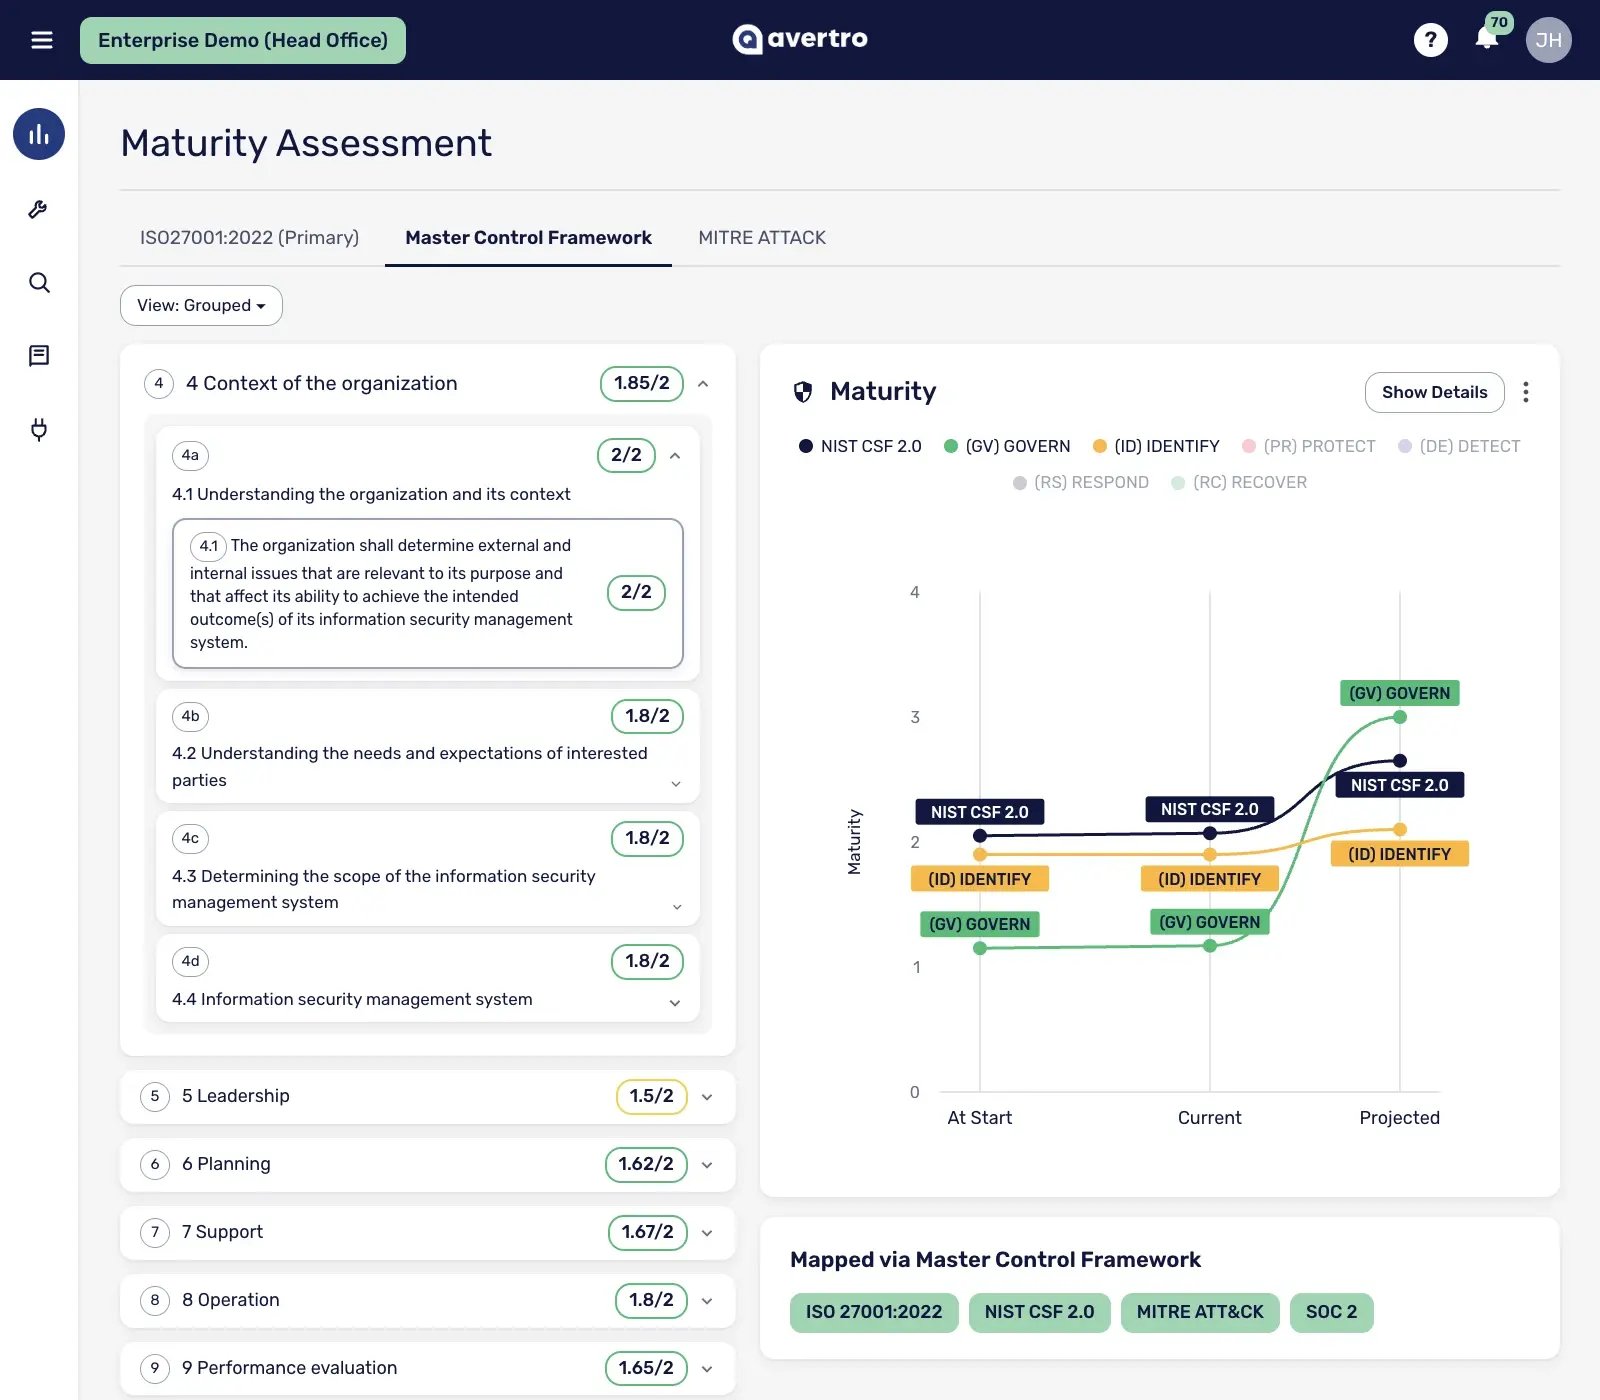
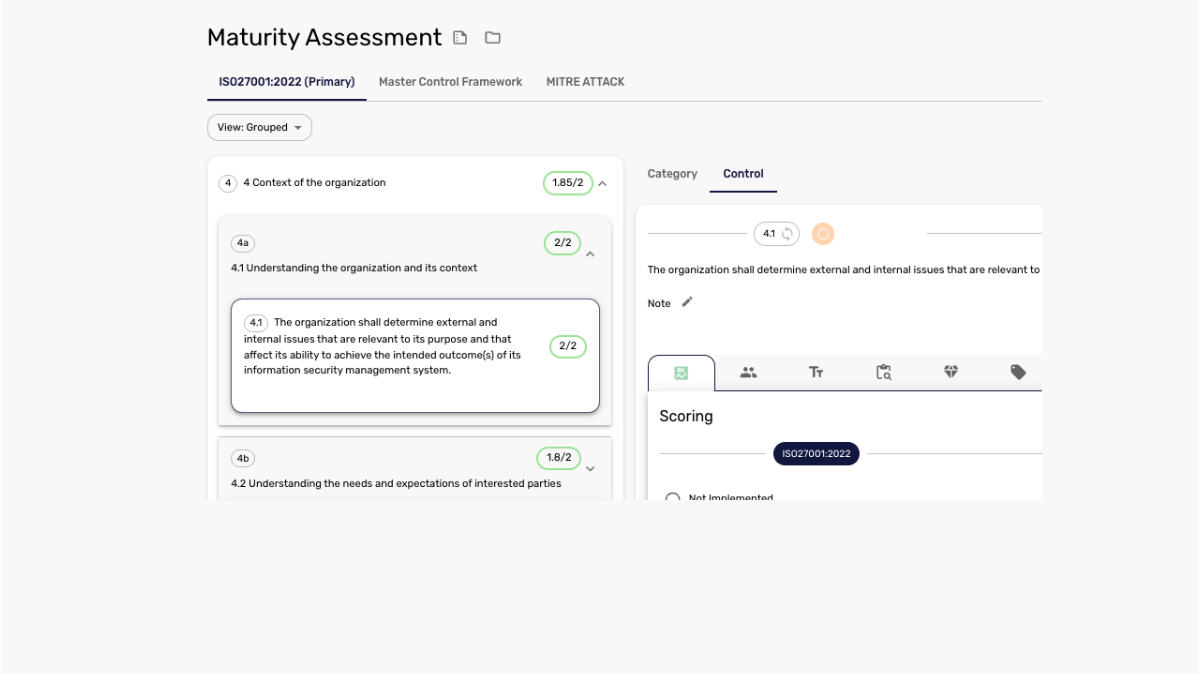
Evaluate control effectiveness and defensive capability. Assess once against the Master Control Framework (MCF).
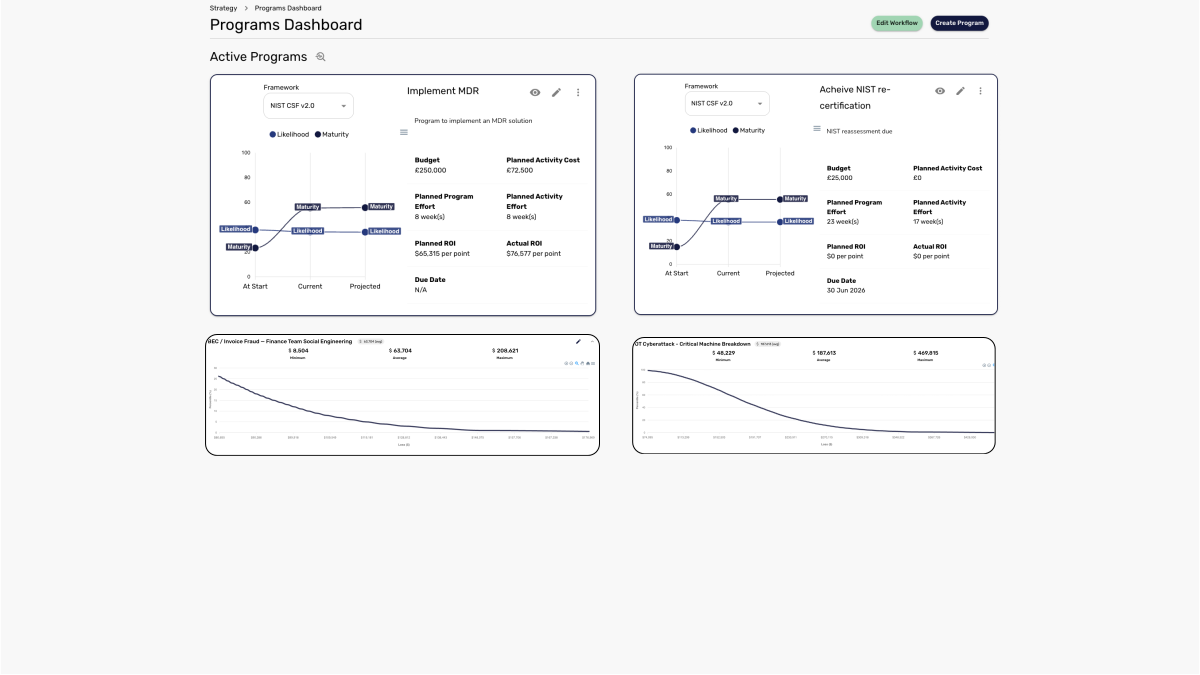
Model cyber risk exposure and financial impact, with threat scenarios mapped to your business services.
Identify the initiatives that reduce the most risk per dollar. Optimize Security-per-Dollar.
Give executives and the board governance-ready reporting and confidence they can defend.
Frequently Asked Questions
What is CyberHQ®?
CyberHQ® is Avertro's Cyber Resilience Command Platform. It sits above your existing cybersecurity stack, connects your tools via API, and transforms fragmented data into a unified intelligence layer. As a result, it enables you to quantify risk, prioritize investments, and govern cyber as a strategic business function.
Does CyberHQ® support my compliance framework?
CyberHQ® supports 20+ global frameworks including NIST CSF, ISO 27001, SOC 2, Essential Eight (AU), DORA (EU), NIS2 (EU), and more. Assess your controls once and CyberHQ®'s AI automatically maps them across multiple frameworks.
Can CyberHQ® quantify cyber risk in financial terms?
Yes. CyberHQ®'s Cyber Risk Quantification (CRQ) capability translates cyber threats into monetary exposure using industry-standard loss models and your organization's specific business context.
How long does implementation take?
CyberHQ® is designed for rapid, low-friction deployment. CyberHQ® Connect's pre-built API connectors enable real-time data ingestion without disrupting your existing tools or workflows.
How is CyberHQ® different from traditional GRC platforms?
Traditional GRC platforms are static, backward-looking, and focused on compliance tracking. CyberHQ® is real-time, integrated, and decision-focused, connecting risk, threat, compliance, and business context into a single command layer.
What environments does CyberHQ® support?
CyberHQ® provides unified cyber risk visibility across IT, OT (operational technology / ICS), and IoT environments.
CyberHQ®
See CyberHQ® Configured To Your Environment
Book a 30-minute interactive session to see how CyberHQ® integrates with your existing tools, frameworks and environment.
No lock-in. No rip-and-replace. Works with what you have.